
Spacebears Claims Ransomware Attack on Gestordes
Summary
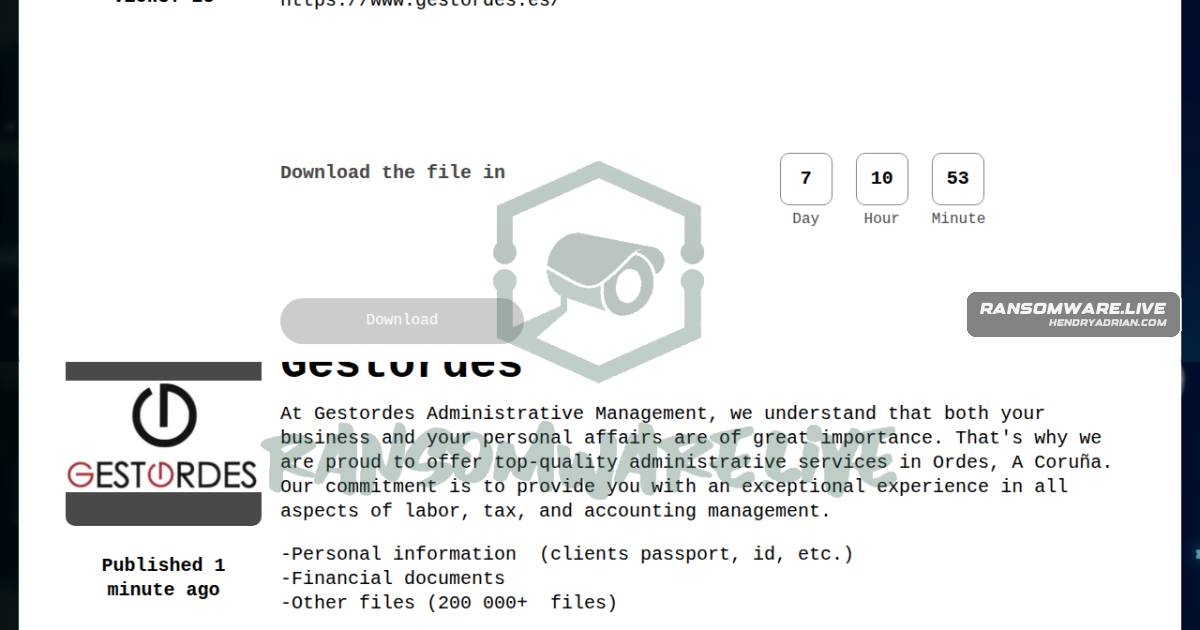
Ransomware.live reports that spacebears claims to have attacked Gestordes in Spain, exposing passports, IDs, financial documents and more than 200,000 files. The claim is unconfirmed.
Key points
- The spacebears ransomware group is alleged to have claimed an attack on Gestordes, an administrative services provider in Spain.
- The claim says exposed data included clients’ passports and IDs, financial documents, and more than 200,000 files.
- The post alleges disruption in Spain but provides no independent confirmation of compromise, exposure, or disruption.
- The claim is attributed to a spacebears leak-site listing and monitored by ransomware.live.
Article Details
- Victim
- Gestordes
- Claim Date
- 2026-05-03
- Encryption Status
- Unknown
- Exfiltration Status
- Claimed; not independently verified
- Exfiltrated Data
- The group reportedly claimed exposure of client passports and ID documents, financial documents, and other files. The source says it cannot confirm the claim.
- Exfiltrated Size
- More than 200,000 files were reportedly affected; the source does not establish that all were exfiltrated.
- Ransom Demand
- Not disclosed
- Leak Status
- The group reportedly claimed the data were exposed; the claim and authenticity of the data are unverified.