
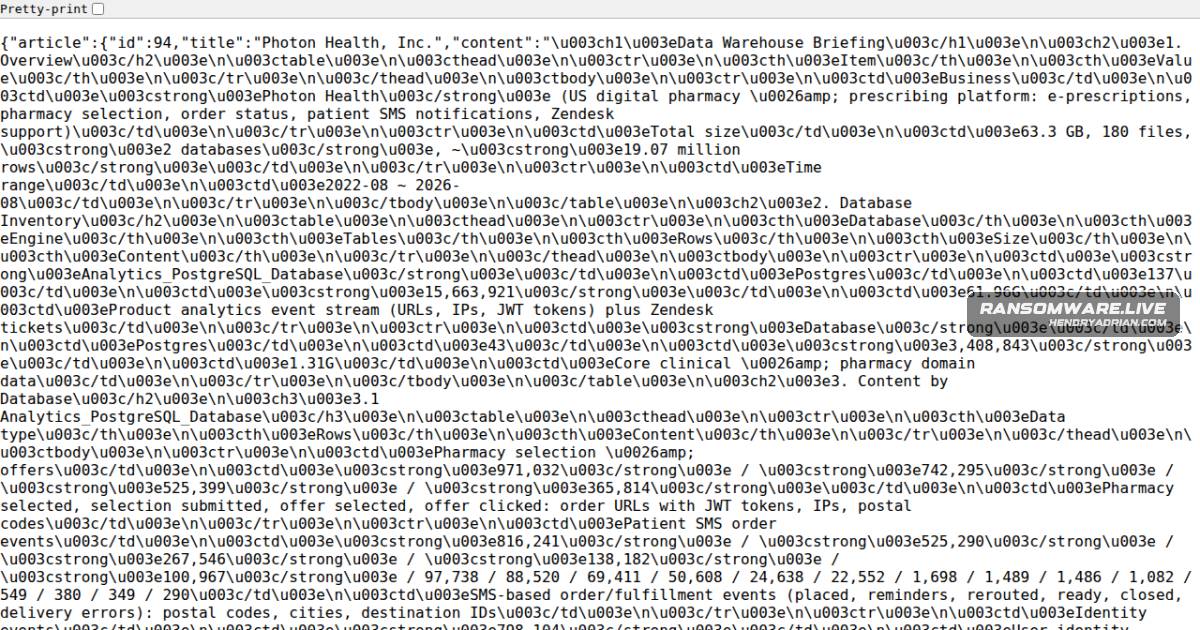
Direwolf Claims Photon Health, Inc. as Ransomware Victim
Ransomware.live lists Photon Health, Inc. as a direwolf ransomware claim, alleging disruption, encryption and potential data exposure. The post says the claims are unconfirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2793 articles
Ransomware.live lists Photon Health, Inc. as a direwolf ransomware claim, alleging disruption, encryption and potential data exposure. The post says the claims are unconfirmed.
Ransomware.live lists an unconfirmed Incransom claim naming nyklawfirm[.]com and nyk[.]ae in the UAE; it alleges encrypted files and operational disruption. The article says the claim's accuracy is unconfirmed.
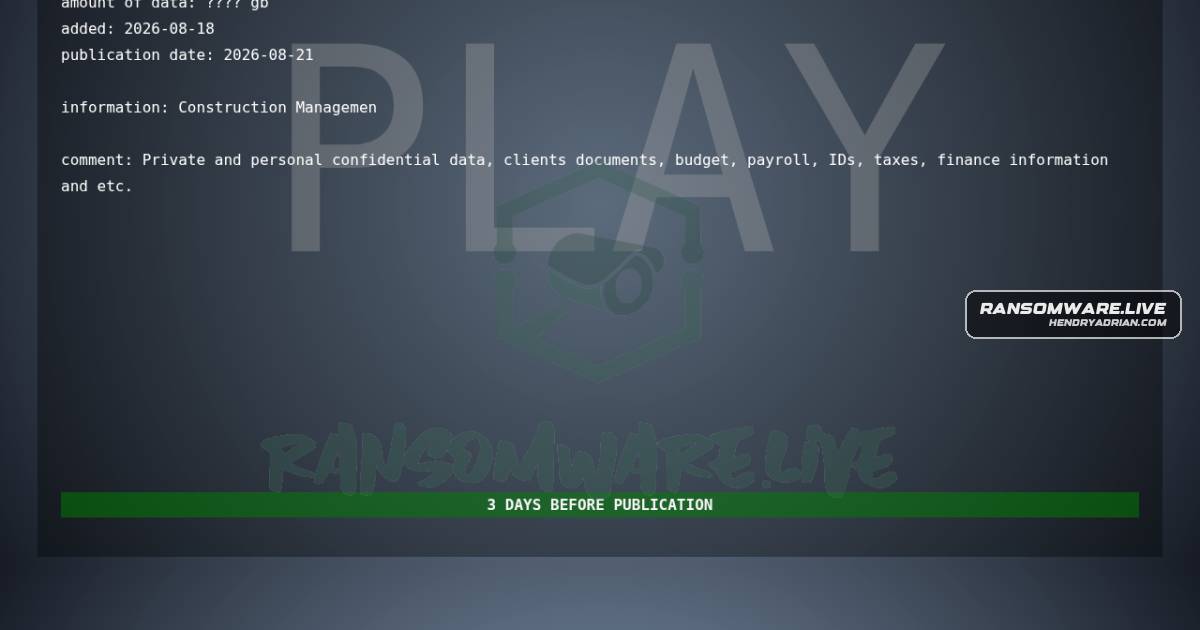
A ransomware.live monitoring record attributes an unverified claim against Coltrane Systems to the Play ransomware group, alleging encryption and operational disruption in the United States.

SilentRansomGroup reportedly claimed a second attack on Troutman Pepper Locke within a year, alleging physical access and ransomware deployment. The post says the claims are unconfirmed.

An Unverified ransomware.live record says DragonForce claimed R&D Machine and Engineering as a victim. The claim was published on August 18, 2026; the post says it cannot confirm the information.
A ransomware.live monitoring record attributes an unconfirmed ransomware claim against ADL Embedded Solutions to securotrop. The record lists the case as AWAITING and claims 925 GB of data.
Ransomware.live records an incransom claim targeting SSF International GmbH in Germany. The group’s claim alleges operational disruption; the post says it could not confirm the information.
A ransomware.live monitoring post attributes a June 26, 2026, claim of a 416 GB data leak at Mauritius-based SpearFin Ltd to incransom. The post says the material includes KYC/AML records and financial and corporate documents; the claim is unconfirmed.
A ransomware.live-monitored post attributes to Akira a claim that it will soon upload Borchert & LaSpina corporate data. The post says personal, financial and legal information is expected, but the claim is unconfirmed.
Ransomware[.]live lists Honduras contractor BOMOHSA as a gunra ransomware target on Aug. 18, 2026. The post attributes the claim to gunra and says it is unconfirmed; no official statement is included.
A ransomware.live-monitored record attributes a ransomware claim against Berlin Brandenburgische Wohnungsbaugenossenschaft in Germany to Qilin. The post says disruption and potential data exposure are alleged but cannot be independently confirmed.
A ransomware.live record says ShinyHunters issued Logitech/Streamlabs a final warning to respond by Aug. 21, 2026, or face a data leak and disruptive actions. The claim is unconfirmed.
A ransomware.live monitoring record attributes a ransomware claim naming WindRose Health Network, a healthcare provider in Indiana, to Storm. The claim is unconfirmed.
The ransomware actor emperador claims it accessed and encrypted systems at Brazil’s Prefeitura Municipal de Arcos and exfiltrated 462.3 MB. The claim threatens publication and permanent loss unless the victim responds within 14 days; it is unconfirmed.
Incransom claims it leaked 1.2 TB of Foresee Pharmaceuticals data, including regulatory, R&D, financial and clinical-study materials. The claim is unconfirmed.
Ransomware.live records Storm’s unverified claim targeting Westco Motors Cairns, an Australian dealership. The post says customers and business operations were affected, but provides no independent confirmation.
Ransomware.live lists U.S. manufacturer Standard Tool & Die in a Storm ransomware-group claim published Aug. 17, 2026. The post says the claim is unverified.
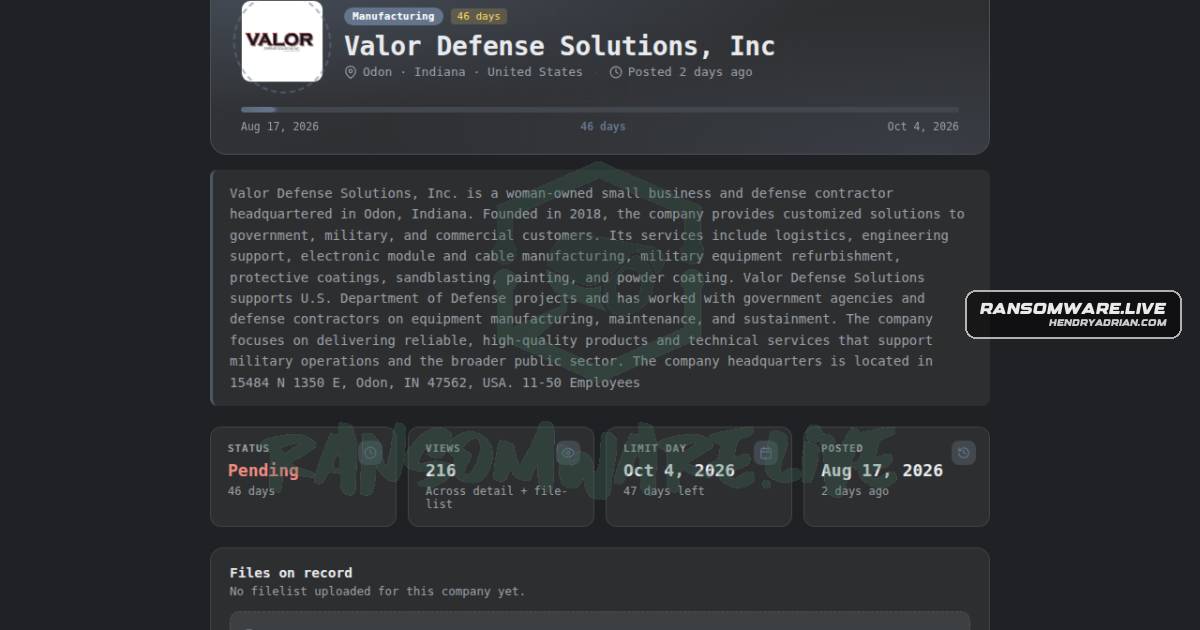
Ransomware.live reports that Storm claimed Valor Defense Solutions, a U.S. defense contractor, as a victim and alleged operational disruption. The claim is unconfirmed.
Qilin reportedly claimed to target the University of the West Indies in Trinidad and Tobago. The monitoring post says the claim involved system disruption and data access, but notes the information is unconfirmed.
Ransomware.live records a Qilin claim naming White-Daters & Associates, Inc., a US professional-services firm. The post cites a Qilin leak-site source; the claim has not been independently confirmed.
Ransomware.live records Qilin's claim naming Germany's GSW Gemeinschaftsstadtwerke GmbH as a victim. The post says the claim was published on August 17, 2026, but its accuracy is unconfirmed.
Ransomware.live reports that Global Secret Group claimed The Rubber Group in New Hampshire was affected, alleging 162 GB across 207,203 files and 21,624 folders. The claim is unconfirmed.
Ransomware.live lists Lansing Urgent Care as a victim claimed by incransom. The post says operations were disrupted across multiple Lansing-area locations, but states that it cannot independently confirm the claim.
A ransomware.live monitoring post attributes an unconfirmed ransomware claim targeting BMW Group to xpl0itrs. The post says the claim was published on August 17, 2026; the incident is not independently confirmed.