
Play Ransomware Group Claims Coltrane Systems Incident
Summary
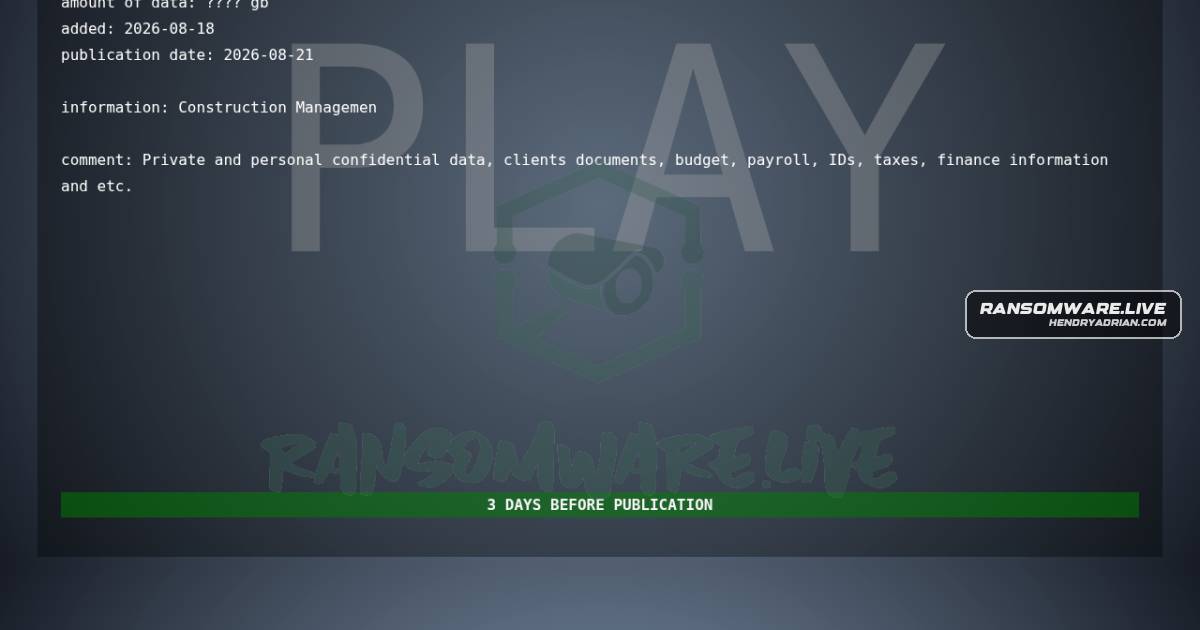
A ransomware.live monitoring record attributes an unverified claim against Coltrane Systems to the Play ransomware group, alleging encryption and operational disruption in the United States.
Key points
- The record names Coltrane Systems as the victim and Play as the ransomware actor.
- The group’s claim alleges unauthorized encryption and operational disruption in the United States; the article says it cannot confirm the claim.
- The record lists August 18, 2026, as the discovery and publication date.
Article Details
- Victim
- Coltrane Systems
- Encryption Status
- Reported, but unconfirmed; the article says the incident is based on public claims by the ransomware group.
- Exfiltration Status
- Unknown
- Ransom Demand
- Unknown
- Leak Status
- Unknown