
Qilin Claims Ransomware Attack on Arnold Center
A ransomware.live monitoring post says Qilin claimed to target Arnold Center in the US and encrypt data, disrupting system access. The post says the claim has not been independently confirmed.
Monitors ransomware victims, threat groups, leak-site activity, and newly disclosed ransomware incidents.
2771 articles
A ransomware.live monitoring post says Qilin claimed to target Arnold Center in the US and encrypt data, disrupting system access. The post says the claim has not been independently confirmed.
A ransomware.live post attributes a claim to MedusaLocker that it exfiltrated data from Spain’s Juntadeandalucia, including 198 emails. The post says the claim is unconfirmed.

The ransomware group “payload” reportedly claimed an attack on Swiss engineering firm Netech (Neeser Technik AG). The monitoring post says industrial machinery and manufacturing support operations were impacted, but the claim is unconfirmed.
A ransomware.live monitoring post says Qilin claimed New World Diagnostics in the Philippines. The post attributes the information to the ransomware group and says it could not confirm the claim.
Safepay claims it targeted Swiss municipal website manno[.]ch and disrupted access to public information. The monitoring post says the claim could not be confirmed.
MedusaLocker claimed it targeted Canadian energy company ATCO Ltd and extracted 80 email addresses. The report says the claim is unverified and identifies mail[.]gmail[.]com as the domain involved.
A ransomware.live monitoring post records a Qilin claim involving Japan’s Nissho Electric Manufacturing, discovered and published on September 28, 2026. The claim’s accuracy is unconfirmed, and no further details were provided.
A ransomware-monitoring post attributes a claimed incident affecting Kellys Home Center to actor pear. It reports disruption to company systems and data but says the group’s claims are unconfirmed.
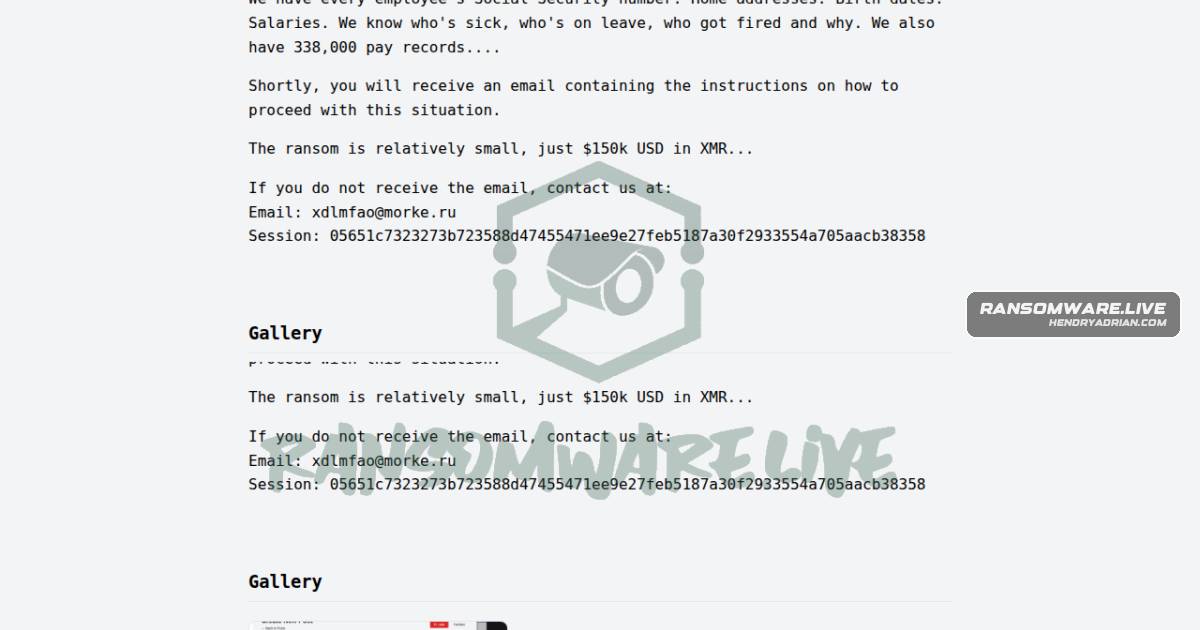
Ransomware group emperador claims it stole employee data from SitePro Rentals, including SSNs and pay records, and demands $150,000 in XMR. The monitoring post says the claims are unconfirmed.
A ransomware.live record says Qilin claimed to target XICO in Mexico, encrypt files, disrupt operations, and demand a ransom. The post says the claims could not be confirmed.
Panzer claims it encrypted or exfiltrated data and disrupted services at Barcelona-based Asesoría FAR. The post cites the group’s leak site; the claims have not been independently confirmed.
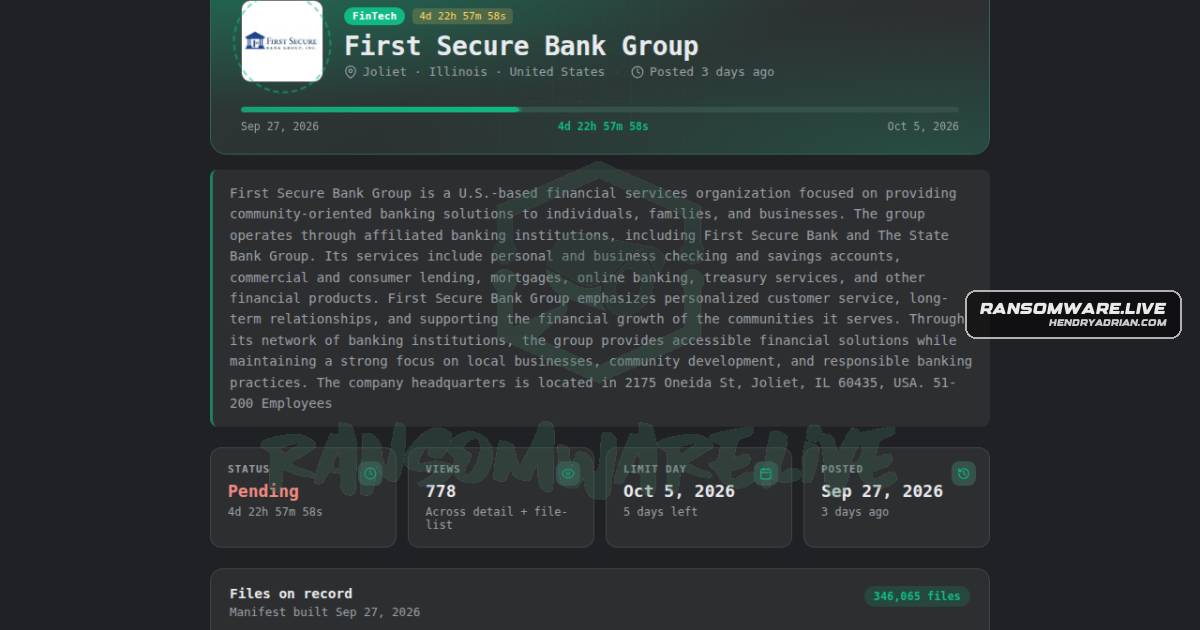
Ransomware group Storm claimed it impacted First Secure Bank Group, a U.S. financial services organization. The claim was listed on 2026-09-27 and has not been independently confirmed.
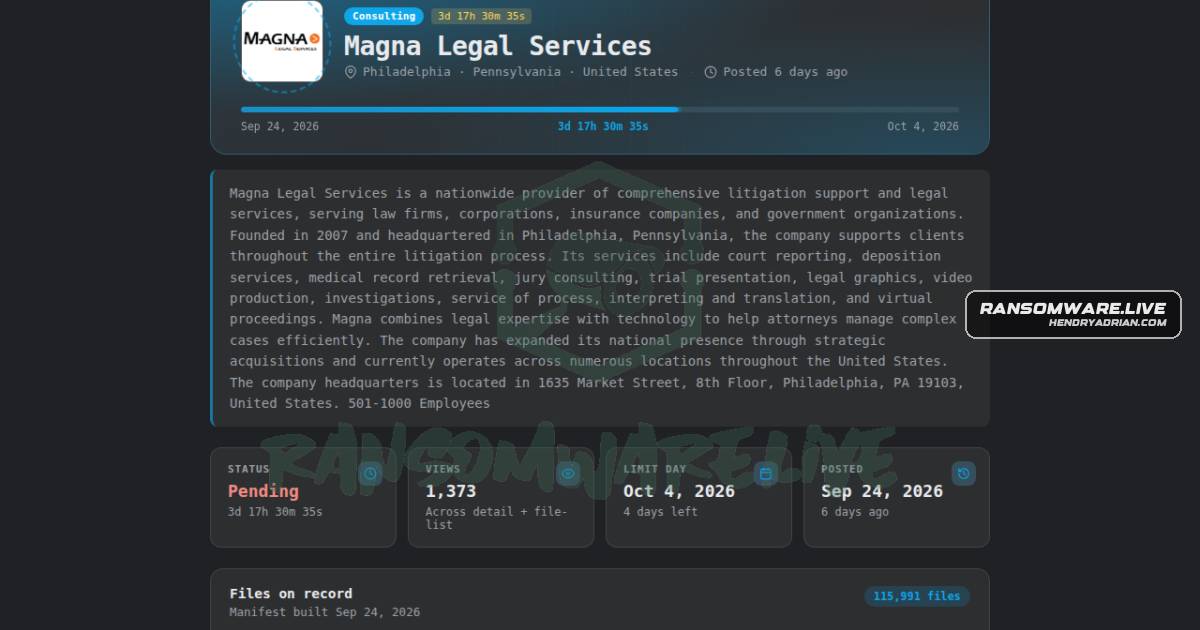
Storm reportedly targeted Magna Legal Services, disrupting litigation-support services. The post attributes the claim to the ransomware group and says it could not confirm the information.

A ransomware claim attributed to thegentlemen names Montreal manufacturer Metalware Corporation. The post says the claim is unverified and provides no details about affected data or operational impact.
The ransomware group “thegentlemen” claims to have targeted South African insurer Guardrisk. The claim is unverified; the post says its accuracy could not be confirmed.
A ransomware.live record attributes a claim against U.S. manufacturer Applied Composites to Storm, with a leak-site source and September 2026 dates. The post says the claim is unconfirmed.
A ransomware.live monitoring post lists South African truck, bus and trailer spare-parts business Apollo 21 as a BlackLocks target. The post says the group made the claim, which the author could not verify.
A ransomware.live post records an unverified m3rx claim involving Cipher Systems (cipher[.]systems), published and discovered on September 26, 2026. The post says it cannot confirm the claim’s accuracy.
BlackLocks claimed an attack on South Africa’s ARCA UNLIMITED Architects, alleging disruption and file and data encryption. The report says the claims are unconfirmed.
Ransomware group Barracuda claims it stole about 90 GB of International Chemical Co. data, including formulas, patents and manufacturing information, and is offering it for sale. The claims are unverified.
A ransomware monitoring post attributes an attack on M****n in the US to payoutsking, alleging disruption and data loss. The post says the claims could not be confirmed.
Ransomware.live lists Crossett Home as a claimed Termite ransomware target. The listing says the petroleum transporter operates in the Eastern U.S. and Ontario, but notes the group's claims are unverified.
Wallstreet allegedly targeted UK industrial-equipment distributor Ar Valve Resources. The post says the claim could disrupt operations but notes it cannot confirm the group's claims.
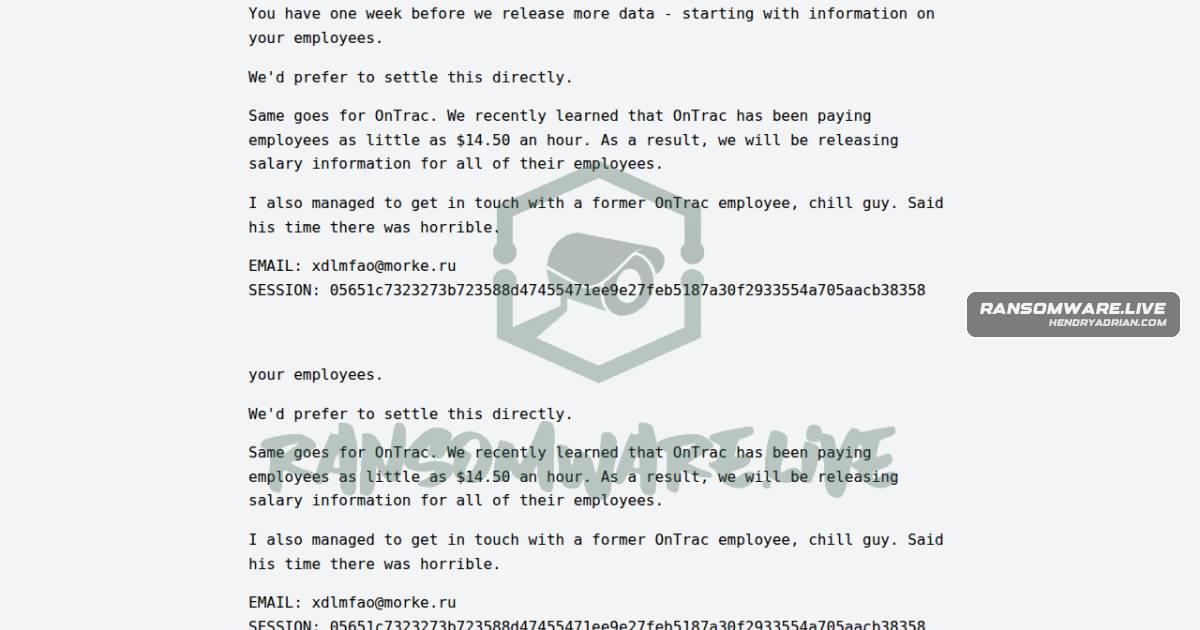
Ransomware group emperador claims it compromised Electrolux and OnTrac and threatens to release employee data within a week. The post says the claims are unverified.