
Ransomware Group Claims Guardrisk as a Victim
Summary
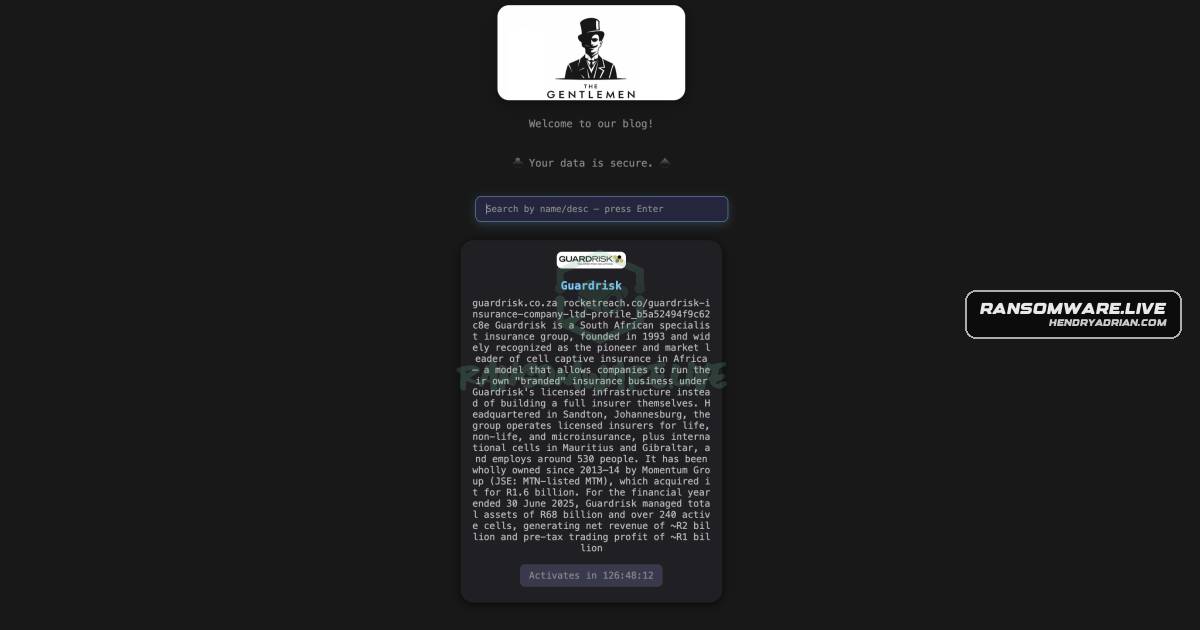
The ransomware group “thegentlemen” claims to have targeted South African insurer Guardrisk. The claim is unverified; the post says its accuracy could not be confirmed.
Key points
- The claim names Guardrisk, a financial services company in South Africa, as the victim.
- The alleged actor is “thegentlemen.”
- The post lists a discovery date of September 26, 2026, and a publication date of September 21, 2026.
- The post attributes the claim to the actor’s onion-site source and says it could not verify the information.
Article Details
- Victim
- Guardrisk
- Victim Domain
- guardrisk.co.za
- Claim Date
- 2026-09-21
- Encryption Status
- Unknown; the source reports an unverified ransomware claim and does not establish encryption.
- Exfiltration Status
- Unknown; the source does not establish whether data was exfiltrated.
- Leak Status
- The source links to a ransomware-group listing for Guardrisk, but does not establish that data was published or verify the claim.