cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1292 articles

Security Insights · aikido.dev

AI Pentesting Aims to Expand Testing Without Increasing Budgets

The article argues AI pentesting can enable more frequent testing without larger budgets. It outlines risk-based, change-aware testing and describes Aikido’s product and pricing model; cost and speed comparisons are vendor claims.

Oct 19, 2026
Security Insights · darkreading.com

Why Vulnerability Counts Should Give Way to Risk-Based Cyber Resilience

The opinion argues that faster vulnerability discovery, including through AI, should not be confused with greater risk. It urges security teams to prioritize remediation by business impact and focus on resilience and outcomes.

Oct 19, 2026
Security Insights · decodedsecurity.com

Five Rules for Preparing for the ISC2 Certified in Cybersecurity Exam

An exam-preparation guide explains five ISC2 CC domains through key concepts and common traps, including risk decisions, recovery objectives, access management, network and cloud security, and incident-response order.

Oct 18, 2026
Security Insights · aikido.dev

Reachable CVEs Aren’t Always Exploitable: How App Context Changes Risk

An explainer distinguishes code reachability from exploitability, showing how attacker-controlled input, configuration, privileges and deployment affect CVE risk. Lodash examples illustrate different outcomes; Aikido also describes its exploitability-analysis product.

Oct 18, 2026
Security Insights · volexity.com

Volexity Demonstrates AI-Assisted Incident Triage and Forensics with Volcano MCP

Volexity demonstrates using Volcano’s MCP integration to analyze a VM infected with a UTA0560 exploit chain, annotate artifacts, create IOCs, and schedule endpoint collections for follow-up.

Oct 16, 2026
Security Insights · malwarebytes.com

High-Volume Job Applications May Make Recruitment Scams Harder to Spot

The article warns that managing many job applications can make unsolicited recruiter messages harder to assess, while noting the reports cited do not establish a causal link. It advises verifying recruiters and protecting accounts.

Oct 16, 2026
Security Insights · thehackernews.com

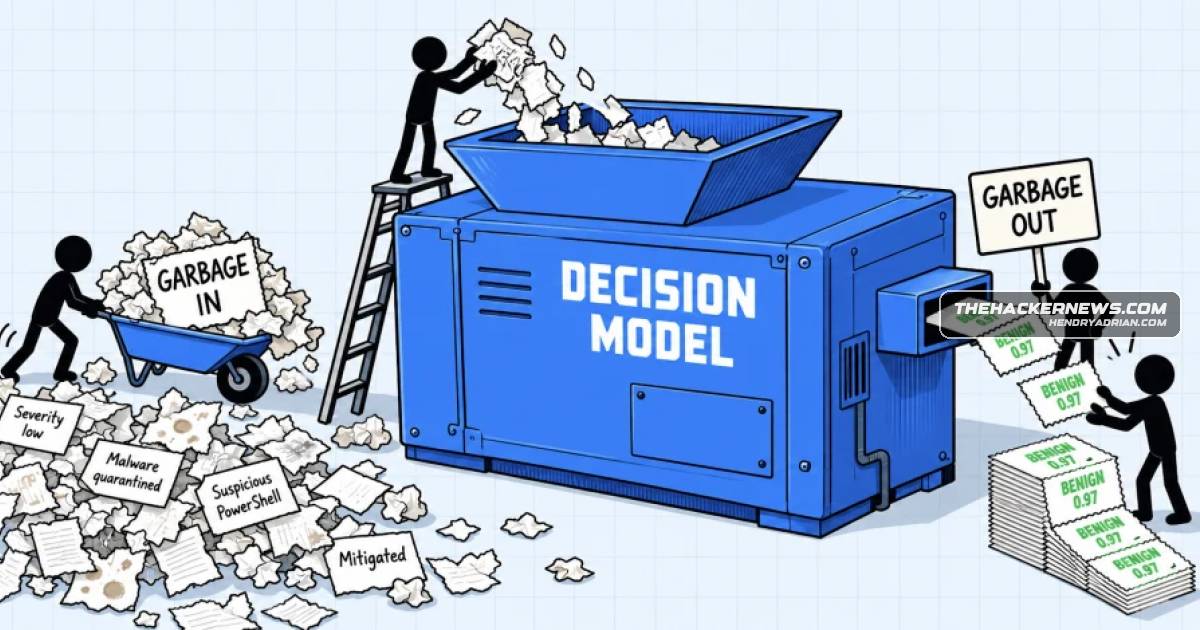
AI Decision Models Can Speed SOC Triage, but Reliable Verdicts Depend on Context

A contributed article argues that AI decision models could make SOC triage faster and more auditable, but reliable verdicts require forensic evidence and up-to-date knowledge of an organization’s normal activity.

Oct 16, 2026
Security Insights · aikido.dev

7 Horizon3 NodeZero Alternatives Compared for 2026

Aikido’s guide compares seven Horizon3 NodeZero alternatives by testing scope, agentic and source-code capabilities, deployment, and remediation. It favors Aikido for application testing but says it does not replace NodeZero’s internal-network, Active Directory, orcloud

Oct 16, 2026
Security Insights · aikido.dev

2026 Guide Compares Nine Alternatives to Escape for Offensive Security

A vendor-authored guide compares nine Escape alternatives across AI pentesting, code access, validated fixes, deployment location and testing scope, and offers criteria for assessing exploit validation, coverage and processing requirements.

Oct 16, 2026
Security Insights · darkreading.com

Ransomware Negotiator’s Arrest Highlights Gaps in Crisis-Vendor Vetting

An opinion article links the arrest of a ransomware negotiator charged in connection with ShinyHunters to weaknesses in crisis-vendor oversight, and recommends pre-vetting vendors, checking principals and conflicts, and ongoing review.

Oct 16, 2026
Security Insights · picussecurity.com

Federal Agency’s Assume-Breach Tests Find Detection Gaps Across Its Sites

A federal agency tested assumed attacker footholds site by site. Reviews found no successful lateral movement, but only about one in ten sites detected simulated activity, and hashes were retrievable on hosts with monitor-only endpoint agents.

Oct 16, 2026
Security Insights · sonatype.com

AI-Generated Dependency Recommendations Can Add Supply Chain Risk

The article argues AI-generated development can amplify unsafe or unnecessary dependency choices, citing Sonatype and external research, and recommends live supply-chain intelligence, automated policy guardrails, and tracking remediation costs.

Oct 15, 2026
Security Insights · cyberbuilders.substack.com

AI Is Speeding Up Cyber Threats and Elevating the Importance of Integrity

A cybersecurity leader argues that AI accelerates attacks and could challenge established assumptions about cryptography, while urging security teams to prioritize the integrity of systems and AI agents.

Oct 15, 2026
Security Insights · thehackernews.com

Why AI Confidence Is Not Validation in Digital Forensics and Incident Response

A SANS contributor argues that DFIR practitioners should independently validate AI findings, document tools and versions, and retain human control over irreversible forensic and incident-response actions.

Oct 15, 2026
Security Insights · securityweek.com

Netskope CISO James Robinson on His Security Career and Building Strong Teams

Netskope CISO James Robinson recounts his path into security and shares advice on curiosity, mentorship, hiring for mindset, and supporting team culture.

Oct 15, 2026
Security Insights · sekoia.com

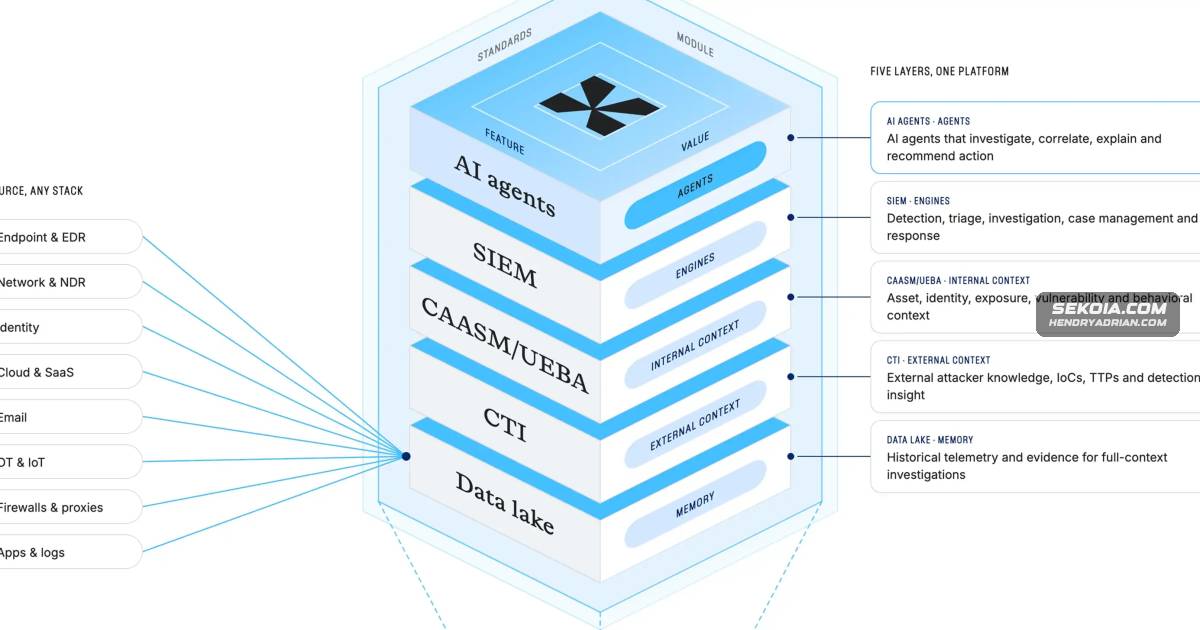
What Integrated Security Operations Mean for the SOC

Sekoia’s article explains how integrated security operations centers (ISOCs) combine SOC capabilities in one operating model, outlining potential efficiency gains, buyer considerations and the risk of vendor lock-in.

Oct 15, 2026
Security Insights · huntress.com

How ITDR Detects and Responds to Identity-Based Attacks

The guide explains how ITDR monitors identity activity for suspicious logins, account takeover, token persistence and privilege abuse, and can revoke sessions or disable accounts. It also cites Huntress-reported identity and ransomware precursor statistics.

Oct 15, 2026
Security Insights · darkreading.com

AI Use Is Making Some Threat Campaigns Sloppier, Researchers Say

Researchers describe AI-generated phishing and malware from several threat groups as error-prone and noisy, exposing infrastructure and weakening campaigns. They say sophisticated espionage groups remain cautious about adopting AI broadly.

Oct 15, 2026
Security Insights · darkreading.com

F-Secure Launches Consumer Scam Guide Covering More Than 50 Fraud Types

F-Secure says its Scam Encyclopedia covers more than 50 consumer fraud types, explains scams from victims’ perspectives, and will be updated as tactics evolve. The company cites a 52% rate of scam victims losing money.

Oct 15, 2026
Security Insights · darkreading.com

Vulnerability Management Should Focus on How Flaws Affect Each Organization

Experts argue that organizations should prioritize vulnerabilities based on their own assets, exposure and attacker activity—not scores alone—as growing volumes of flaws strain manual processes.

Oct 15, 2026
Security Insights · bleepingcomputer.com

Intruder Explains How Its AI Pentester Compares With Human Testers

Intruder argues its AI pentester can find complex flaws and provide code-level fixes, while noting limits such as unpredictable coverage, cautious scope handling, and higher-than-warranted risk ratings.

Oct 15, 2026
Security Insights · cyfirma.com

Deepfake Fraud and Media Provenance: CYFIRMA’s 2026 Forecast Update

CYFIRMA says deepfake fraud, synthetic-media volume, provenance adoption and regulation are tracking its forecasts, while 2026 fraud losses will test its projection of $5–10B or more annually.

Oct 14, 2026
Security Insights · huntress.com

Ransomware: How Attacks Work, Warning Signs, and Prevention

A general guide explains ransomware’s typical entry and encryption process, warning signs, recovery limits, and steps organizations can take to reduce risk, including MFA, tested backups, patching, and employee training.

Oct 14, 2026
Security Insights · huntress.com

Texas HB 3834: Cybersecurity Training Requirements and Compliance Steps

The guide explains who Texas HB 3834 covers, annual cybersecurity training and certification requirements, and how in-scope organizations can meet the added AI awareness training requirement effective September 1, 2025.

Oct 14, 2026
PreviousPage 6 of 54 Next
© 2026 cyber.hendryadrian.com