What Integrated Security Operations Mean for the SOC
Summary
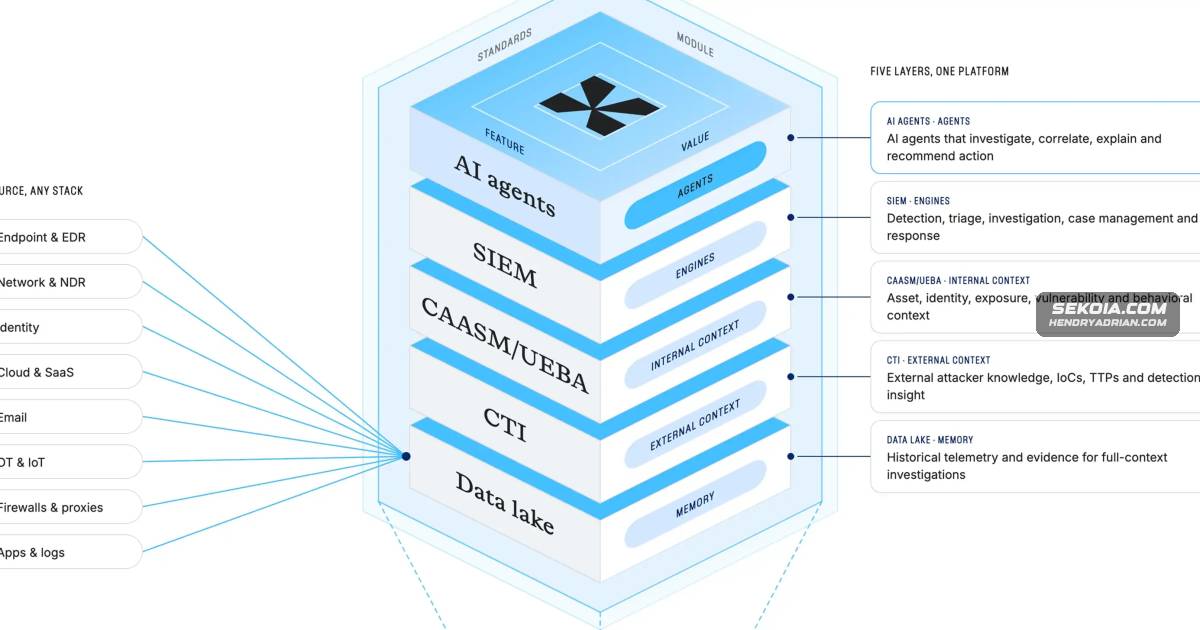
Sekoia’s article explains how integrated security operations centers (ISOCs) combine SOC capabilities in one operating model, outlining potential efficiency gains, buyer considerations and the risk of vendor lock-in.
Key points
- An ISOC aims to deliver connected detection, investigation and response capabilities rather than a standalone SIEM or disconnected set of tools.
- The article says vendor-maintained integrations, detection content and workflows may reduce customer maintenance and investigation friction.
- It presents complexity, hidden integration costs, limited team resources and time to value as drivers of interest in ISOC.
- Automation and AI agents are framed as support for alert enrichment and investigations, not a replacement for human judgment.
- Integrated platforms may reduce complexity but can offer less open extensibility and increase dependence on one vendor.
- The article advises buyers to assess compatibility with existing tools and service providers, deployment flexibility and measurable TDIR outcomes.
Article Details
- Topic
- Integrated Security Operations Center (ISOC) as an integrated security operations model