cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1292 articles

Security Insights · picussecurity.com

Global Retailer Uses Picus for Continuous Attack Simulation and Automated IOC Blocking

A Picus case study says an unnamed global retailer replaced its legacy BAS with Picus, continuously tests controls across stores and servers, and routes unblocked IOCs through a SOAR playbook to its EDR for blocking.
Oct 28, 2026
Security Insights · bleepingcomputer.com

Why Identity Blast Radius Matters More Than CVSS After PHP2Shell

Sponsored analysis argues that patching cannot always outpace exploitation and recommends limiting the access of service accounts and AI agents to reduce the impact of a compromised workload.

Oct 28, 2026
Security Insights · cisecurity.org

Healthcare Regulators Focus on Risk Analysis and Documented System Hardening

The article says healthcare organizations should act on HIPAA risk analyses, apply consistent secure configurations, and document progress. It cites OCR settlements tied to missing risk analyses and recommends CIS Benchmarks and assessment tools.

Oct 27, 2026
Security Insights · aws.amazon.com

AWS Security Professionals Explain the Work Behind Cybersecurity Careers

Three AWS security professionals describe day-to-day application security and penetration-testing work, emphasizing communication, code review, foundational practice, careful AI use, and habits for building a security career.

Oct 27, 2026
Security Insights · malwarebytes.com

How to Browse Safely Amid Fake Verification Attacks and Web Security Flaws

Criminals have used hacked legitimate websites to show fake verification prompts that trick visitors into running malware. The article offers practical steps for safer browsing amid other recent web security problems.

Oct 27, 2026
Security Insights · thehackernews.com

AI Makes Fake Login Pages More Convincing and Account Takeovers Easier

The article explains how AI-assisted fake login pages can steal credentials and MFA codes, while adversary-in-the-middle attacks can capture authenticated sessions. It discusses defensive gaps and promotes Keeper’s phishing protection.

Oct 27, 2026
Security Insights · sekoia.com

Five Principles for Keeping Self-Hosted SOC Platforms Secure and Current

The article outlines five principles for self-hosted SOC platforms: secure deployment, signed and predictable updates, current detection content, clear operational ownership, and transparent releases.

Oct 27, 2026
Security Insights · databreachtoday.com

Why Air Gaps Alone Won’t Secure Critical Infrastructure

An essay compares infrastructure air-gapping with the failed GovNet plan, arguing isolation cannot stop insider or valid-account threats and can impair operations. It recommends machine identities, least privilege, segmentation, selective isolation and monitoring.

Oct 27, 2026
Security Insights · databreachtoday.com

CISO Guidance for Securing AI-Assisted Software Development

JFrog field CISO Paul Davis advises tracking AI agents and software components across development and production, using approved package sources, prioritizing vulnerabilities with application context, and retaining human review for operationally risky changes.

Oct 27, 2026
Security Insights · databreachtoday.com

Why Enterprises Lack Ownership of Cross-Layer AI Security Failures

Enterprise AI can remain fluent while producing unsafe or false outputs, and siloed teams may miss failures spanning data, orchestration, models and hardware. The article outlines four compromise paths and recommends cross-layer ownership and stronger integrity checks.

Oct 27, 2026
Security Insights · darkreading.com

AI Could Erode Cybersecurity Skills Without Hands-On Experience

Kudelski Security’s Nathan Hamiel warns that overreliance on AI could weaken cybersecurity expertise and limit junior professionals’ learning. He recommends using AI where it helps while retaining the skills needed to assess its results.

Oct 27, 2026
Security Insights · cyberscoop.com

Warlock Intrusion Shows Why Security Must Survive Disabled Sensors

Researchers described a Warlock intrusion in which attackers disabled security tools across dozens of hosts before deploying ransomware. The article argues for protections that act on-device and remain effective when monitoring fails.

Oct 27, 2026
Security Insights · bleepingcomputer.com

Huntress Ranks Tactics Putting Businesses at Risk

Huntress’s Tragic Quadrant ranks tactics targeting businesses, including RMM abuse, mailbox manipulation and AiTM. Huntress reports RMM abuse in 45% of its Q1 2026 endpoint investigations and explains device-code phishing, ClickFix and AI-platform lures.

Oct 27, 2026
Security Insights · arcticwolf.com

PHP2Shell Is a Wake-Up Call for Business Cyber Resilience

Arctic Wolf says its telemetry showed scanning spikes and exploitation attempts around PHP2Shell, using the case to urge asset visibility, exposure management, timely patching and tested response plans as AI compresses attack timelines.

Oct 26, 2026
Security Insights · cyble.com

How Brand Intelligence Could Help Disrupt the Booking.com ClickFix Campaign

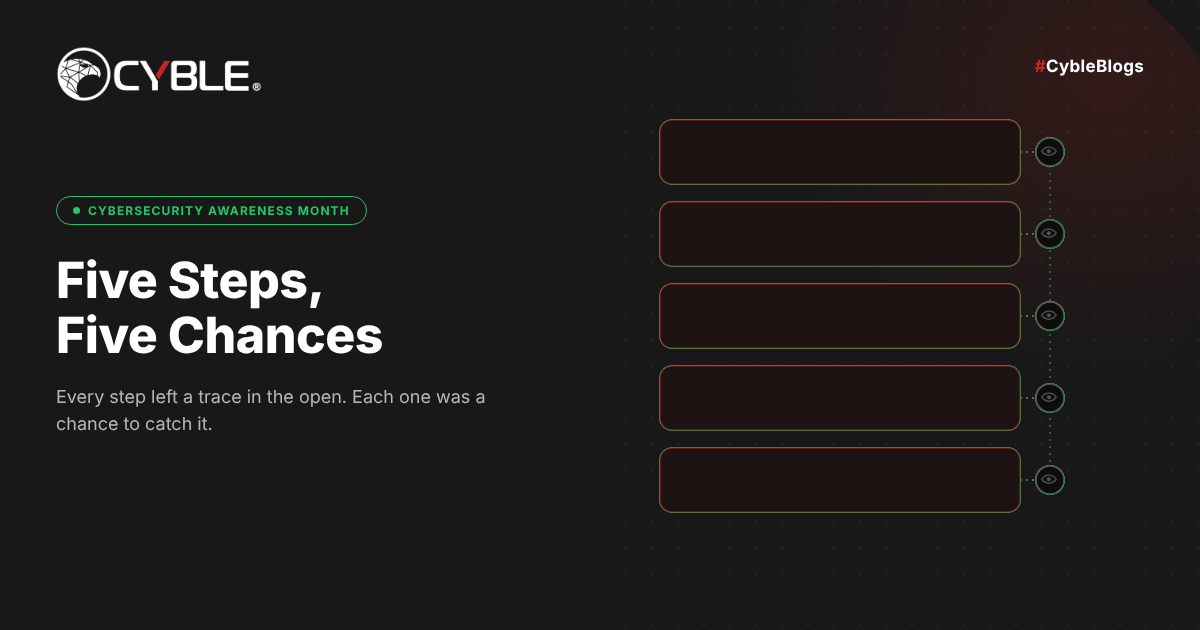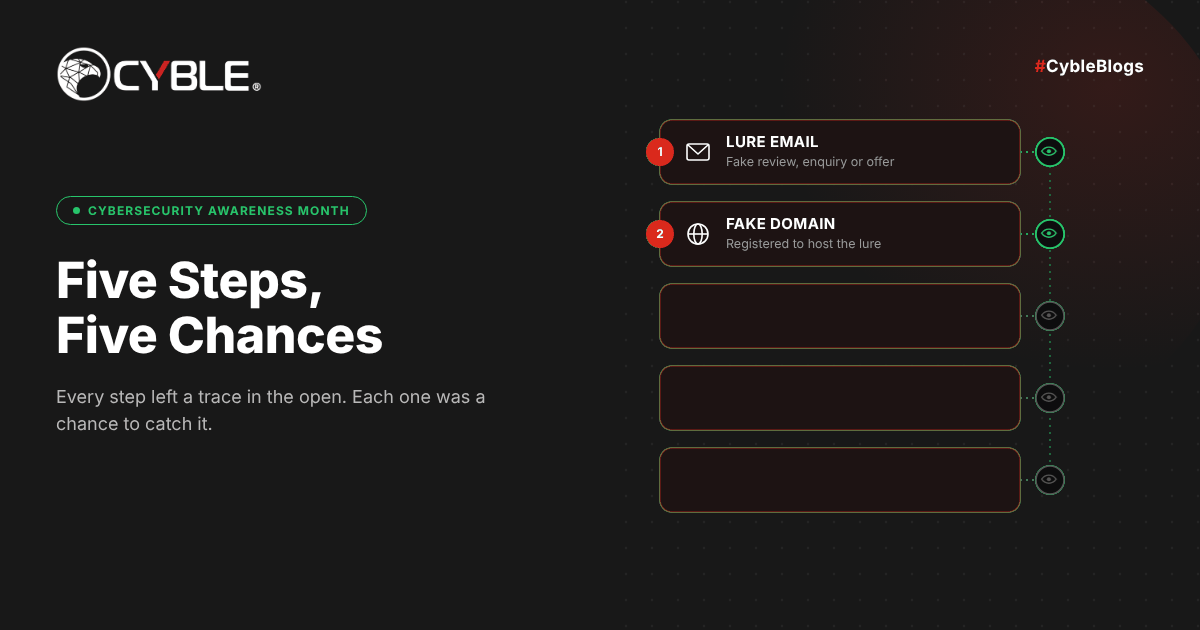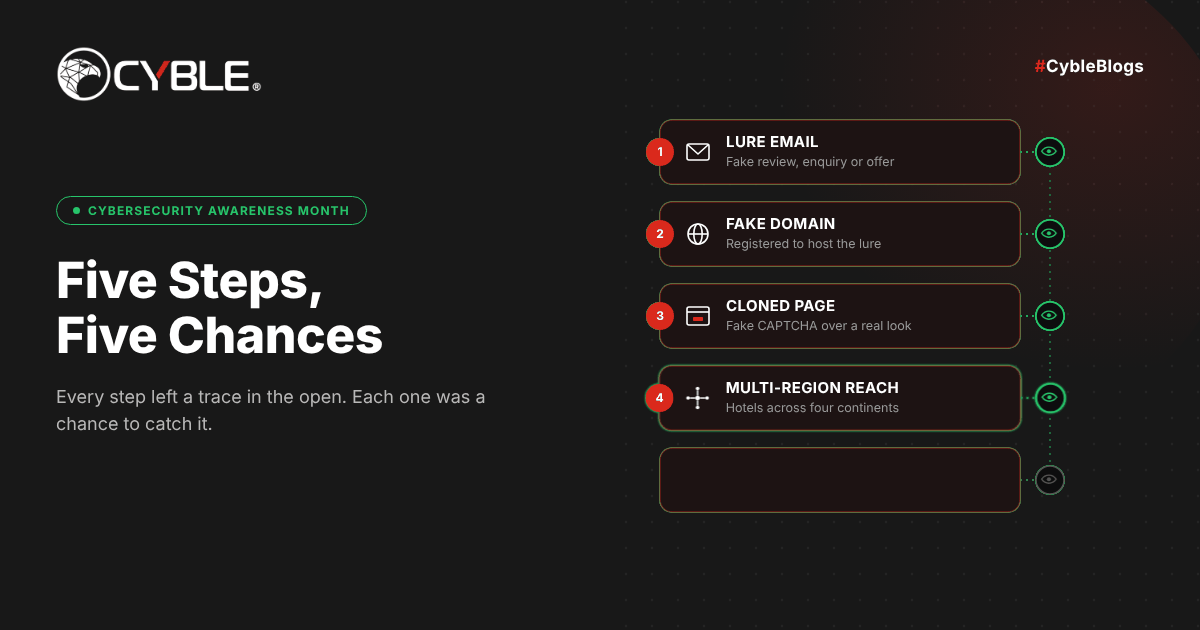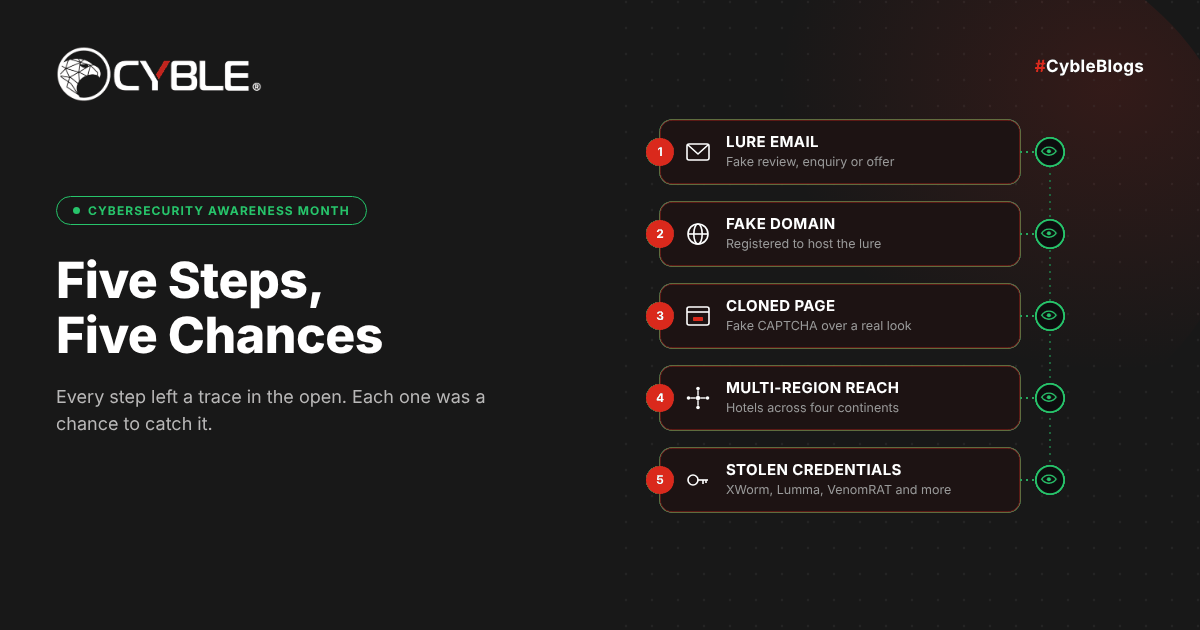
Microsoft reported Storm-1865 used fake Booking.com pages and ClickFix lures to deliver credential-stealing malware to hospitality staff. Cyble's sponsored walkthrough maps its brand-intelligence tools to the campaign and clarifies it did not participate in the response

Oct 26, 2026
Security Insights · securitylabs.datadoghq.com

Code Security Basics for Developers Using AI Coding Agents

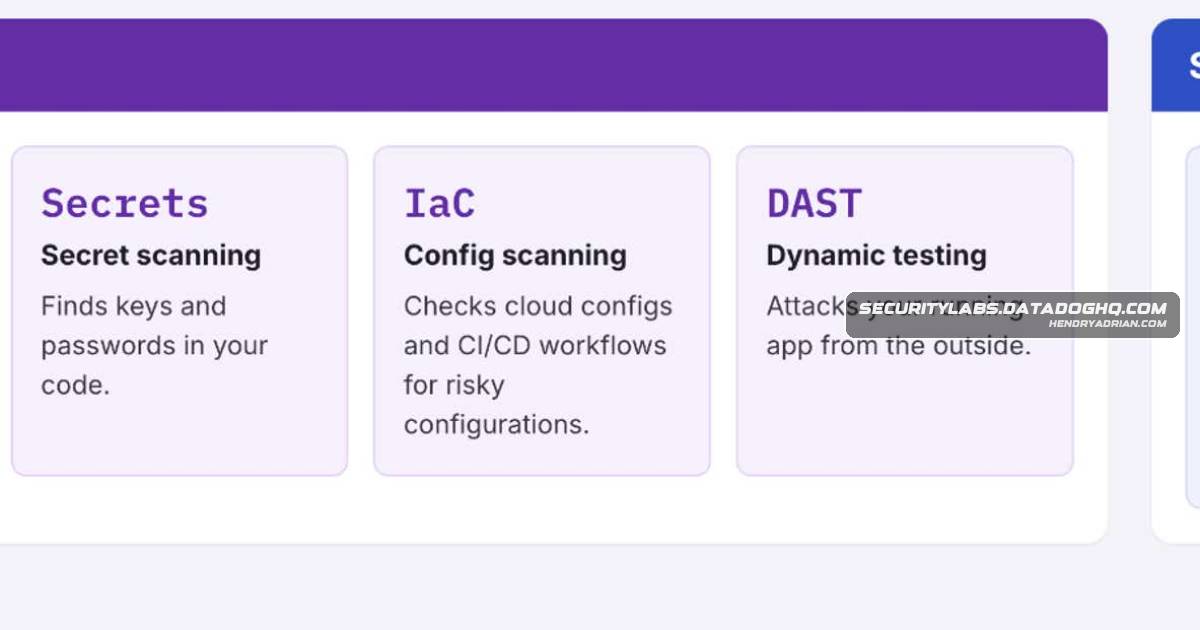
A beginner’s guide to securing code built with AI agents, covering secrets, first- and third-party code, dependency risks, security questions to ask agents, and common scanning tools.

Oct 26, 2026
Security Insights · bleepingcomputer.com

AI Agent Incident Readiness Starts With Identity and Credential Records

A sponsored analysis of a federal AI-agent incident guide argues that readiness depends on agent-specific identities, credential inventories and tamper-resistant session logs. It cites the OpenCode exposure and a Hugging Face evaluation incident as examples.

Oct 26, 2026
Security Insights · darkreading.com

10 Software Security Practices for Long-Term Resilience

An opinion article recommends 10 lasting software-security practices, including secure-by-design architecture, dependency provenance, continuous code verification, remediation of security debt, and threat modeling AI systems.

Oct 26, 2026
Security Insights · aikido.dev

How to Add AI Pentesting to an Existing Security Stack

Aikido’s guide covers scoping and integrating AI pentests with existing security tools, including staging environments, role-based credentials, optional source-code access, and retesting. Aikido reports white-box tests found 7x more vulnerabilities than grey-box tests.

Oct 24, 2026
Security Insights · decodedsecurity.com

How Password Hashing and Salting Protect Stored Passwords

A beginner’s guide explains how unique salts and slow password-hashing functions protect stored passwords, why fast general-purpose hashes are unsuitable, and how unique passwords and MFA help limit risk.

Oct 23, 2026
Security Insights · picussecurity.com

PHP2Shell Highlights Limits of Automated Pentesting and Value of Attack Simulation

Picus says PHP2Shell’s lack of a safe day-one exploit left automated pentesting limited to version fingerprinting, while its breach-and-attack simulation tested deployed controls and guided signature fixes; it urges patching PHP and revalidating defenses.

Oct 23, 2026
Security Insights · darkreading.com

Why Caribbean Cyber Risks Can Cascade Across Global Supply Chains

Commentary argues that rapid exploitation and annual supplier reviews leave Caribbean organizations exposed, with risks cascading through shared platforms. It recommends continuous assurance, faster remediation measurement, segmentation, and monitoring federated access.

Oct 23, 2026
Security Insights · wiz.io

Wiz Explains Prioritizing Exploitable Application Risks with Code-to-Cloud Context

Wiz describes enriching and deduplicating application-security findings, then correlating code, build, cloud runtime, and network exposure to prioritize exploitable attack paths and manage lower-priority security debt.

Oct 22, 2026
Security Insights · unit42.paloaltonetworks.com

How Attackers Exploit OAuth Tokens to Bypass MFA and Maintain Access

Unit 42 explains how OAuth phishing steals tokens after MFA, enabling persistent access, consent abuse and malicious redirects, and recommends admin-controlled consent, clipboard monitoring and redirect-URI audits.

Oct 22, 2026
PreviousPage 4 of 54 Next
© 2026 cyber.hendryadrian.com