cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1292 articles

Security Insights · darkreading.com

Why Incident Response Communication Needs Automation—with Human Oversight

Manual incident communications can lag automated detection and strain trust. The article recommends automating coordination and update drafts while keeping human review, and describes proposed CIRCIA reporting deadlines.
Nov 4, 2026
Security Insights · cisecurity.org

Why Secure Configuration Can Outlast the Zero-Day Race

The article argues that complete secure-configuration baselines can reduce attack surface before vulnerabilities are disclosed, citing SMBv1, App Installer and MFA examples while noting that hardening complements—not replaces—patching and other defenses.

Nov 3, 2026
Security Insights · socprime.com

How to Export Falcon LogScale Logs

A guide to exporting Falcon LogScale events through its query API or search UI, converting NDJSON @rawstring data to raw logs, and troubleshooting permissions, timestamps, aggregation, missing fields and timeouts.

Nov 3, 2026
Security Insights · socprime.com

How LogTotal Sanitizes Logs Before Analysis

LogTotal masks identifying values in plain-text, CSV and JSON uploads while preserving patterns needed for detection. EVTX files are not sanitized, so users should review data before uploading and follow their organization’s handling rules.

Nov 3, 2026
Security Insights · thehackernews.com

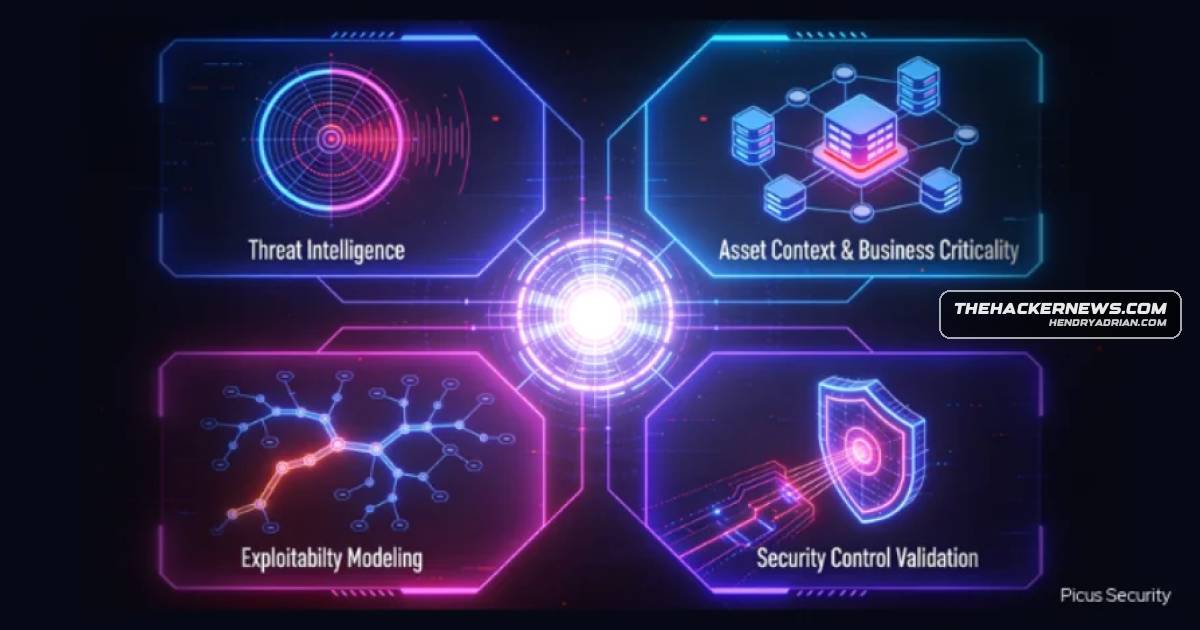
Four Elements of Exposure Prioritization and How to Operationalize Them

The article explains a four-part approach to exposure prioritization—threat intelligence, asset context, exploitability modeling and security control validation—and describes how Picus says its platform combines them.

Nov 3, 2026
Security Insights · toxsec.com

How AI Agent Teams Could Scale a One-Person Cyber Operation

The article argues that AI-agent hierarchies could let one skilled operator scale offensive work, citing Anthropic’s report of at least 14 internal-access cases among 42 tracked entities and research on agent-assisted testing; it stresses authorization and oversight.

Nov 3, 2026
Security Insights · databreachtoday.com

Building Trust in AI-Powered Cybersecurity Through Evidence and Controls

The article argues that organizations should govern agentic AI by controlling its access and actions, monitoring behavior, and expanding autonomy gradually as evidence of reliability builds.

Nov 3, 2026
Security Insights · huntress.com

Wuffy Scam and Ransomware Payments Reveal Hidden Money Trails

The article connects a network of 250+ fake AI-toy stores, estimated to process $50 million annually, with a reported $40 million CNA Financial ransom traced by UK investigators through illicit financial networks. It offers practical scam-prevention advice.

Nov 3, 2026
Security Insights · cyberscoop.com

CISA’s 2030 Strategy Faces a Legacy Trust Challenge

The article argues that CISA’s 2030 goals require operators to reassess trust in OT devices, software, identities, and AI agents, enforce access limits, and test whether access can be revoked without interrupting essential services.

Nov 3, 2026
Security Insights · gendigital.com

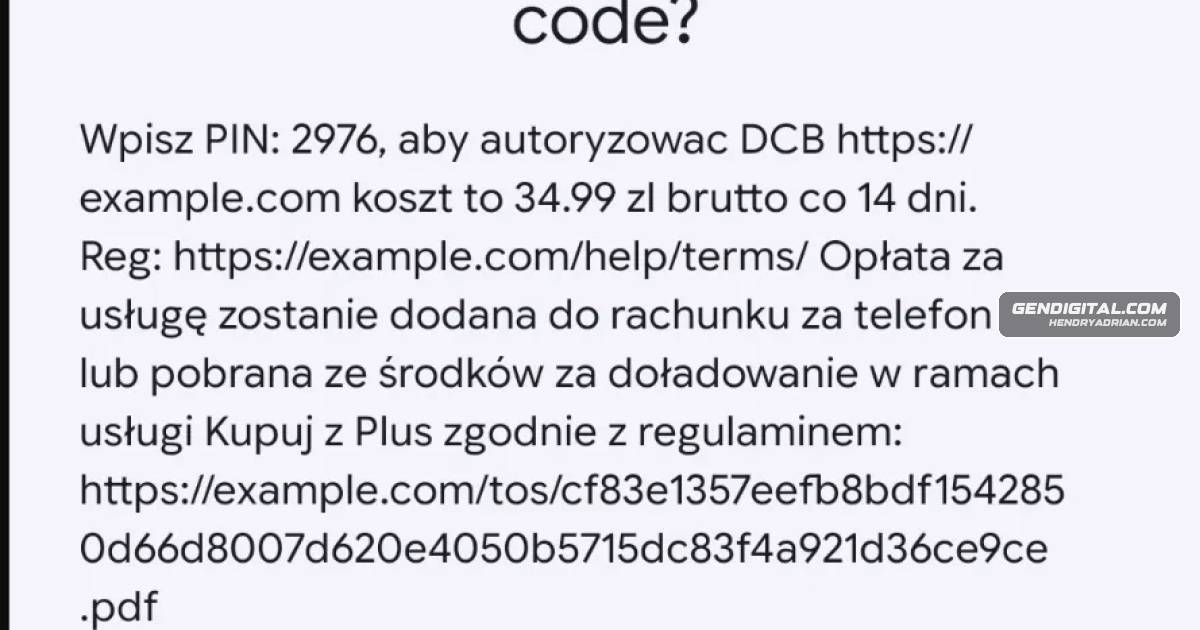
BillBait Uses SMS Autofill to Obscure Recurring Subscription Charges

Gen Threat Labs describes “BillBait,” misleading mobile subscriptions that use SMS-code autofill to make recurring-payment authorization resemble routine phone verification, and recommends reading the full SMS before submitting a code.

Nov 2, 2026
Security Insights · censys.com

Censys: PHP2Shell Highlights the Challenge of Maintaining Vulnerable Software

Censys reports that more than 11 million PHP services moved to fixed versions after PHP2Shell patches became available, while over 30 million still reported affected versions as of October 29. Its research also found that the oldest enterprise software changes little.

Nov 2, 2026
Security Insights · socprime.com

Which Log Formats LogTotal Can Analyze

SOC Prime’s LogTotal analyzes EVTX, JSON/JSONL, syslog-style text and CSV logs. The guide explains which formats are sanitized, how to convert files, and how to handle encoding, timestamps and file size.

Nov 2, 2026
Security Insights · iru.com

CVE Disclosures More Than Doubled in 2026, but Confirmed Exploitation Rose 31%

The article finds 2026 CVE disclosures rose about 2.3x year over year through late October, while CISA KEV additions rose about 31%. It argues defenders should prioritize exposed edge devices, rapid patching and behavioral detection.

Nov 2, 2026
Security Insights · elastic.co

How Elastic’s Agent Skills Build and Test an NVD Integration

Elastic’s Integration Skills automate research, scaffolding, CEL development, pipelines, tests, and review. A NIST NVD example built snapshot and change-event streams, while the article stresses human review of assumptions and test coverage.

Nov 2, 2026
Security Insights · databreachtoday.com

How Organizations Can Prepare for Post-Quantum Cryptography

Intel’s Steve Orrin advises organizations to inventory cryptography across IT, operational technology and vendors, then prioritize high-value systems, long-lived data and trust relationships in a phased post-quantum migration plan.

Nov 2, 2026
Security Insights · crowdstrike.com

CrowdStrike Hackathon Highlights Five Principles for Security AI Agents

CrowdStrike and NVIDIA's AgentWorks Hackathon showcased agents for MCP-server discovery, MFA-reset abuse, and detection-rule testing. The article distills lessons on deterministic tools, guardrails, measurable outcomes, and trace-based optimization.

Nov 2, 2026
Security Insights · darkreading.com

Opinion: Microsoft’s AI Risk Report Overlooks Legacy Software Exposure

The opinion argues that Microsoft’s 2026 Digital Defense Report overlooks legacy software and vendor-concentration risks, citing CISA vulnerability figures, VA software decisions, and prior government compromises to call for stronger product security.

Nov 2, 2026
Security Insights · isc.sans.edu

Extract Embedded Files from Multiple OneNote Files with onedump.py

A new onedump.py option outputs embedded files from multiple OneNote files as JSON. Piping the output to myjson-filter.py writes the files to disk using each file's SHA-256 hash as its name.

Nov 1, 2026
Security Insights · bleepingcomputer.com

How Beginners Can Build Bug Bounty Skills in the AI Era

This sponsored guide offers practical advice for learning bug bounty skills: practise in authorized labs, verify findings with evidence, use AI for hints, and write reproducible reports. It also discusses changing submission quality at curl and Google programs.

Oct 31, 2026
Security Insights · securityweek.com

Passkeys Strengthen Authentication but Don’t Solve Identity Security

Passkeys reduce phishing and reusable-credential risks, but organizations still need to secure identity enrollment and recovery and monitor for device, session, and account risks after authentication.

Oct 30, 2026
Security Insights · socprime.com

How to Export CrowdStrike Falcon Event Data for Investigation

Guide to exporting Falcon sensor telemetry with Advanced Event Search or Falcon Data Replicator, filtering bulk JSON by agent ID and event type, and uploading it to LogTotal[.]com. It distinguishes sensor telemetry from raw host logs and notes access and retentionlimits

Oct 30, 2026
Security Insights · socprime.com

How to Export Microsoft Defender XDR Hunting Results as JSON

A tutorial shows how to export Defender XDR Advanced Hunting results as JSONL through Microsoft Graph, with required permissions, query limits, retention caveats, and troubleshooting tips.

Oct 30, 2026
Security Insights · jamf.com

Binance Theft Highlights DPRK Targeting of Developer Laptops

Chainalysis and TRM Labs attributed a roughly $6.4 billion Binance theft to a likely DPRK-linked attack. Binance said a developer laptop may have been involved, but the full intrusion path remains undisclosed. The article outlines targeting tactics and defenses.

Oct 30, 2026
Security Insights · aikido.dev

Why Read-Only Kubernetes AI Agents Can Still Expose Secrets

A Kubernetes security discussion explains how poisoned log content can influence AI agents and how broad read permissions may expose secrets even in read-only mode. It recommends limiting agent access and verifying agent actions.

Oct 30, 2026
PreviousPage 2 of 54 Next
© 2026 cyber.hendryadrian.com