
Four Elements of Exposure Prioritization and How to Operationalize Them
Summary
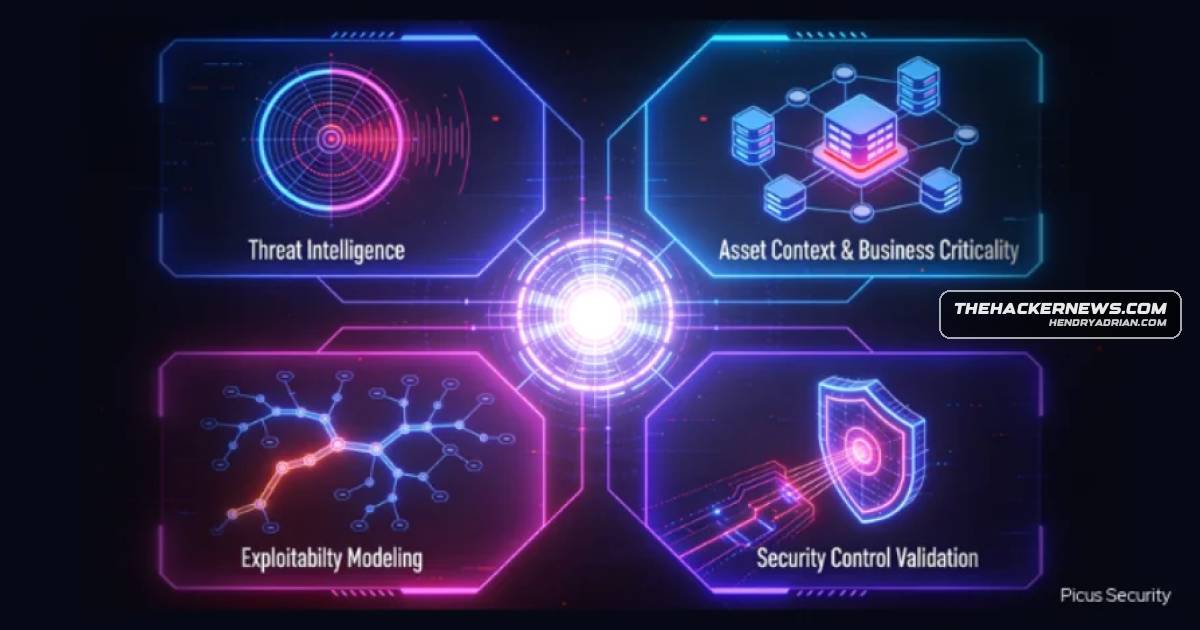
The article explains a four-part approach to exposure prioritization—threat intelligence, asset context, exploitability modeling and security control validation—and describes how Picus says its platform combines them.
Key points
- The framework calls for combining threat intelligence, business-critical asset context, exploitability modeling and security control validation rather than relying on CVSS scores alone.
- The article says teams should track the time from threat publication through testing and remediation.
- It recommends unifying and updating asset context from sources such as scanners, CMDBs, cloud security platforms and identity systems.
- EPSS can help estimate general exploitation likelihood, but the article says those estimates should guide local validation rather than serve as a final verdict.
- Security control validation assesses exposures against defenses such as segmentation, endpoint protection, detection coverage and identity controls.
- The article describes safe live attack execution and attack-chain analysis as validation approaches.
- Picus says its platform combines the four elements; it also reports that one customer reduced its critical ticket backlog by 98% and had a validation cycle of under six hours.
Article Details
- Topic
- Exposure prioritization using threat intelligence, asset context, exploitability modeling, and security control validation
Vendors
Products
Picus Breach and Attack Simulationbecause evidence is what turns the other three elements from assumptions into decisions. Picus Breach and Attack Simulation is one of three validation methods on the platform.Picus Platformon CVSS-based vulnerability prioritization. Let’s break down how each element works, and how the Picus Platform puts all four into practice.