
How to Export Logs from OpenSearch
A practical guide to exporting OpenSearch logs with Python or curl, including permissions, field selection, pagination limits, and troubleshooting for security-log review.
Actionable detection engineering, threat hunting, hardening, and defensive response guidance.
624 articles
A practical guide to exporting OpenSearch logs with Python or curl, including permissions, field selection, pagination limits, and troubleshooting for security-log review.
A practical guide to exporting scoped Splunk logs through Web, CLI, or REST for security analysis, with advice on export limits, timestamps, permissions, and handling sensitive data.
A practical guide to exporting readable QRadar event payloads with AQL and the Ariel REST API, including token scope, retention, certificate, and troubleshooting considerations, then reviewing the data in LogTotal.
Shadow AI creates three distinct risks: sensitive data sent to external services, unverified AI-generated code and dependencies, and models entering software builds. The article outlines governance, review, scanning and proxy controls for each.
The article explains what MSSP services may cover—and miss—and gives buyers practical questions for assessing business-specific monitoring and threat hunting. It emphasizes that AI can speed alert triage but does not replace business context or fresh threat intelligence
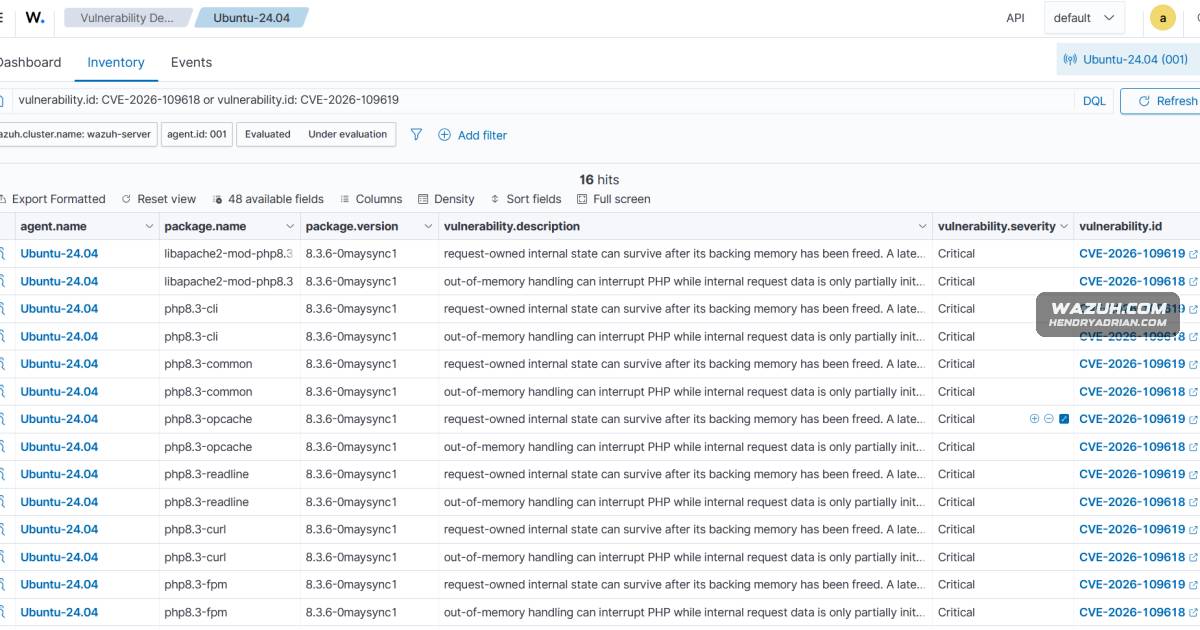
A Wazuh walkthrough shows how to identify vulnerable PHP packages, check partial mitigations, and alert on PHP2Shell indicators. It recommends fixed PHP releases as the only complete fix for CVE-2026-109618 and CVE-2026-109619.
Unit 42 outlines ransomware, data theft, DDoS, skimming, account takeover and gift-card fraud risks to retailers during 2026’s peak season, with examples and defensive measures including segmentation, DLP, bot mitigation and automated response.
Microsoft advises CISOs to govern enterprise AI agents with dedicated identities, least-privilege access, data protections and deep observability, while integrating security signals and using agents to accelerate investigation and response.
Banks are detecting third-party AI agents in customer accounts, raising risks around credential exposure and misuse. The article advises consumers to avoid sharing logins, use approved read-only access where possible, limit data shared, and review consequential actions.
ANY.RUN describes Skyw4lker, a device-code phishing campaign targeting U.S. organizations with business-themed documents and Microsoft authentication flows, and outlines sandbox and threat-intelligence workflows for detection.
Qualys outlines interim mitigations for Node.js flaws, including CVE-2026-111497, and recommends prioritizing exposed runtimes, adding WAF/IPS/EDR controls, then upgrading and verifying. Its telemetry found 42,000 of 3.3 million installations patched.
Canada’s Cyber Centre warns that vishers impersonate IT staff and relay credentials and MFA responses through lookalike sign-in pages. The actor has reportedly used authenticated sessions to access Microsoft 365 and SaaS data; the alert recommends phishing-resistant MFA
eSentire says its threat-response team traced Citrix NetScaler exploitation to September 8, before disclosure, and found activity across customer environments. The company describes its hunting, response, and detection work and recommends assessing appliance integrity.
The article describes five election-themed scams targeting voter information, donations, survey payments, alleged fines or election duties, and merchandise purchases. It advises verifying requests through official channels and avoiding unsolicited payment demands.
A practical guide to forwarding Palo Alto and FortiGate logs to a Linux rsyslog collector or downloading existing logs, with configuration steps, review patterns, and troubleshooting advice.
A practical guide to exporting Google Workspace audit logs through the Admin console or Reports API, including a Python example, access requirements, retention limits, troubleshooting, and events to review for suspicious activity.
A guide to locating and exporting Windows DNS logs, enabling query logging for future investigations, and spotting potential tunneling, generated domains, record changes, and DnsAdmins abuse. It warns that LogTotal uploads are not yet sanitized.
Erich Winkler argues that AI agent risks often stem from longstanding security gaps. He outlines seven defenses, including least privilege, trust boundaries, data classification, secret management, supply-chain checks, and out-of-band verification.
Based on 100+ audits, the article explains why messages reach spam and recommends monitoring domain/IP reputation, suppressing disengaged recipients, validating SPF/DKIM/DMARC, enforcing DMARC, and restricting SaaS notification features that can be abused for phishing.
The guide explains how SURBL lists URLs in email, common causes including compromised sites, leaked ESP keys and unsolicited outreach, and a four-step process to investigate, fix root causes, strengthen email security and request delisting.
At an ISC2 session, an Atlassian security manager described how an outdated SBOM and hidden transitive dependency hindered response to a Shai-Hulud compromise, and urged teams to prioritize runtime visibility and incident-scoping capabilities.
Cyber legal expert Daniel B. Garrie outlined frameworks for scoring AI deployment risk, documenting board decisions, and preserving evidence during incidents, alongside contract provisions and exercises for CISOs.
A Picus case study describes a U.S. school district using breach-and-attack simulations to identify EDR and firewall gaps, apply vendor-specific mitigations, and retest controls across endpoints and servers.
The article outlines a method for comparing Salesforce authorization across UI API, GraphQL, and custom Apex. It highlights that Apex database access defaults differ by class API version and recommends testing restricted and guest users.