
Acronis Study Finds Outdated Software and Delayed Patching Across Business PCs
Summary
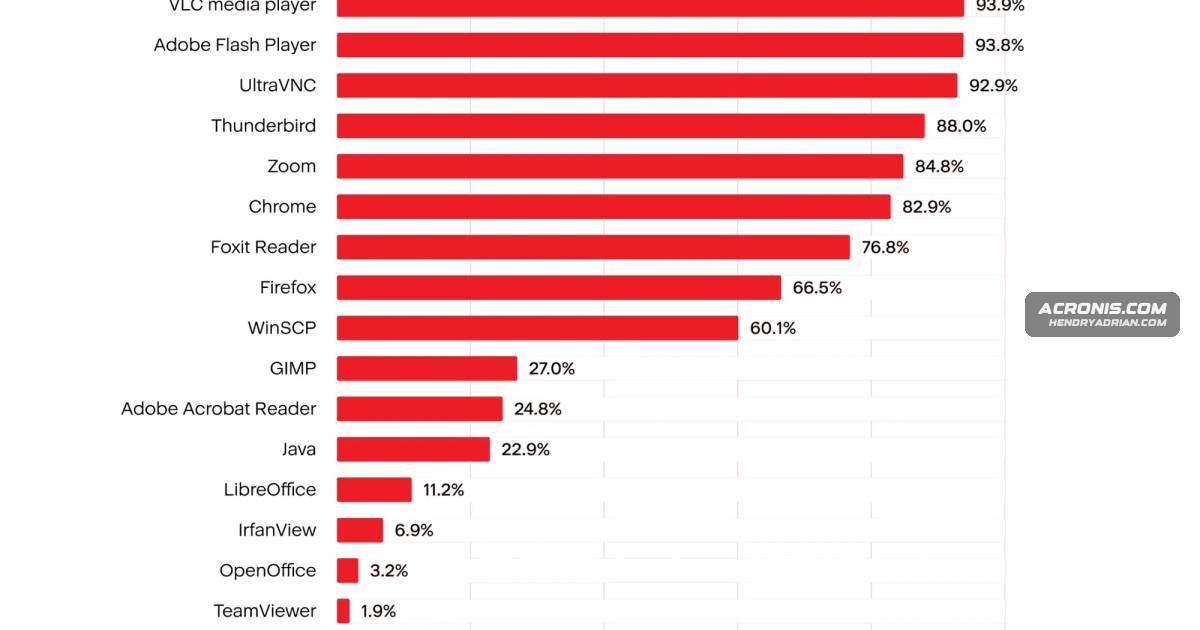
Analysis of anonymized telemetry from over 1.8 million business computers found widespread outdated and unsupported apps. Of Windows PCs with update data, 22.1% had third-party security updates overdue by 30+ days; most addressed known-exploited flaws.
Key points
- Acronis analyzed anonymized telemetry from more than 1.8 million business computers online on September 30, 2026.
- Among Windows PCs with update data, 22.1% had at least one third-party app security update waiting for more than 30 days; 77% of those PCs had an update addressing a known-exploited weakness.
- Nearly 1 in 4 Windows PCs ran at least one product past its end of support. The study found such products on 49.6% of Windows 10 PCs versus 17% of Windows 11 PCs.
- Update delays varied widely: the median was six days overall, 35 days for WinRAR, and 1,000 days for Java updates installed during the quarter.
- Only 41.5% of the selected Windows PCs had update data, limiting visibility; Acronis said PCs without update data had end-of-support products at a similar rate to those with data.
- The report recommends inventorying software across all PCs, enabling third-party app patching, investigating updates that remain pending, removing unsupported products, and replacing PCs that cannot run supported Windows versions.
- The smallest customer groups had less update visibility and more end-of-support software than larger groups.
Article Details
- Publisher
- Acronis
- Report Period
- Telemetry snapshot: September 30, 2026; software removals and installed updates: Q3 2026; published November 11, 2026.
- Scope
- Anonymized telemetry on software inventory, age, support status, removals, and delayed security updates across Windows PCs and Macs. The report describes computer exposure, not confirmed breaches.
- Sample Size
- More than 1.8 million business computers protected by Acronis and online September 30, 2026. Update data was available for 41.5% of selected Windows PCs; 34% of online Macs completed an app scan.
- Key Statistics
- Acronis analyzed anonymized telemetry from more than 1.8 million business computers online September 30, 2026.
- Among Windows PCs with update data, 22.1% had at least one third-party app security update waiting for more than 30 days; update data was available for 41.5% of the selected Windows PCs.
- On 77% of PCs with a waiting update, the update fixed a weakness on the CISA list of vulnerabilities already used by criminals.
- 22.8% of Windows PCs had at least one product past its end of support.
- For Java security updates installed in Q3 2026, the median time from release to installation was 1,000 days.
- Recommendations
- Inventory the apps on every PC and remove products whose makers no longer provide security support.
- Extend scanning to every managed PC and enable patching for third-party apps; treat missing update data as a visibility gap.
- Review approvals, maintenance schedules, and restart requirements to find why updates remain uninstalled, and prioritize fixes for weaknesses on the exploited list.
- Replace or upgrade PCs that cannot run a supported version of Windows, prioritizing older systems and the smallest customers.
- Decide whether to license, replace, or remove Java, and remove remote-control tools when they are no longer needed.
CVE
Vendors
AcronisAcronis Threat Research UnitAdobeAdobe Acrobat and Reader 9, X and XIAppleApple QuickTime for WindowsGoogleGoogle Chrome 109 or older (last version for Windows 7, 8 and 8.1)MicrosoftMicrosoft Visual C++ RedistributableMozillaMozilla Maintenance ServiceOracle4.9% of the PCs with update data have a waiting Java update. For Java 8, which many businesses still run, Oracle ties updates for business use to a paid subscription. A paid line item is easy to skip, and the update
Products
7-Zipthat criminals are already using. The apps most often affected are WinRAR, Java, Firefox, Notepad++ and 7-Zip.Adobe Acrobat and ReaderAdobe Acrobat and Reader 9, X and XIJavawaiting update fixes a weakness that criminals are already using. The apps most often affected are WinRAR, Java, Firefox, Notepad++ and 7-Zip.Mozilla Firefoxupdate fixes a weakness that criminals are already using. The apps most often affected are WinRAR, Java, Firefox, Notepad++ and 7-Zip.Notepad++a weakness that criminals are already using. The apps most often affected are WinRAR, Java, Firefox, Notepad++ and 7-Zip.WinRARthe waiting update fixes a weakness that criminals are already using. The apps most often affected are WinRAR, Java, Firefox, Notepad++ and 7-Zip.