
StepSecurity Says Harden-Runner Now Protects 10,000 Open-Source Repositories
Summary
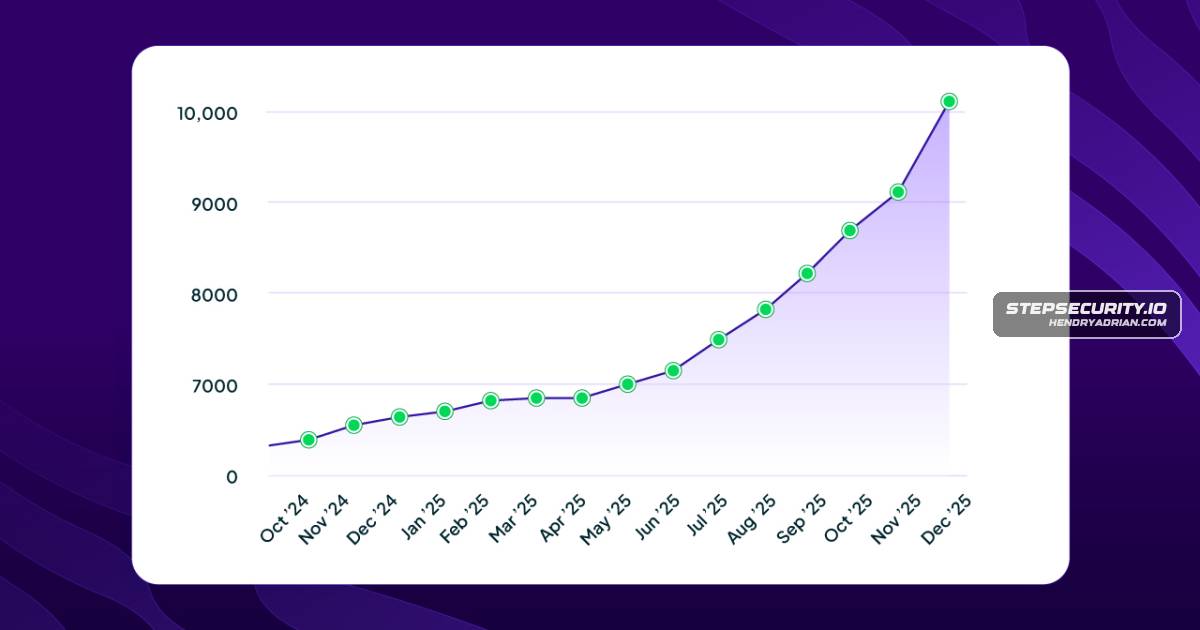
StepSecurity says Harden-Runner now protects 10,000+ open-source repositories and monitors 13 million jobs weekly. The company describes runtime detections across supply-chain incidents and new runner, HTTPS monitoring and SIEM integrations.
Key points
- StepSecurity reports that Harden-Runner protects more than 10,000 open-source repositories and monitors over 13 million jobs weekly; its Community Tier is free for public repositories.
- The company describes Harden-Runner as runtime security for CI/CD runners, monitoring workflow processes, network activity and files, with controls including network egress management.
- StepSecurity says Harden-Runner flagged suspicious behavior in the tj-actions/changed-files compromise before public disclosure, helping affected organizations respond to potential credential theft and code tampering.
- For the 2025 s1ngularity compromise involving Nx packages, StepSecurity says runtime monitoring flagged unexpected calls to api[.]github[.]com and credential-theft activity associated with a malicious post-install script.
- The article describes detections during security research on Flank and Microsoft's Azure Karpenter Provider: anomalous outbound activity was flagged, and StepSecurity says it reported the latter issue to Microsoft within an hour.
- Platform developments include HTTPS request monitoring, exporting detections to Amazon S3 for SIEM integration, and support for embedding Harden-Runner in GitHub-hosted custom runner images.
Article Details
- Event Type
- StepSecurity announced that Harden-Runner now protects more than 10,000 open-source repositories and described detections of CI/CD supply-chain attacks.
- Impact
- StepSecurity reports that Harden-Runner monitors more than 13 million jobs weekly and detected suspicious activity in several reported supply-chain incidents. In the tj-actions/changed-files and Nx incidents, malicious code reportedly exposed developer secrets to potential theft; the article says Harden-Runner flagged anomalous behavior. It also describes detection of ethical security research exercises on Flank and Azure Karpenter Provider. No resulting credential theft, code tampering, or other downstream compromise is reported.
MITRE ATT&CK
Vendors
Products
Azure Karpenter ProviderMicrosoft Azure Karpenter Provider: Real-Time Detection in a High-Trust ProjectBackstageWhen the Shai Hulud supply chain attack targeted CNCF's Backstage repository, Harden-Runner was there to catch it. This attack represented a new category of threat, one that traditional security tools weren't designedFlankFlank: Detecting a Real Supply Chain AttackGitHub Actionsmobile testing project, Harden-Runner detected it in real time. The researcher exploited a vulnerable GitHub Actions workflow to gain access to an elevated GITHUB_TOKEN with write permissions to the repository. TheyHarden-RunnerHarden-Runner now protects over 10,000 open-source repositories. Harden-Runner is also used by companies across open source, security, and enterprise environments. A public list of organizations using Harden-Runner isNxs1ngularity: Nx Package Compromise and AI CLI Weaponizationtj-actions/changed-filesof our most significant detections, Harden-Runner flagged suspicious behavior in the widely-used tj-actions/changed-files Action before any public disclosure. The Action had been compromised through a sophisticated
Tools
ClaudeThe malware also attempted to abuse local AI CLI tools such as Claude, Gemini, and q to help with reconnaissance and data collection, marking a new escalation in supply chain attacker tradecraft. GeminiThe malware also attempted to abuse local AI CLI tools such as Claude, Gemini, and q to help with reconnaissance and data collection, marking a new escalation in supply chain attacker tradecraft. qThe malware also attempted to abuse local AI CLI tools such as Claude, Gemini, and q to help with reconnaissance and data collection, marking a new escalation in supply chain attacker tradecraft.
Industries
CybersecurityGoogle RunCISA (Cybersecurity and Infrastructure Security Agency) – Supporting secure build practices in projects tied to critical infrastructure and national security.Software developmentused open-source projects and ecosystems in the world. These projects sit at the core of modern software development and infrastructure, which makes their CI/CD pipelines especially attractive targets for supply