Impacket `reg` Walkthrough Demonstrates Remote Registry Access, Credential Harvesting and Persistence
Summary
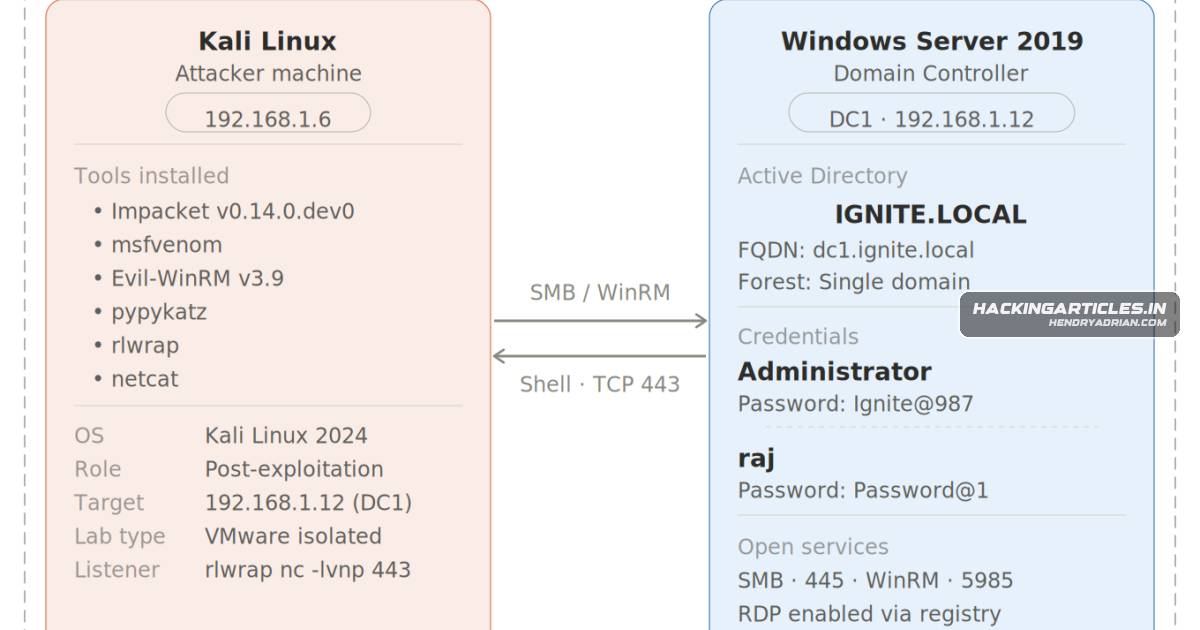
A lab walkthrough shows how Impacket `reg` can use authenticated SMB access to enumerate and modify a Windows registry, export credential hives, enable RDP and establish Run-key persistence, alongside defensive monitoring and hardening guidance.
Key points
- The walkthrough demonstrates password, NTLM hash, AES Kerberos key and ticket-cache authentication to a Windows Server 2019 domain controller over SMB.
- Remote registry queries reveal system configuration, services and installed software for post-exploitation reconnaissance.
- SAM, SYSTEM and SECURITY hives can be exported to an SMB share and parsed offline to recover local account hashes without accessing LSASS memory.
- Registry writes can enable RDP and create or remove keys and values, supporting lateral movement and configuration changes.
- The lab chain transfers a reverse-shell payload and registers it under the Windows Run key for execution at logon.
- Suggested defenses include restricting RemoteRegistry and SMB access, protecting privileged credentials and registry hives, and monitoring Run-key changes, remote-registry activity and outbound connections.
Article Details
- Topic
- Remote Windows registry post-exploitation with impacket-reg in an isolated Active Directory lab
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 192[.]168[.]1[.]6 | Operator-controlled Kali host used as the registry-hive export destination and reverse-shell callback listener in the isolated lab demonstration. |
MITRE ATT&CK
T1003.002 · Security Account ManagerExports SAM and SYSTEM registry hives and uses pypykatz to extract local account NTLM hashes offline.T1007 · System Service DiscoveryEnumerates registered Windows services through HKLM\SYSTEM\CurrentControlSet\Services.T1012 · Query RegistryQueries remote registry keys to enumerate operating system configuration, services, and installed applications.T1021.001 · Remote Desktop ProtocolConnects to the domain controller through RDP after enabling it through a registry modification.T1021.002 · SMB/Windows Admin SharesUses authenticated SMB and the winreg named pipe for remote registry operations.T1021.006 · Windows Remote ManagementUses Evil-WinRM to establish an authenticated remote session on the domain controller.T1105 · Ingress Tool TransferUploads a generated reverse-shell executable to the target through Evil-WinRM.T1112 · Modify RegistryRemotely creates, changes, and deletes registry keys and values, including settings that enable RDP.T1518 · Software DiscoveryEnumerates installed applications through the registry Uninstall key.T1547.001 · Registry Run Keys / Startup FolderRegisters the reverse-shell executable under the Windows Run key for execution at user logon.T1550.002 · Pass the HashAuthenticates to the remote registry using an NTLM hash instead of a plaintext password.T1550.003 · Pass the TicketReuses an existing Kerberos ticket cache for authenticated remote registry access.
Vendors
Products
Active DirectoryFor penetration testers, remote registry read/write access without an interactive session ranks among the most powerful post-exploitation capabilities in an Active Directory environment.KaliBefore dumping hives, the operator starts an SMB server on the Kali machine using impacket-smbserver.Windows Server 2019This article presents a complete, end-to-end attack chain using impacket-reg against a Windows Server 2019 domain controller in the ignite.local lab.
Tools
Evil-WinRMUploading the Payload via Evil-WinRMImpacketImpacket for Pentester: regimpacket-regThis article presents a complete, end-to-end attack chain using impacket-reg against a Windows Server 2019 domain controller in the ignite.local lab.impacket-smbserverBefore dumping hives, the operator starts an SMB server on the Kali machine using impacket-smbserver.Metasploit FrameworkMsfvenom, part of the Metasploit Framework, generates self-contained executable payloads.msfvenomGenerating a Reverse Shell Payload with Msfvenomnetcatrlwrap nc -lvnp 443pypykatzExtracting NTLM Hashes with PypykatzrdesktopWith RDP now enabled, the operator connects from Kali using rdesktop — a Linux-native RDP client — to establish a full graphical desktop session on the domain controller.rlwraprlwrap nc -lvnp 443