
CloudSEK Dataset Reports 78,330 Secrets Exposed in Team PCP Campaign
Summary
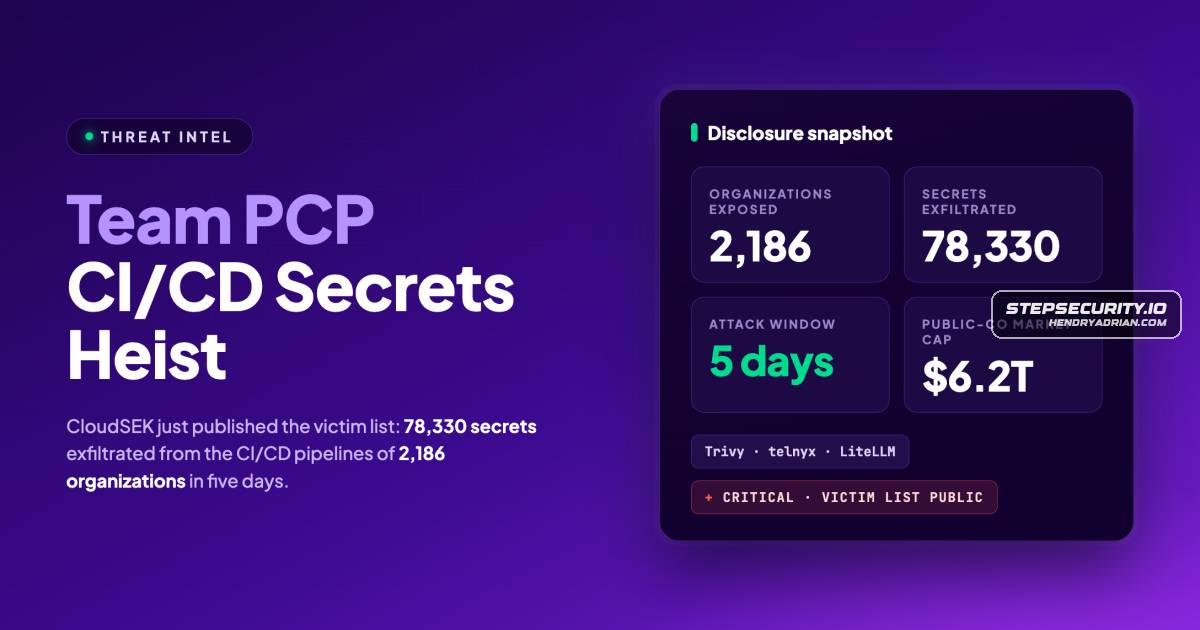
StepSecurity's analysis of CloudSEK's dataset reports 78,330 secrets exposed across CI/CD pipelines at 2,186 organizations from March 19–24, 2026, and outlines credential-rotation, audit, dependency-pinning and runner-control measures.
Key points
- StepSecurity says CloudSEK's dataset records 78,330 distinct secrets across 2,186 organizations during March 19–24, 2026; the article does not independently verify each exposure.
- The dataset analysis lists GitLab for 1,064 organizations, GitHub Actions for 618, Azure DevOps for 233 and Jenkins for 105; some organizations used multiple platforms.
- Reportedly exposed credentials include JWTs, private keys, AWS access keys, GitLab and GitHub tokens, and OpenAI API keys.
- StepSecurity attributes the campaign to Team PCP and describes compromised open-source components harvesting CI/CD runner secrets for use in further compromises.
- The article highlights runner secrets accessible to pipeline steps, unrestricted outbound connections and mutable dependency references as risks across CI/CD platforms.
- Recommended responses include rotating exposed credentials, reviewing access logs, pinning dependencies to immutable references, and applying runtime monitoring and network-egress controls to runners.
Article Details
- Event Type
- Supply-chain credential theft campaign and disclosure of an exposure dataset.
- Impact
- The article reports that, in March 2026, Team PCP exfiltrated 78,330 secrets from CI/CD pipelines associated with 2,186 organizations over five days. StepSecurity's analysis of the CloudSEK dataset says 92 publicly traded companies were affected, with a combined market capitalization above $6.2 trillion. Exposed credentials included cloud keys, source-control tokens, private keys, and API keys.
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe article says stolen secrets were sent from CI/CD runners over outbound connections to attacker C2, describing exfiltration over a C2 channel.T1195.001 · Compromise Software Dependencies and Development ToolsThe article describes compromising trusted open-source components and planting credential-stealing code in them, consistent with compromise of software dependencies and development tools.
Threat Actors
Malware
Vendors
Products
Azure DevOpsWhen you decode which system each victim organization was running, GitLab leads by a wide margin, and Azure DevOps, which is often left out of these conversations, appears in more than 230 organizations. A separateCheckmarx KICSPCP injected a credential stealer into 76 of the 77 version tags of the Trivy GitHub Action, hit the Checkmarx KICS action days later with the same technique, planted a WAV steganography credential stealer in theGitHub ActionsThis was not a GitHub Actions story. When you decode which system each victim organization was running, GitLab leads by a wide margin, and Azure DevOps, which is often left out of these conversations, appears in moreGitLabEvery major CI/CD platform was hit. GitLab led.LiteLLMtechnique, planted a WAV steganography credential stealer in the telnyx PyPI package, and compromised LiteLLM in what CloudSEK describes as the largest supply chain attack targeting AI infrastructure to date. It isTrivyis extensive. In March 2026, Team PCP injected a credential stealer into 76 of the 77 version tags of the Trivy GitHub Action, hit the Checkmarx KICS action days later with the same technique, planted a WAV