
Krybit Claims Ransomware Attack on Resi
Summary
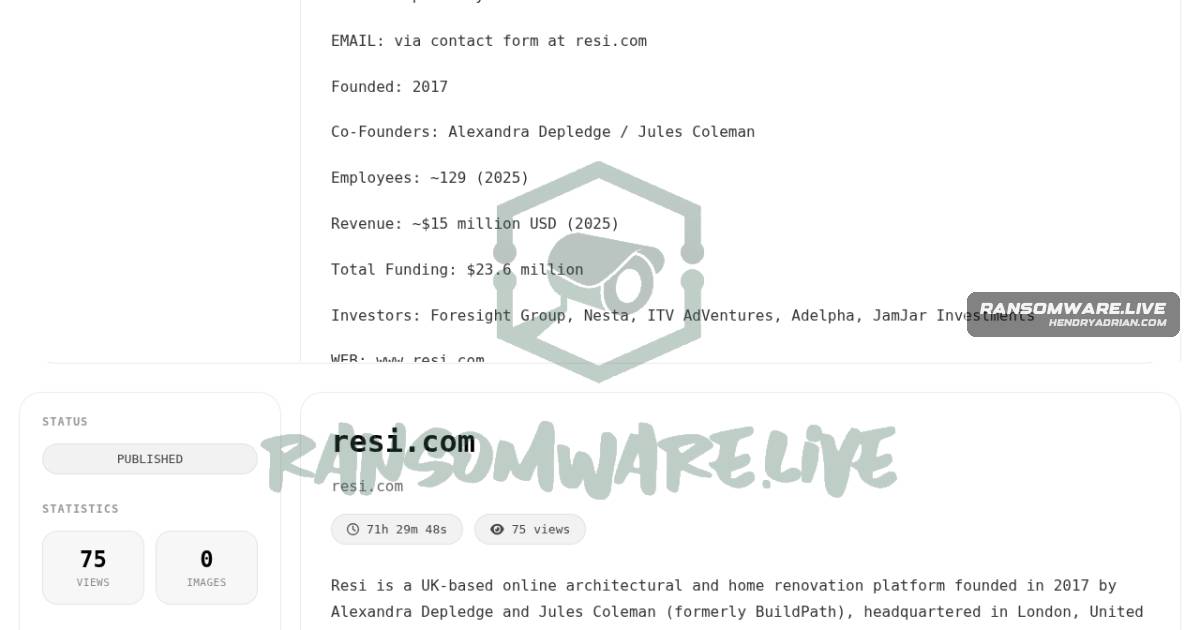
ransomware[.]live records an unverified Krybit claim targeting resi[.]com, a UK-based architectural and home-renovation platform. The post cites the group’s onion-site listing; no independent confirmation is provided.
Key points
- The monitoring record names resi[.]com as the alleged victim and Krybit as the ransomware actor.
- It attributes the claim to a post on Krybit’s onion blog.
- The record lists discovery and publication dates of August 24, 2026.
- The publisher says it cannot confirm the claim and invites an official statement from Resi.
Article Details
- Victim
- resi.com
- Victim Domain
- resi.com
- Claim Date
- 2026-08-24
- Encryption Status
- Unknown
- Encrypted Size
- Unknown
- Exfiltration Status
- Unknown
- Exfiltrated Data
- Unknown
- Exfiltrated Size
- Unknown
- Ransom Demand
- Unknown
- Leak Status
- A claim was posted on krybit's blog; publication of victim data is not reported or confirmed.