
Attackers Abuse Faronics Deploy to Install ConnectWise ScreenConnect
Summary
Huntress says phishing actors used Faronics Deploy to enroll victims and run scripts installing ScreenConnect. Faronics confirmed the abuse, added anti-abuse measures and notified affected organizations.
Key points
- Huntress observed Faronics-themed phishing lures reaching more than 457 endpoints between July 21 and August 20.
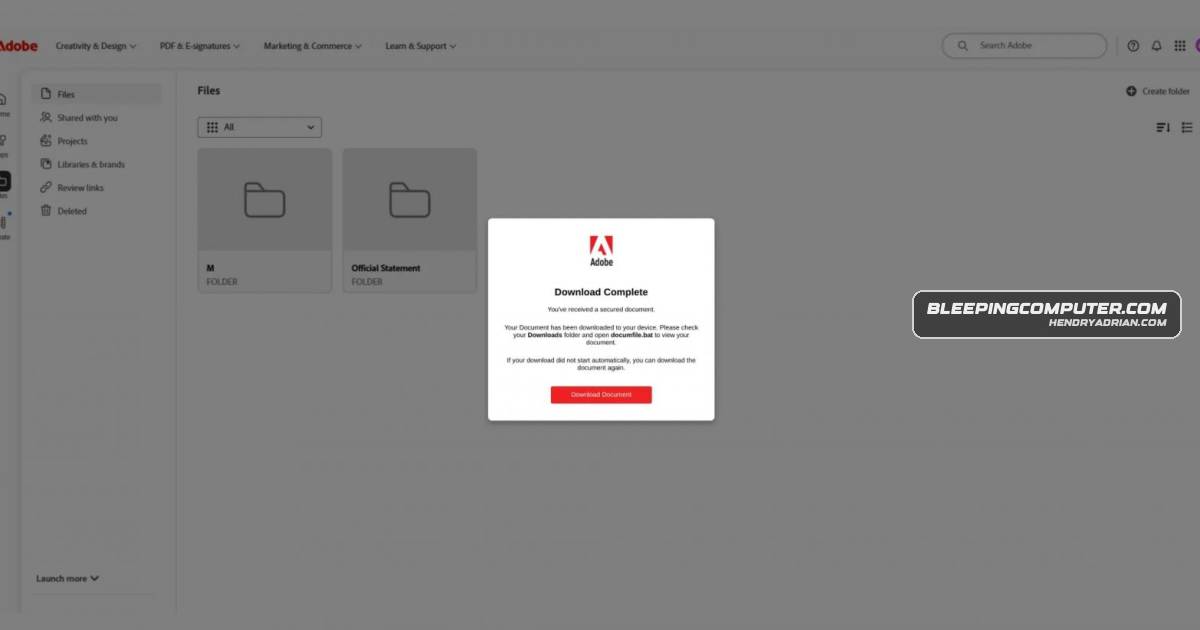
- The lures led victims to download a legitimate, signed Faronics Deploy installer disguised as an Adobe document, reader app or plugin update.
- After devices were enrolled in attacker-controlled deployments, attackers used Faronics remote-deployment features to run PowerShell scripts.
- Scripts used methods including curl, mshta and msiexec to retrieve additional tools and install ConnectWise ScreenConnect.
- ScreenConnect provided a separate remote-access channel that could remain available if the malicious Faronics deployment was removed.
- Faronics confirmed the activity, added anti-abuse measures and contacted affected organizations; Huntress said activity dropped significantly starting August 21.
- Huntress recommends checking Faronics logs and configuration requests for indicators, and looking for ScreenConnect installations where they are not normally deployed.
Article Details
- Event Type
- Phishing campaign abusing Faronics Deploy to enroll victim devices and install ConnectWise ScreenConnect.
- Impact
- Faronics-themed lures reached more than 457 endpoints. On devices where victims ran the disguised installer, attackers used Faronics remote-deployment features to execute PowerShell scripts, download additional tools, and install ScreenConnect for remote access. Faronics added anti-abuse measures and contacted affected organizations; Huntress reported that activity dropped significantly starting August 21.
MITRE ATT&CK
T1059.001 · PowerShellAttackers used PowerShell scripts through Faronics remote-deployment functionality.T1072 · Software Deployment ToolsAttackers abused Faronics Deploy's remote software-deployment features to run scripts on enrolled computers.T1105 · Ingress Tool TransferScripts retrieved additional content and tools from attacker infrastructure or external locations.T1204.002 · Malicious FileVictims were prompted to run a legitimate Faronics installer disguised as an Adobe-related file.T1219 · Remote Access ToolsAttackers installed ConnectWise ScreenConnect as an additional remote-access channel.T1566.002 · Spearphishing LinkPhishing emails contained malicious links leading to a target-profiling website and download flow.
Vendors
ConnectWisePhishing actors are abusing the legitimate Faronics Deploy platform to enroll victim devices and use remote deployment features to run PowerShell scripts that install ConnectWise ScreenConnect.FaronicsPhishing actors are abusing the legitimate Faronics Deploy platform to enroll victim devices and use remote deployment features to run PowerShell scripts that install ConnectWise ScreenConnect.
Products
ConnectWise ScreenConnectPhishing actors are abusing the legitimate Faronics Deploy platform to enroll victim devices and use remote deployment features to run PowerShell scripts that install ConnectWise ScreenConnect.Faronics DeployPhishing actors are abusing the legitimate Faronics Deploy platform to enroll victim devices and use remote deployment features to run PowerShell scripts that install ConnectWise ScreenConnect.