ClickFix Campaign Steals Facebook Sessions from Creators Through Fake Verification Pages
Summary
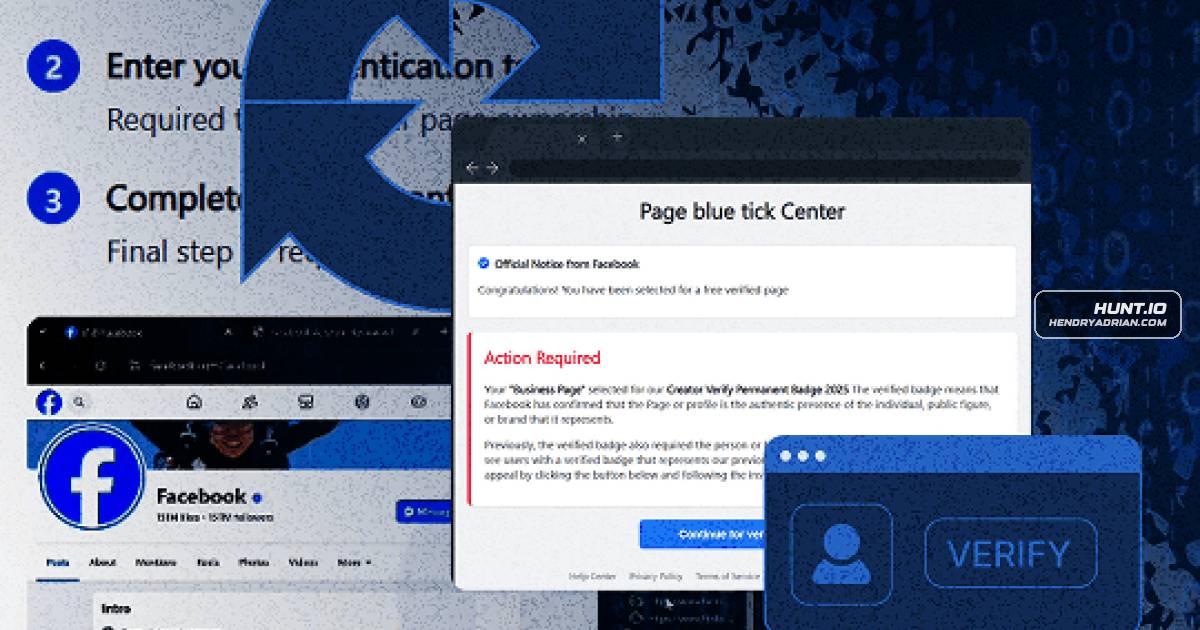
A multi-stage Facebook phishing campaign tricks creators into submitting session cookies, backup codes, and passwords. Researchers identified 115 pages, eight collection endpoints, and reused infrastructure supporting the account-takeover workflow.
Key points
- Fake Facebook badge, appeal, and security-verification pages guide victims to extract and submit the c_user and xs session cookies.
- The campaign uses staged lures and redirects; researchers identified 115 pages and a title-based pivot found 103 hostnames active since January 2025.
- Stolen tokens are sent through third-party form services, including submit-form.com, Formspark, and shiper.app, decoupling collection from phishing-page hosting.
- If session replay fails, the workflow can collect backup codes and passwords as alternative access paths.
- Some pages profile visitors by IP, proxy use, and location to vary the attack flow; some exfiltration endpoints are obfuscated in page code.
- The article recommends tracking reused page titles and templates, monitoring collection endpoints, and capturing short-lived phishing pages and their requests for analysis.
Article Details
- Attack Vectors
- Facebook-themed verification, appeal, and security-confirmation lures direct victims through staged phishing pages.
- Instructional videos coach victims to extract and submit the c_user and xs Facebook session cookies from browser developer tools.
- The workflow captures backup or security codes and Facebook passwords when session-token replay is unavailable.
- JavaScript performs token validation, environment profiling, and automatic submission of stolen data to collection endpoints.
- Defensive Notes
- Track and block the campaign's collection endpoints as well as rotating lure pages.
- Alert on pages requesting c_user and xs values in verification, appeal, badge, or security-confirmation workflows.
- Use recurring page titles and template structure to identify related infrastructure.
- Monitor lure pages for IP, proxy, and geolocation checks and preserve HTML, JavaScript, screenshots, and request logs promptly.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | 1-free-reward[.]netlify[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | activation-form[.]vercel[.]app | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | appeal-request-here-plum[.]vercel[.]app | Stage 1/2 appeal-phishing infrastructure. |
| DOMAIN | appeal-restricted-monetize-issue[.]netlify[.]app | Stage 1/2 appeal-phishing infrastructure. |
| DOMAIN | appeal-to-get-free-verified-badge-bluetick[.]vercel[.]app | Stage 1/2 appeal-phishing infrastructure. |
| DOMAIN | appeals[.]neocities[.]org | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | apply-for-badge-blue-tick[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | apply-for-blue-badge-subscription-2025[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | apply-for-free-badge-here-t3nl[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | apply-for-free-verified-badge-one[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | apply-free-tick[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | apply-get-badge[.]org | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | apply-get-tick[.]netlify[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | apply-get-verified-badge-eight[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | apply-now-meta-free-verfied-badge-m[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | apply-re-for-verification-badge[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | apply-subscrption-free-verified-badge[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | applyfor-bluebadge[.]vercel[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | badge-get-blue-verified-tick[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | badge-now-free-apply-subscription[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | badge-opportunity-free[.]surge[.]sh | Related phishing attack variant with credential and token harvesting. |
| DOMAIN | blue-tick-opportunity-us[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | blue-verification-free[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | blue-verified-bluetick-badges[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | bluetick-opportunity-for-creators-badge[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | chatbot[.]pagehelppro[.]xyz | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | claim-verification-badge[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | claim-your-badgeforfree-here[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | claimbluesignnow[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | claimyourbluesign2025[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | click-to-apply[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | collact-reward[.]netlify[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | complete-your-verification[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | easy-blue-tick[.]surge[.]sh | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | eligible-apply-for-free-badge[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | enjoy-free-blue-badge[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | enroll-reward[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | faceauth-dev[.]pages[.]dev | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | faceauth[.]pages[.]dev | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | fb-badge-reward[.]netlify[.]app | Facebook-themed Stage 1/2 phishing infrastructure. |
| DOMAIN | fb-terms[.]vercel[.]app | Facebook-themed Stage 1/2 phishing infrastructure. |
| DOMAIN | fil-here[.]netlify[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | file-panel[.]netlify[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | filing-application[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | form-apply-here-meta[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | free-blue-tick-get-now[.]org | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | free-collect-lifetime-badge[.]vercel[.]app | Second-stage phishing page receiving victims redirected from the initial lure. |
| DOMAIN | free-get-badge[.]netlify[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | free-get-reward[.]netlify[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | free-opportunity-apply-verified-badge-blue-tick[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | free-reward-m[.]netlify[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | free-rewards-h[.]wasmer[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | free-verfied-badge-opportunity-for-creators-two[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | free-verified-badge-service-here[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | free-verified-badge-service-two[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | free-verified-progrm[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | get-badge-appeal-just-now[.]vercel[.]app | Stage 1/2 appeal-phishing infrastructure. |
| DOMAIN | get-badge-becomeverified[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | get-blue-badge1066843[.]vercel[.]app | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | get-blue-mark[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | get-blue-program[.]vercel[.]app | Facebook verification-themed phishing infrastructure identified in the campaign. |
| DOMAIN | get-free-blue-badge-service[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | get-lifetime-badge-v[.]vercel[.]app | Initial phishing entry point masquerading as a face-verification page. |
| DOMAIN | get-lifetime-badges[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | get-official-badge[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | get-on-blue[.]surge[.]sh | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | get-permanent-badge[.]org | Verification-themed phishing infrastructure identified in the campaign. |
| DOMAIN | get-verification-for-service[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | great-news-get-free-verified[.]wasmer[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | harryxstar1010[.]github[.]io | Final-stage phishing page identified in the campaign IOC list. |
| DOMAIN | here-you-can-apply-free-verified[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | inf0-applying-center[.]vercel[.]app | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | info-apply-free-blue-badge-here[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | info-free-mark[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | info-required-rho[.]vercel[.]app | Post-submission redirect to another page in the phishing workflow. |
| DOMAIN | info-required[.]vercel[.]app | Redirect destination in the phishing workflow, including after failed submission. |
| DOMAIN | info-selected-your-verified-badge[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | info-setup-badge[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | jdbd7[.]github[.]io | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | jdhdu7[.]github[.]io | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | join-now-program[.]surge[.]sh | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | lifetime-blue-tick[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | lifetime-free-blue-page-f[.]surge[.]sh | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | nizzzzz7[.]github[.]io | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | now-appeal-bad-post-center-here[.]vercel[.]app | Stage 1/2 appeal-phishing infrastructure. |
| DOMAIN | now-appeal-bad-post[.]vercel[.]app | Stage 1/2 appeal-phishing infrastructure. |
| DOMAIN | now-blue-tick-get-free[.]vercel[.]app | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | now-free-apply-subscription-badge[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | now-free-request-here[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | now-request-badge[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | nsishahhs[.]github[.]io | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | okpoi98[.]github[.]io | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | permanent-bluetick[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | permanent-reward-03[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | permanent-reward-04[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | raheel77665544332211[.]github[.]io | Final-stage phishing page identified in the campaign IOC list. |
| DOMAIN | re-hi-review-issue-check[.]surge[.]sh | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | re-hi-review-issue-check1[.]surge[.]sh | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | request-for-badge-two[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | request-for-free-verified-badge-amber[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | request-for-review-remove-here[.]wasmer[.]app | Stage 1/2 phishing infrastructure identified in the campaign. |
| DOMAIN | request-to-verify-page[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | resolve-newissue-here[.]surge[.]sh | Second-stage phishing page receiving victims redirected from a lure. |
| DOMAIN | review-new-issue[.]neocities[.]org | Initial phishing lure that redirects victims to a second-stage page. |
| DOMAIN | review-restriction-notice[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | securityverificationrequired[.]github[.]io | Final-stage phishing page identified in the campaign IOC list. |
| DOMAIN | shavlal[.]github[.]io | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | submit-appeal-reviews[.]vercel[.]app | Stage 1/2 appeal-phishing infrastructure. |
| DOMAIN | submit-details-review[.]vercel[.]app | Final-stage phishing page identified in the campaign IOC list. |
| DOMAIN | submit-form-here[.]netlify[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | submit-here[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | submit-review-for-blue-badge[.]wasmer[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | thenuna98-gifr[.]github[.]io | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | tick-badge-approval[.]surge[.]sh | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | tick-trust-verify[.]surge[.]sh | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | verified-badge-support-fb[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | vidyamenon627477-wq[.]github[.]io | Final-stage phishing page identified in the campaign IOC list. |
| DOMAIN | viryfipage-done[.]github[.]io | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
| DOMAIN | winscottwood-glitch[.]github[.]io | Final-stage phishing page identified as capturing credentials. |
| DOMAIN | yingvera12345[.]github[.]io | Domain included in the article's query for reported campaign infrastructure. |
| DOMAIN | yingvera12348[.]github[.]io | Final-stage phishing page identified in the campaign IOC list. |
| DOMAIN | your-eligible-verified-badge-opportunity[.]vercel[.]app | Stage 1/2 phishing infrastructure listed in the campaign IOCs. |
hermesanfacebookadvertising@gmail[.]com | Operator email present in commented exfiltration logic for the phishing flow. | |
itguy932@gmail[.]com | Operator email hardcoded into the automatic stolen-token submission payload. | |
mjohn72929@gmail[.]com | Operator email present in commented exfiltration logic for the phishing flow. | |
| IPV4 | 143[.]198[.]42[.]253 | IP address from the infrastructure pivot reported as flagged malicious by multiple security vendors. |
| IPV4 | 93[.]127[.]137[.]89 | IP address reported to resolve from the campaign's live environment-profiling endpoint. |
| URL | hxxps[:]//handle[.]gadgetsdecory[.]xyz:3000/anotherdc | Live endpoint used by phishing code for IP, proxy, and geolocation profiling. |
| URL | hxxps[:]//postal-form[.]on[.]shiper[.]app/notifyLogin | Endpoint used to send an additional notification when recovery codes are submitted. |
| URL | hxxps[:]//postal-form[.]on[.]shiper[.]app/submit | Form endpoint used to exfiltrate Facebook session tokens. |
| URL | hxxps[:]//submit-form[.]com/1FHQilMmM | Form-based data-theft endpoint listed in the campaign IOCs. |
| URL | hxxps[:]//submit-form[.]com/1v527LkNH | Endpoint receiving authentication tokens submitted through an appeal-phishing page. |
| URL | hxxps[:]//submit-form[.]com/9B1d9kugn | Form-based data-theft endpoint listed in the campaign IOCs. |
| URL | hxxps[:]//submit-form[.]com/cl2uWSEUd | Token-harvesting and credential-exfiltration endpoint identified in a related attack chain. |
| URL | hxxps[:]//submit-form[.]com/mtVclNJQR | Form-based data-theft endpoint listed in the campaign IOCs. |
| URL | hxxps[:]//submit-form[.]com/Yajvf9ABS | Form endpoint used to exfiltrate session tokens, security codes, and passwords. |
| URL | hxxps[:]//submit-form[.]com/z4M6ojyY3 | Obfuscated endpoint decoded from page code and used for exfiltration. |
| URL | hxxps[:]//submit-form[.]com/Z6EdHfXSR | Form-based data-theft endpoint listed in the campaign IOCs. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationHTML/JavaScript hides exfiltration endpoints using binary-encoded strings and Base64 fragments.T1036 · MasqueradingPhishing pages impersonate Facebook verification, appeal, Help Center, and security-confirmation workflows.T1071.001 · Web ProtocolsThe pages send collected tokens and credentials in HTTPS POST requests to collection endpoints.T1102.003 · One-Way CommunicationThird-party form backends are used as one-way channels to collect and forward stolen data.T1119 · Automated CollectionJavaScript automatically submits token values after their structure passes validation.T1204.001 · Malicious LinkVictims voluntarily follow links and continue through staged verification and appeal pages.T1555.003 · Credentials from Web BrowsersVictims are instructed to extract c_user and xs session cookies from browser developer tools.T1566.002 · Spearphishing LinkVictims are directed through multi-stage Facebook-themed phishing links.
Products
Countries
PakistanThe script performs an IP intelligence check via https://handle[.]gadgetsdecory[.]xyz:3000/anotherdc to determine proxy usage and geolocation, dynamically altering the attack flow for non-proxy users outside Pakistan.United States93.127.137[.]89 is associated with AS401479 (Database Mart LLC) and geolocated to Kansas City, United States. Hunt.io confirms that port 3000 (HTTP/TLS) is actively exposed and responding (HTTP 200), with