CISA Sets Patch Deadlines for Exploited Plex2Shell, Siemens and SiteGuard Flaws
Summary
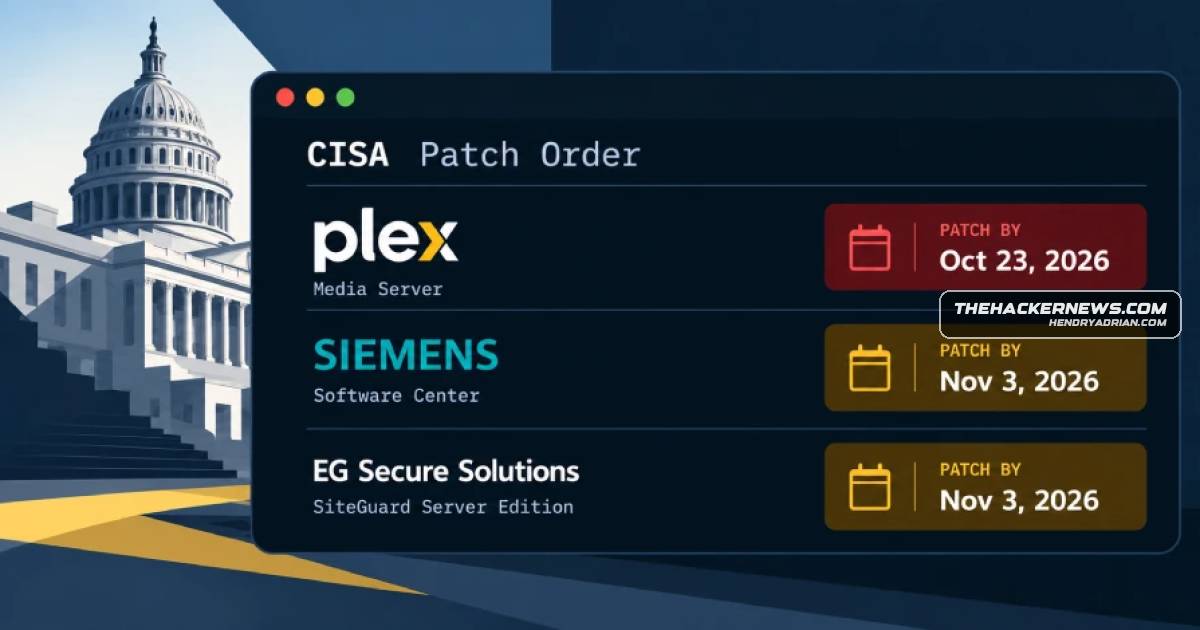
CISA added four Plex2Shell flaws to its KEV catalog and flagged exploited Siemens and SiteGuard flaws. Federal agencies must patch specified vulnerabilities by October 23 or November 3, 2026.
Key points
- CISA added four Plex Media Server vulnerabilities, collectively called Plex2Shell, to its Known Exploited Vulnerabilities catalog.
- Researcher Zach Main said the Plex flaws can be chained for unauthenticated remote code execution; Plex addressed them in version 1.43.3.10861, released August 3, 2026.
- A report by researcher boredhackerblog said threat actors are exploiting the Plex flaws to deploy cryptocurrency miners and proxy malware.
- CISA also flagged Siemens Software Center CVE-2026-110936, a DLL sideloading flaw reportedly abused in ClickFix attacks using Romulus.
- EG Secure Solutions confirmed exploitation of the SiteGuard Server Edition command injection flaw CVE-2026-106931; further exploitation details were unavailable.
- CISA set an October 23, 2026 deadline for FCEB agencies to patch CVE-2026-106931, CVE-2026-96656, and CVE-2026-96654, and November 3 for the remaining vulnerabilities.
Article Details
- Vulnerability Types
- Remote code execution
- DLL sideloading
- Command injection
- Affected Versions
- Plex Media Server versions before 1.43.3.10861
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
CVE-2026-106931The second security flaw is a command injection bug in EG Secure Solutions SiteGuard Server Edition (CVE-2026-106931, CVSS score: 8.5) that the Japanese company confirmed as being exploited. No additional detailsCVE-2026-110936as actively exploited. One of them is a DLL sideloading vulnerability in Siemens Software Center (CVE-2026-110936, CVSS score: 8.4) that has been abused in ClickFix attacks using a platform called Romulus.CVE-2026-96654CISA is urging Federal Civilian Executive Branch (FCEB) agencies to apply fixes for CVE-2026-106931, CVE-2026-96656, and CVE-2026-96654 by October 23, 2026, and the rest by November 3, 2026.CVE-2026-96656CISA is urging Federal Civilian Executive Branch (FCEB) agencies to apply fixes for CVE-2026-106931, CVE-2026-96656, and CVE-2026-96654 by October 23, 2026, and the rest by November 3, 2026.
People
Vendors
EG Secure SolutionsThe second security flaw is a command injection bug in EG Secure Solutions SiteGuard Server Edition (CVE-2026-106931, CVSS score: 8.5) that the Japanese company confirmed as being exploited. No additional detailsSiemenstwo other vulnerabilities as actively exploited. One of them is a DLL sideloading vulnerability in Siemens Software Center (CVE-2026-110936, CVSS score: 8.4) that has been abused in ClickFix attacks using a
Products
Plex Media Serverto its Known Exploited Vulnerabilities (KEV) catalog, including four vulnerabilities impacting Plex Media Server that's collectively called Plex2Shell.Siemens Software Centerother vulnerabilities as actively exploited. One of them is a DLL sideloading vulnerability in Siemens Software Center (CVE-2026-110936, CVSS score: 8.4) that has been abused in ClickFix attacks using a platformSiteGuard Server EditionThe second security flaw is a command injection bug in EG Secure Solutions SiteGuard Server Edition (CVE-2026-106931, CVSS score: 8.5) that the Japanese company confirmed as being exploited. No additional details