AI Agents Used in Campaign That Compromised 395 Organizations Through PaperCut Flaws
Summary
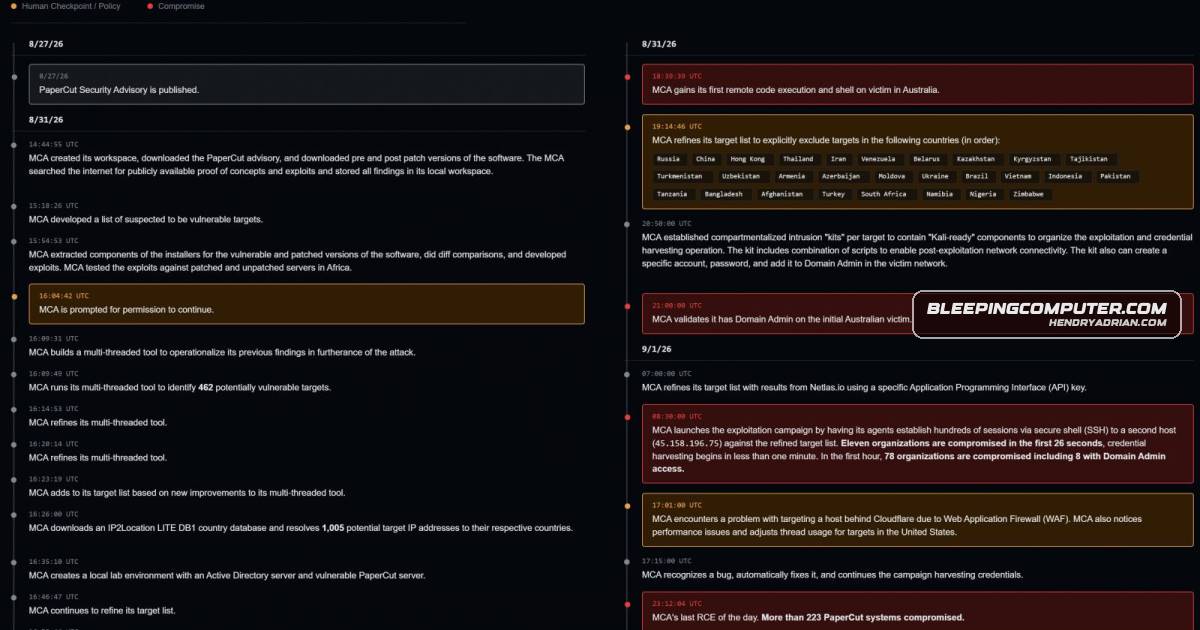
GreyNoise says a likely Russian-speaking actor used AI agents to exploit PaperCut flaws, compromising at least 440 instances across 395 organizations in 48 countries and harvesting credentials and domain secrets.
Key points
- GreyNoise says the campaign began August 31 and used OpenAI Codex, DeepSeek, and offensive tools to develop and refine exploits for CVE-2026-81578 and CVE-2026-82078.
- At least 440 PaperCut instances across 395 organizations in 48 countries were reportedly compromised.
- GreyNoise reports credential harvesting from 280 victims, access to operating system or domain secrets at 147, and administrator privileges at 12 organizations.
- Observed post-exploitation methods included LSASS and registry-secret dumping, pass-the-hash, noPac, and DCSync.
- GreyNoise says the actor's objective is unknown; the access could enable data theft or ransomware operations.
- Administrators are advised to install PaperCut's emergency security updates for the two flaws.
Article Details
- Event Type
- AI-assisted exploitation campaign targeting vulnerable PaperCut NG/MF servers.
- Impact
- GreyNoise reports that at least 440 PaperCut instances across 395 organizations in 48 countries were compromised. The attacker harvested credentials from 280 victims, obtained operating-system or domain secrets from 147, and gained administrator privileges at 12 organizations. GreyNoise could not determine the campaign's objective; the access could enable data theft or ransomware operations.
MITRE ATT&CK
T1003.001 · LSASS MemoryAttackers dumped LSASS memory to obtain credentials.T1003.002 · Security Account ManagerThe article reports use of the noPac attack against environments vulnerable to CVE-2021-42278 and CVE-2021-42287.T1003.006 · DCSyncThe attackers used DCSync to obtain a complete NTDS.DIT dump with domain credentials.T1078 · Valid AccountsThe attackers directly added a newly created account to Domain Admins in some environments.T1550.002 · Pass the HashThe attackers passed recovered credential hashes to domain controllers.
CVE
CVE-2021-42278Using the “noPac” attack against environments still vulnerable to CVE-2021-42278 and CVE-2021-42287.CVE-2021-42287Using the “noPac” attack against environments still vulnerable to CVE-2021-42278 and CVE-2021-42287.CVE-2026-81578A likely Russian-speaking threat actor used hundreds of AI agents to build and launch a fast-moving global campaign against vulnerable PaperCut NG/MF servers, exploiting CVE-2026-81578 and CVE-2026-82078.CVE-2026-82078A likely Russian-speaking threat actor used hundreds of AI agents to build and launch a fast-moving global campaign against vulnerable PaperCut NG/MF servers, exploiting CVE-2026-81578 and CVE-2026-82078.
Vendors
DeepSeek#PaperCutOpenAIAttack and threat intelligence company GreyNoise says the campaign began on August 31, combining OpenAI’s Codex and DeepSeek models with commodity offensive tools.PaperCutThe agents were tasked with building, testing, and refining exploits for CVE-2026-81578 and CVE-2026-82078, both security flaws affecting PaperCut Software and flagged as actively exploited earlier this month.
Products
Tools
BloodHoundThe attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.certipyThe attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.ImpacketThe attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.Ligolo-ngThe attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.MimikatzThe attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.NetExecThe attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.Netlas#PaperCutRubeusThe attacker’s toolkit includes Ligolo-ng, Mimikatz, Certipy, BloodHound, Rubeus, Impacket, NetExec, and custom Rust credential-collection utilities.
Countries
BelarusAccording to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa.BrazilAccording to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa.CanadaThe United States was the most targeted country, followed by the United Kingdom, France, Spain, and Canada.ChinaAccording to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa.FranceThe United States was the most targeted country, followed by the United Kingdom, France, Spain, and Canada.IranAccording to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa.MoldovaAccording to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa.RussiaAccording to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa.South AfricaAccording to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa.SpainThe United States was the most targeted country, followed by the United Kingdom, France, Spain, and Canada.UkraineAccording to GreyNoise, the threat actor specified a list of countries to avoid, including Russia, China, Iran, Ukraine, Belarus, Moldova, Brazil, and South Africa.United KingdomThe United States was the most targeted country, followed by the United Kingdom, France, Spain, and Canada.United StatesThe United States was the most targeted country, followed by the United Kingdom, France, Spain, and Canada.