
Deceptive Android Apps Exploit Google Play Early Access, Researchers Say
Summary
Bitdefender says thousands of deceptive apps exploit Google Play Early Access, where users cannot post reviews or ratings. Social ads promote fake rewards and casino apps; the article also describes related Android malware targeting users and devices.
Key points
- Bitdefender reports that threat actors are pushing thousands of deceptive apps through Google Play Early Access, where public reviews and ratings are unavailable.
- The apps promise cash, rewards, casino winnings or premium content; reported lures also include utilities and trademark-themed games.
- Bogus TikTok and Facebook ads, sometimes using AI-generated celebrity deepfakes, direct users to the apps or gambling sites.
- A reported scam pattern gives users virtual rewards but slows progress at withdrawal thresholds; the promised payout does not arrive, while repeated ads generate revenue.
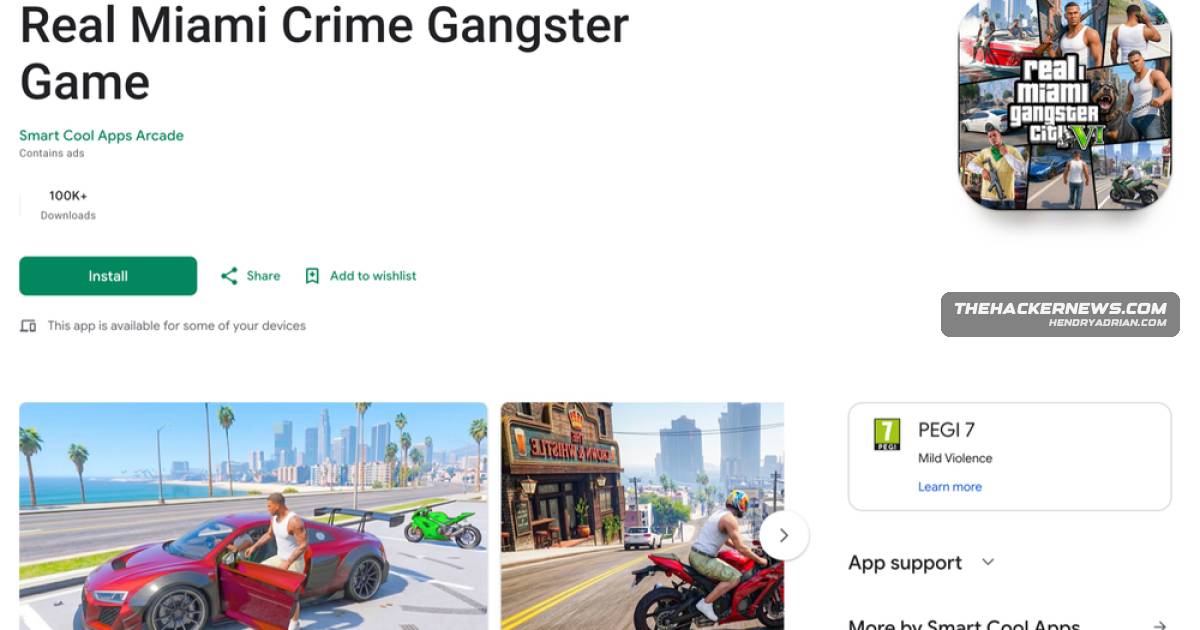
- A Grand Theft Auto imitator named “Vice Streets: Open World” reportedly had more than 1 million downloads and no ratings or reviews; it is no longer on Google Play, but the reason for its removal is unclear.
- The article also summarizes Hagaseca, Mantax Otax and StreamRat Android malware, and GoldFactory’s reported use of the Gigabud trojan with Vwork for financial fraud.
Article Details
- Event Type
- Abuse of Google Play Early Access to distribute deceptive Android apps, alongside reporting on Android malware used for fraud and device compromise.
- Impact
- Users may be deceived into installing apps that generate ad revenue or promise payouts that never arrive. The associated malware activity is reported to enable remote device control, data theft, ransomware, and financial fraud.
Threat Actors
Malware
GigabudThe activity overlaps with several Android threats, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory’s use of the Gigabud trojan and Vwork to enable fraud and device compromise.HagasecaThe activity overlaps with several Android threats, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory’s use of the Gigabud trojan and Vwork to enable fraud and device compromise.Mantax OtaxThe activity overlaps with several Android threats, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory’s use of the Gigabud trojan and Vwork to enable fraud and device compromise.StreamRatThe activity overlaps with several Android threats, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory’s use of the Gigabud trojan and Vwork to enable fraud and device compromise.THost9Hagaseca, a remote access trojan spread via the THost9 loader that contains a worm component, which scans exposed Android Debug Bridge (ADB) services and installs the malware for persistence and remote control throughVworkThe activity overlaps with several Android threats, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory’s use of the Gigabud trojan and Vwork to enable fraud and device compromise.
Vendors
Products
AndroidBad actors are abusing Google Play’s Early Access program to distribute deceptive Android apps that promise cash, rewards, casino wins, and premium content while evading public reviews and ratings.FacebookBogus ads on TikTok and Facebook spread the apps, often using AI-generated celebrity deepfakes.Google PlayBad actors are abusing Google Play’s Early Access program to distribute deceptive Android apps that promise cash, rewards, casino wins, and premium content while evading public reviews and ratings.Shelteruse of the Gigabud banking trojan to install a companion Android app called Vwork, a weaponized fork of Shelter, to clone a target app inside a work profile with the goal of conducting financial fraud.TikTokBogus ads on TikTok and Facebook spread the apps, often using AI-generated celebrity deepfakes.