Cleo File-Transfer Products Actively Exploited; Version 5.8.0.21 Still Vulnerable
Summary
Huntress reported active exploitation of Cleo Harmony, VLTrader, and LexiCom, including systems running version 5.8.0.21. It observed at least 10 compromised businesses and advised moving internet-exposed systems behind a firewall pending a new patch.
Key points
- Huntress said exploitation was observed as early as December 3, 2024, with at least 10 businesses compromised in its telemetry.
- The advisory says Cleo versions through 5.8.0.21 are vulnerable; Huntress reproduced exploitation on version 5.8.0.21 despite the earlier update.
- The observed attack used arbitrary file writes to place files in Cleo’s autorun directory, triggering PowerShell execution.
- Huntress observed attackers retrieving JAR files for webshell-like persistence and using nltest.exe for Active Directory reconnaissance.
- Cleo was preparing a new patch at the time of the advisory; disabling autorun processing was offered as an interim measure, but does not fix the arbitrary file-write flaw.
- Huntress recommended placing internet-exposed Cleo systems behind a firewall until a new patch is available.
Article Details
- Vulnerability Types
- Arbitrary file write
- Unauthenticated remote code execution
- Affected Versions
- Cleo Harmony: all versions prior to and including 5.8.0.21
- Cleo VLTrader: all versions prior to and including 5.8.0.21
- Cleo LexiCom: all versions prior to and including 5.8.0.21
- Exploitation Status
- active
- Exploit Availability
- claimed_or_private
- Patch Status
- unavailable
- Workarounds
- Move internet-exposed Cleo systems behind a firewall until a new patch is released.
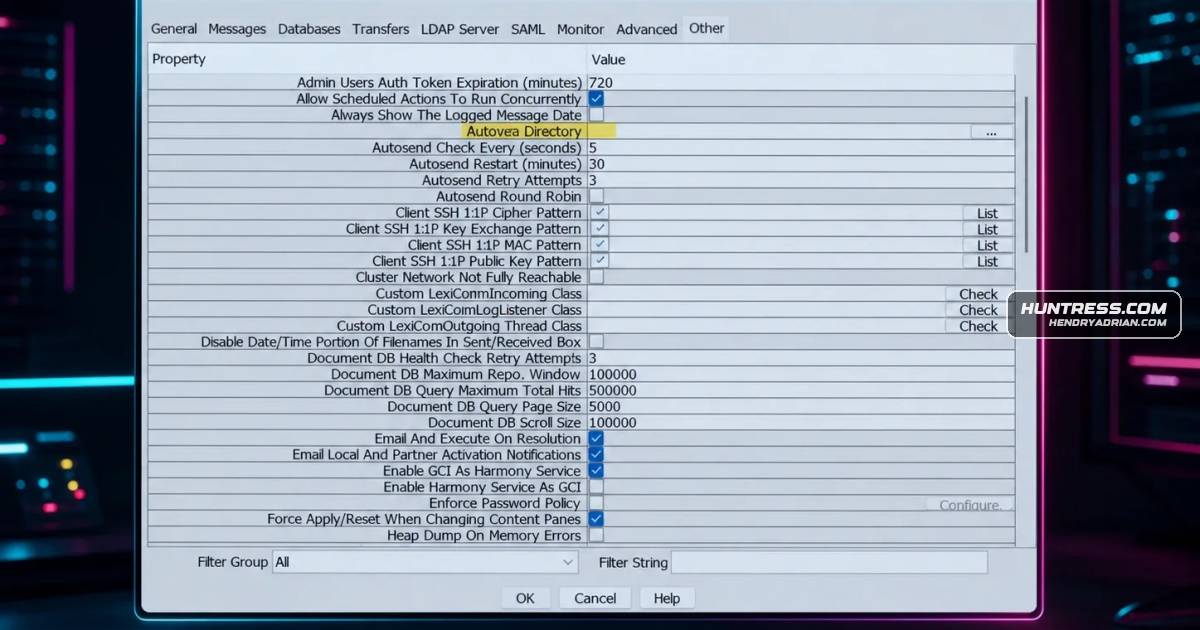
- Disable autorun processing by deleting the contents of the Autorun Directory field in the software’s Options.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 176[.]123[.]5[.]126 | Attacker IP embedded in encoded PowerShell and observed as callback infrastructure. |
| IPV4 | 181[.]214[.]147[.]164 | IP address observed for callbacks during the exploitation activity. |
| IPV4 | 185[.]181[.]230[.]103 | IP address observed for callbacks during the exploitation activity. |
| IPV4 | 192[.]119[.]99[.]42 | IP address observed for callbacks during the exploitation activity. |
| IPV4 | 209[.]127[.]12[.]38 | IP address observed for callbacks during the exploitation activity. |
| IPV4 | 5[.]149[.]249[.]226 | IP address observed for callbacks during the exploitation activity. |
MITRE ATT&CK
T1018 · Remote System DiscoveryThreat actors used nltest.exe to enumerate potential Active Directory assets.T1059.001 · PowerShellA staged autorun action invoked a PowerShell command to execute code.T1105 · Ingress Tool TransferThe PowerShell process reached an external IP address to retrieve JAR files.T1190 · Exploit Public-Facing ApplicationThreat actors exploited the Cleo software vulnerability on exposed systems.T1505.003 · Web ShellRetrieved JAR files contained webshell-like functionality used for persistence on endpoints.
CVE
People
Amelia CasleyHuntress analyst who generated an internal investigation guide for the threat.Austin WorlineHuntress SOC analyst who helped create detections for the activity.Caleb StewartHuntress Principal Security Researcher who crafted the Python proof-of-concept script.Chad HudsonHuntress SOC analyst who helped create detections for the activity.Jai MintonHuntress SOC analyst who helped create detections for the activity.Tanner FilipHuntress SOC analyst who helped create detections for the activity.
Vendors
Products
Tools
Countries
Canada209.127.12.38 - AS 55286 (SERVER-MANIA / B2 Net Solutions Inc) - CanadaLithuania181.214.147.164 - AS 15440 (UAB Baltnetos komunikacijos) - LithuaniaMoldova176.123.5.126 - AS 200019 (AlexHost SRL) - MoldovaNetherlands5.149.249.226 - AS 59711 (HZ Hosting Ltd) - NetherlandsUnited States192.119.99.42 - AS 54290 (HOSTWINDS LLC) - United States
Industries
Consumer productsThe majority of customers that we saw compromised deal with consumer products, food industry, trucking, and shipping industries.FoodThe majority of customers that we saw compromised deal with consumer products, food industry, trucking, and shipping industries.ShippingThe majority of customers that we saw compromised deal with consumer products, food industry, trucking, and shipping industries.TruckingThe majority of customers that we saw compromised deal with consumer products, food industry, trucking, and shipping industries.