DarkOwl Reports Increased Darknet Offers of Android RATs and Ransomware
Summary
DarkOwl analysts reported more Android RAT offerings on darknet forums in 2020, describing malware capabilities, COVID-themed lures, mobile ransomware, and distribution methods; some advertised tools’ effectiveness was unverified.
Key points
- DarkOwl analysts said Android RAT offers increased in 2020, with tools advertised for surveillance, data theft, and banking fraud.
- Cerberus developers reportedly offered their operation for auction before releasing its source code; Cerberus v2 was described as capable of stealing two-factor authentication codes.
- Alien was described as adding keylogging and notification monitoring to Cerberus capabilities; the article says it used TeamViewer for remote access.
- The article describes COVID-themed apps based on AhMyth and reports that a fake COVID-19 Tracker app locked phones and demanded $100 in bitcoin.
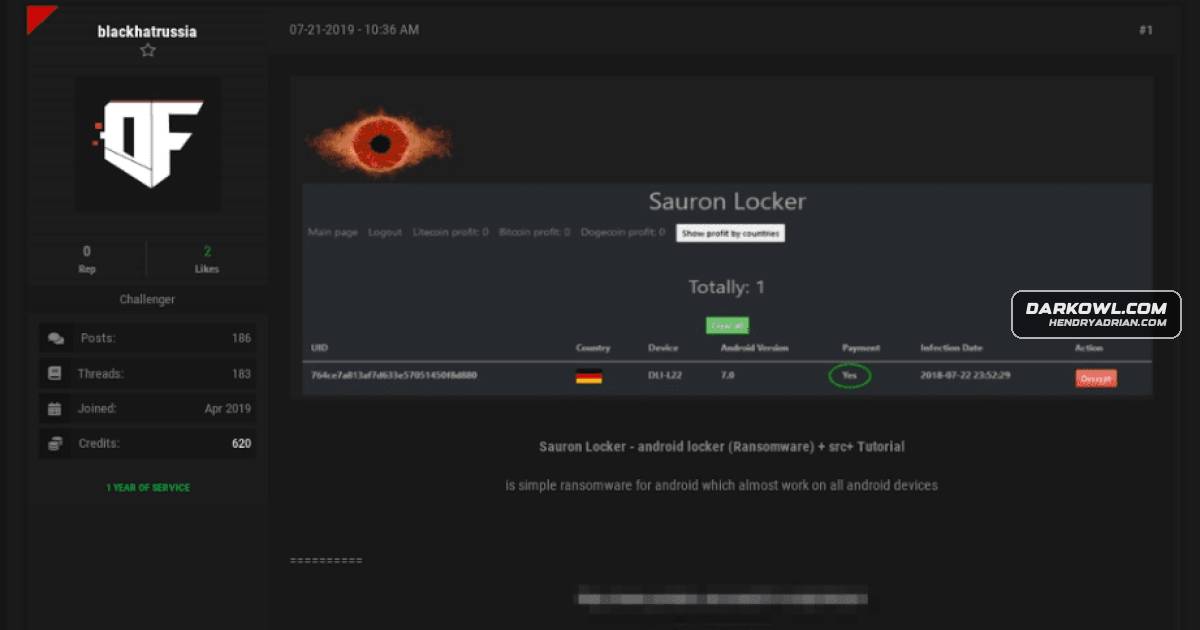
- Sauron Locker was reportedly distributed through a cracked Clash Royale game, with ransom demands said to vary by victim location.
- DarkOwl said it had not verified the effectiveness or severity of some advertised tools, including Xerxes Android Botnet and Oxyn-Android-Bot.
- The article identifies malicious app downloads, SMS, and phishing or vishing as delivery routes, and describes Android crypters marketed to evade antivirus detection.
Article Details
- Event Type
- Darknet intelligence report on the availability and use of Android-specific RATs and ransomware.
- Impact
- The malware described can surveil Android devices, steal authentication and banking data, access personal information, and lock or encrypt devices for extortion. DarkOwl reports use of malicious or disguised apps, including COVID-themed apps and a cracked game, to reach victims. The article also reports targeting of government organizations and individuals, and cites unverified darknet claims of more than 1,000 victims across 27 countries.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | tweensangoma[.]servebbs[.]com | C2 domain identified for an AhMyth RAT disguised as a COVID-19 testing app. |
| IPV4 | 122[.]10[.]114[.]159 | Public IP identified in the article as a hard-coded C2 address for a malicious COVID-themed Android app. |
| URL | hxxps[:]//github[.]com/dot-sec/Cyberpunk2077-android-malware | Specific repository identified as providing the Cyberpunk 2077-themed ransomware sample and APK. |
| URL | hxxps[:]//github[.]com/sk3ptre/AndroidMalware_2020 | Specific repository said to contain a list of COVID-titled Android RATs and live malware strains. |
MITRE ATT&CK
T1056.001 · KeyloggingAlien RAT is described as including a keylogger.T1204.002 · Malicious FileVictims are lured into downloading and installing disguised malicious Android apps.T1219 · Remote Access ToolsAlien RAT reportedly installs and leverages TeamViewer for remote control and observation of a victim's device.T1486 · Data Encrypted for ImpactThe article describes ransomware encrypting device files and locking devices for extortion.T1566 · PhishingThe article describes phishing as a delivery vector for Android malware.
Threat Actors
@CodersanNamed as the developer of BlackKingdom Coderware, distributed through a fake Cyberpunk 2077 Android app.@zEdHacKsNamed as the developer advertising the Xerxes Android Botnet.blackhatrussiaForum user reported to distribute malware, including Sauron Locker, on hacking forums and a personal website.Cold_KillerForum user reported to offer access to Sauron Locker for cryptocurrency.megabyteDarknet forum user reported to offer a license for the Alien Android RAT.speedwap4Forum user reported to advertise Sauron Locker.Transparent TribeThe article attributes active exploitation of COVID-related tracking and monitoring apps to this group, to serve malicious mobile malware.TriangulumNamed in the article as the seller of the Rogue RAT, including its version 6.2.
Malware
AhMyththat threat actors are successfully deploying mobile ransomware such as “Sauron Locker” and RATs such as AhMyth, disguised as a COVID-19 testing app, designed to ‘exfiltrate’ or extract the contents of the mobileALIENWithin weeks of the Cerberus source code leaks, a fork of the initial variant of Cerberus (v1) called Alien surfaced for sale on the darknet.BlackKingdom CoderwareCyberpunk 2077 Android app to a fake website impersonating the Google Play store that installed BlackKingdom Coderware, developed by Telegram user “@Codersan” that subsequently encrypted all the device’s files,CerberusSince 2019, one of the most widely discussed RATs has been is Cerberus, particularly in the context of targeting banking applications supported by the Google Play store and Android mobile operating systems.CovidLockerCOVIDLOCKER & WANNALOCKEROX-LockerThe Oxyn-Android-Bot is similarly advertised to include the OX-Locker ransomware in addition to exfiltration of banking and personal data of the victim’s Android device.Oxyn-Android-BotThe Oxyn-Android-Bot is similarly advertised to include the OX-Locker ransomware in addition to exfiltration of banking and personal data of the victim’s Android device.Rogue RATFigure 3: Advertisement for Rogue RAT (Source: DarkOwl Vision)Sauron LockerDarkOwl discovered that threat actors are successfully deploying mobile ransomware such as “Sauron Locker” and RATs such as AhMyth, disguised as a COVID-19 testing app, designed to ‘exfiltrate’ or extract the contentsWannalockerCOVIDLOCKER & WANNALOCKERXerxes Android BotnetIn early February, a Telegram post included a link to the Xerxes Android Botnet advertised by a malware developer known as @zEdHacKs.
Vendors
GoogleSince 2019, one of the most widely discussed RATs has been is Cerberus, particularly in the context of targeting banking applications supported by the Google Play store and Android mobile operating systems.SupercellSauron Locker has been observed distributed to Android devices on a cracked version of the popular mobile game, Clash Royale originally developed by Supercell.TeamViewerThe Alien RAT successfully installs and leverages the commercial TeamViewer application in its operation on the victim’s mobile device providing the threat actors full remote control and observation of the device and
Products
Androidindiscriminately across industries, our analysts have also witnessed an increase in the offers of Android-based Remote Access Trojans/Tools (RATs).Clash RoyaleSauron Locker has been observed distributed to Android devices on a cracked version of the popular mobile game, Clash Royale originally developed by Supercell.Google AuthenticatorAn update to the RAT appeared in 2020 (v2) that has additional security-evasion functionalities, such as stealing two-step authentication (2FA) codes from apps like Google Authenticator.Google PlaySince 2019, one of the most widely discussed RATs has been is Cerberus, particularly in the context of targeting banking applications supported by the Google Play store and Android mobile operating systems.TeamViewerThe Alien RAT successfully installs and leverages the commercial TeamViewer application in its operation on the victim’s mobile device providing the threat actors full remote control and observation of the device and
Countries
FranceObservations came to light in September 2020 in France when a fake website mimicking legitimate services surfaced with a C2 domain identified as hxxp://tweensangoma.servebbs[.]com:22222.RussiaResearchers have observed the locker demand higher ransoms for victims in the US than in Europe or Russia.
Industries
GovernmentAndroid-specific malware, especially if deployed alongside a “crypter,” is one of many credible threats to commercial and government organizations that utilize devices with the Android operating system.HealthcareTargets ranging from everyday citizens, government officials, healthcare workers, lawyers, etc.