DarkOwl Roundup Profiles Emerging Ransomware Groups Operating on the Darknet
Summary
DarkOwl profiles emerging ransomware groups, describing their darknet activity, claimed affiliations, apparent targets, and public victim-shaming or data-leak practices.
Key points
- DarkOwl says ransomware-as-a-service groups use darknet services to coordinate, recruit affiliates, negotiate with victims, and publish or sell allegedly stolen data.
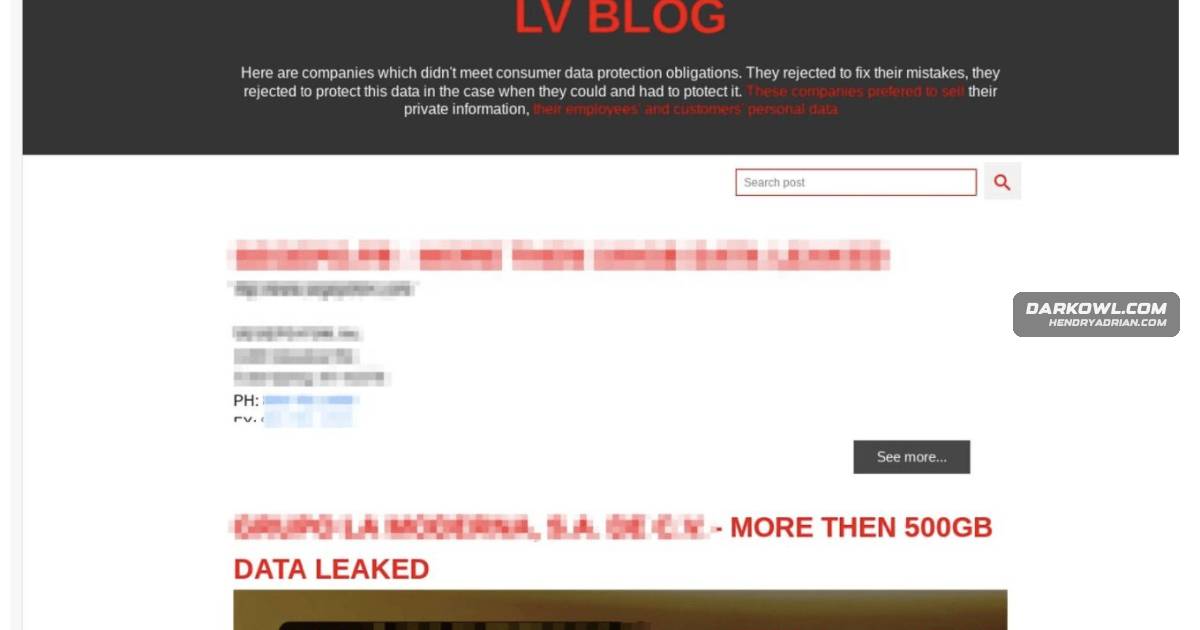
- LV ransomware appears to use customized REvil/Sodinokibi binaries and has made announcements suggesting a focus on France.
- Xing is described as self-claimed Chinese-language ransomware and assessed as an Avaddon/MountLocker affiliate; its Tor service listed pipeline-services company Linestar Integrity Services.
- LockBit 2.0 relaunched with a partner recruitment pitch and claimed encryption-speed and self-spreading capabilities.
- Lorenz launched in April 2021; Dutch researchers at Tesorion released a decrypter in late June after reverse-engineering the malware.
- Hive began leaking victim data in June, including encryption and planned disclosure dates; the article says it was linked to a mid-June breach at Altus Group.
- Prometheus's claimed REvil association was removed from its service; open-source reporting cited possible links to Thanos. Vice Society's possible Hello Kitty connection is based on reported Linux-encryption technique similarities.
Article Details
- Event Type
- DarkOwl's roundup of emerging and active ransomware-as-a-service groups observed on darknet services.
- Impact
- The groups described conduct ransomware attacks, publicly disclose or threaten to disclose victim data, and seek ransom payments. Reported victims include Linestar Integrity Services, Altus Group, and multiple school districts; the article also notes apparent targeting of victims in France by LV.
Threat Actors
Arvin ClubGroup operating Tor services and a Telegram channel; the article describes its activity around data leaks and ransomware-group links.DarkSideRansomware group associated in the article with the attack on Colonial Pipeline.GriefRansomware group that publicly shames victims and uses financial-impact messaging.HiveRansomware group that began appearing in June and published victim data, including information related to a breach at Altus Group.Lockbit 2.0Ransomware operation described as rebooting the original group's activities and recruiting partners for an affiliate model.LorenzRansomware group described as operating since April 2021 and publishing victim information.LVRansomware group whose operators appear to use a personalized version of REvil/Sodinokibi source binaries; reported targeting victims in France.PrometheusRansomware group that claimed to be a group of REvil; the article says this association was later removed from its domain.REvilRansomware group whose source binaries were reportedly adapted by LV; Prometheus also claimed an association with REvil.Vice SocietyRansomware group with known school-district victims; assessed as a possible spin-off of the Hello Kitty ransomware variant.XingSelf-claimed Chinese-language ransomware operation assessed by the article to be an affiliate of the Avaddon/MountLocker ransomware family.
Malware
AvaddonXing is a self-claimed Chinese-language ransomware assessed to be an affiliate of the Avaddon/MountLocker ransomware family.Grief ransomwareThe Grief ransomware has marketing and branding down to it a tee, with its “Grief came to …” theme for its public shaming of victims.HelloKittyVice Society is assessed to be a possible spin-off of the Hello Kitty ransomware variant based on similarities in the techniques used for Linux system encryption.Hive ransomwareThe Hive ransomware group appeared in June with little self-proclamation but instead jumping right into leaking victim data.LorenzLorenz / SZ40LV ransomwareThreat actors behind the LV ransomware appear to have deployed their own personalized version of the 2.03 source binaries developed by the infamous REvil/Sodinokibi ransomware group.MountLockerXing is a self-claimed Chinese-language ransomware assessed to be an affiliate of the Avaddon/MountLocker ransomware family.Prometheus ransomware variantAccording to open-source reporting, the Prometheus ransomware variant has possible associations with the Thanos ransomware variant.REvilThreat actors behind the LV ransomware appear to have deployed their own personalized version of the 2.03 source binaries developed by the infamous REvil/Sodinokibi ransomware group.ThanosAccording to open-source reporting, the Prometheus ransomware variant has possible associations with the Thanos ransomware variant.
Vendors
Tools
Countries
FranceThe LV ransomware group appears to be targeting victims in France as indicated by their latest public announcements.Iranre-shares of other data leaks (including the information stolen from the Ministry of Intelligence of Iran), press reports of significant cyber attacks, and onion service URLs for popular ransomware groups.