
Tor’s v2 Onion Address Deprecation Leaves Legacy Services Accessible to Some Clients
Summary
DarkOwl reports that Tor’s move to disable v2 onion services has not made them inaccessible to all legacy clients. Its collection found 62% of observed active onion services still used v2 addresses.
Key points
- Tor Project phased out v2 onion services in 2021, ending support through client and network changes.
- DarkOwl says legacy browser executables could still access some deprecated v2 services after newer Tor Browser versions disabled them.
- In a six-week snapshot, DarkOwl observed an average of 104,095 active onion services; 62% used v2 addresses and 38% used v3.
- DarkOwl cautions that its collection figures are not a count of all active Tor onion services.
- DarkOwl observed 2,963 new v3 addresses in the last two weeks of July 2021, following removal of the option to create new v2 services.
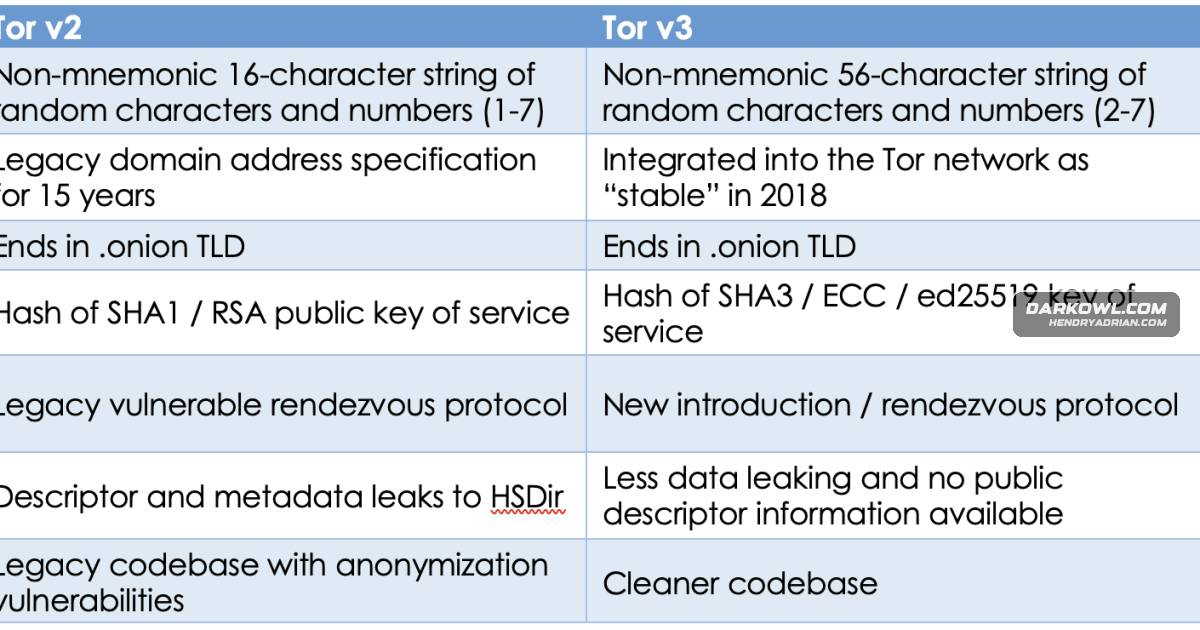
- The article describes v3 addressing as using stronger cryptography than v2, while noting that Tor's transition and relay updates affected when v2 services became unavailable.
Article Details
- Event Type
- Tor Project’s deprecation and disabling of legacy v2 onion-service addressing, and the resulting changes in Tor service availability.
- Impact
- DarkOwl estimates that known onion services decreased by 62% after v2 support ended. DarkOwl also reports that some legacy v2 services remained accessible with older browser clients. The article discusses security differences between v2 and v3 addressing and reports prior v3 service outages; it does not identify a specific compromise or victim organization.
People
Products
TorDarkOwl has unprecedented coverage of data from prominent darknets including Tor (or The Onion Router), which is widely considered to be the most well-known and popular darknet.Tor BrowserWithin that month, Tor Project did update the Tor Browser to version 10.5.10 disabling v2 and rendering v2 onion services unavailable.