DarkOwl Reports LAPSUS$ Activity Across Brazilian and Portuguese Organizations
Summary
DarkOwl describes LAPSUS$ activity against organizations in Brazil and Portugal, including alleged data theft and service disruptions. The group’s responsibility for some incidents, including attacks affecting Vodafone and Cofina, remained unconfirmed.
Key points
- DarkOwl reported increased LAPSUS$ activity from December 2021, with targets including Portuguese-speaking organizations in Brazil and Portugal.
- Brazil’s Ministry of Health acknowledged a temporary service outage after LAPSUS$ claimed access and data deletion; the government did not confirm the group was responsible.
- LAPSUS$ posted screenshots it said showed access to Claro and Embratel systems, including more than 1,500 virtual machines; DarkOwl said it was still investigating how access was gained.
- The group claimed responsibility for attacks involving Portuguese media company Impresa, including SMS phishing and activity on a verified Twitter account.
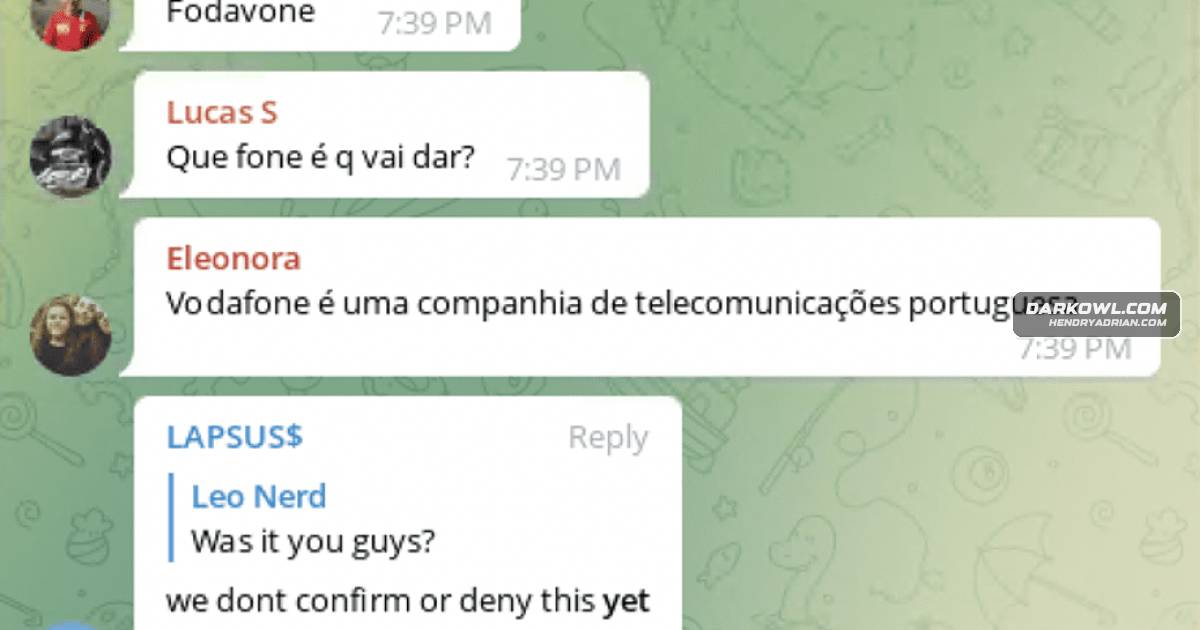
- LAPSUS$ did not confirm or deny responsibility for Vodafone Portugal’s disruption; the company said no subscriber or sensitive customer data was accessed or stolen.
- DarkOwl said LAPSUS$ had previously claimed stolen EA/FIFA data and later leaked it after an alleged $28 million extortion attempt failed.
Article Details
- Event Type
- Cybercriminal activity involving data theft, extortion, service disruption, defacement, and phishing attributed or linked to LAPSUS$ across multiple organizations.
- Impact
- Reported impacts included disruption to Vodafone Portugal voice, SMS, and television services; deletion of Brazil’s Ministry of Health vaccination-record database and temporary web-service outage; alleged theft of large volumes of corporate information and customer SIM details from Claro and Embratel; defacement and phishing affecting Impresa/Expresso; and a reported partial interruption at Localiza. Some incidents were not definitively attributed to LAPSUS$, and reports stated there was no evidence of customer data theft in the Vodafone Portugal, Ministry of Health, and Localiza incidents.
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelThe group claimed to have copied internal data and reported stolen data in several incidents; the article does not establish that data was exfiltrated in every case.T1490 · Inhibit System RecoveryThe alleged attack on Brazil’s Ministry of Health reportedly deleted the COVID vaccination-record database.T1491.002 · External DefacementThe group defaced websites and social-media accounts, including Impresa’s Twitter account.T1565.002 · Transmitted Data ManipulationThe Localiza incident was described as an apparent DNS spoofing attack that redirected website visitors.T1566.001 · Spearphishing AttachmentLAPSUS$ members reportedly sent phishing SMS texts to Expresso subscribers.
People
Threat Actors
Vendors
BlackBerryAccording to open-source reporting, analysts with Blackberry’s Research and Intelligence Division confirmed Cyberjagu is some sort of “intermediary” for the cybercriminal group behind the EA/FIFA attack.DarkOwlIn December 2021, DarkOwl witnessed increased activity on the darknet regarding the cybercriminal gang known as LAPSUS$.
Products
AWSThe group appears to have preference for attacking Portuguese-speaking organizations using data extortion-style campaigns and leverage compromised AWS servers where possible.DoxbinDrama Between Doxbin & LAPSUS$FrostBiteEnglish language detailing to EA that they found a Remote Code Execution (RCE) vulnerability in the “frostbite engine” and they had no intention to target console users.GitLabinformation and SIM details for Claro customers across mass data storage systems such as: AWS, 2x Gitlab, SVN, x5 vCenter (MCK, CPQCLOUD, EOS, ODIN), Dell EMC storage, and Telecom/SS7.RaidForumsdetected previous activity from the LAPSUS$ on the deep web and darknet including posts in July 2021 on RaidForums and other darknet forums claiming they had compromised networks and stolen data for the FIFA soccerSVNinformation and SIM details for Claro customers across mass data storage systems such as: AWS, 2x Gitlab, SVN, x5 vCenter (MCK, CPQCLOUD, EOS, ODIN), Dell EMC storage, and Telecom/SS7.VMware vCenter Serverand SIM details for Claro customers across mass data storage systems such as: AWS, 2x Gitlab, SVN, x5 vCenter (MCK, CPQCLOUD, EOS, ODIN), Dell EMC storage, and Telecom/SS7.
Tools
Countries
BrazilThe cyberattack, allegedly “ransomware in nature” compromised Brazil’s Ministry of Health COVID vaccination records database, deleting the entire database contents, and defacing its website with the following message:PortugalVodafone Telecommunications in PortugalSpainThe January dox suggested might be in the process of relocating to Spain with his family.United Kingdomwe discovered São Paulo, Brazil did not have weather conditions at that date/timestamp, but London, United Kingdom experienced similar weather patterns.