RaidForums’ Apparent Seizure Spurs Replacement Forums and Continued Data-Leak Activity
Summary
DarkOwl reports that RaidForums went inactive amid claims its domain was seized, while replacement forums emerged. BreachedForums reportedly attracted thousands of members and distributed large volumes of claimed leaked data.
Key points
- RaidForums users reportedly lost access on February 25, 2022; a moderator claimed the domain had been seized and was operating as a law-enforcement honeypot, but the article says authorities did not confirm this.
- RaidForums’ domain remained online but inactive, and its registration information reportedly changed on February 25.
- RaidForums 2 emerged as a separate forum; its administrator reportedly disclaimed ties to the original site.
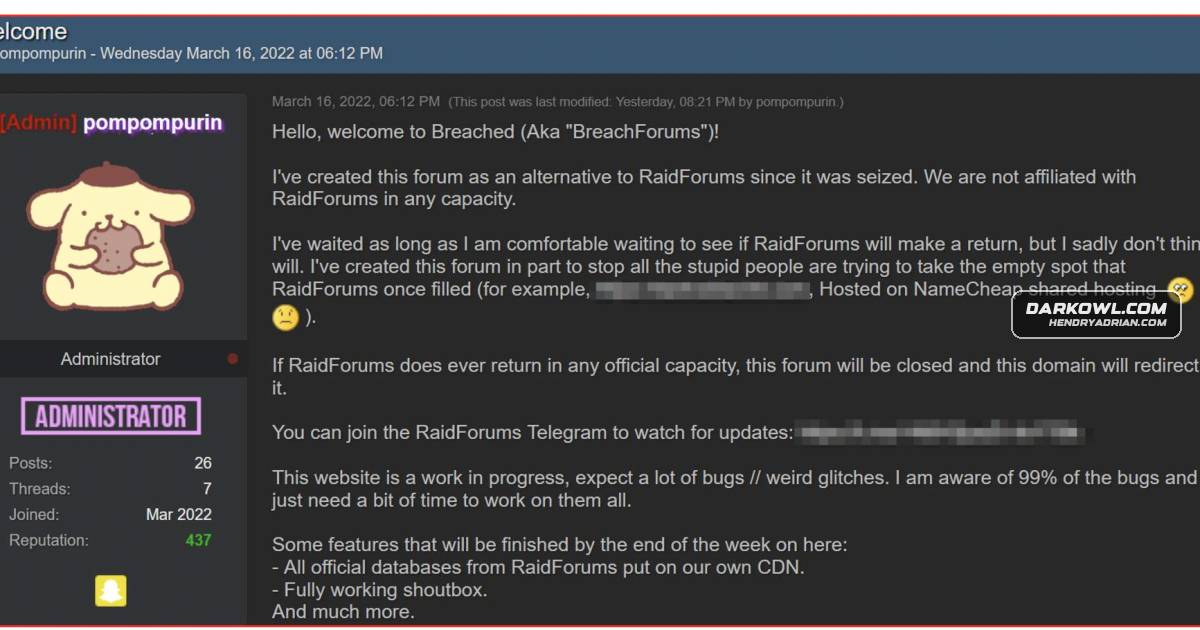
- BreachedForums opened for registration on breached[.]co on March 16, 2022, and reportedly gained 3,293 members, 13,707 posts, and 1,939 threads in less than three weeks.
- DarkOwl estimates BreachedForums hosted more than 80 official datasets containing over one billion records and that members distributed more than 700 other data archives.
- The article describes forum posts involving claimed leaks related to the Ukraine conflict and alleged targeting of government and military organizations; these claims are attributed to forum users.
- BreachedForums reportedly faced downtime after its domain was reported for illicit content, prompting its administrator to set up a Tor service and alternate mirrors.
Article Details
- Event Type
- RaidForums domain seizure and shutdown, followed by the emergence of replacement forums
- Impact
- Users reportedly lost the ability to log into RaidForums after its domain was said to have been seized. A moderator alleged the site had become a law-enforcement honeypot and phishing operation, but the article says the seizure was not officially confirmed. RaidForums users subsequently established replacement forums, where members continued distributing sensitive data leaks.
MITRE ATT&CK
Threat Actors
AgainstTheWestA RaidForums 2 member who reportedly shared leaks obtained through campaigns against Russian and Chinese targets.AnonymousThe article refers to Anonymous’s #opRussia cyber campaign in connection with sensitive data shared on BreachedForums.CarzitaA RaidForums user who reportedly claimed to be actively targeting Ukrainian government websites.LAPSUS$The article identifies LAPSUS$ as the group associated with source-code leaks discussed on RaidForums 2.NetSecA self-described cybersecurity hacktivist who claimed to target U.S. government and military networks and to be working with Russian individuals on a zero-day.PompompurinA RaidForums user reportedly DDoS-attacked the domain after its moderator said it had been seized, and later established BreachedForums.
Vendors
Products
Countries
CanadaAccording to their surface web blog, pompur[.]in, pompompurin, resides in Canada.RussiaMoot, another staff administrator of RaidForums posted in a thread titled, “RAIDFORUMS SANCTIONS ON RUSSIA,” stating that anyone connecting to the forum from a Russian IP address would be banned.SwitzerlandNetSec is a self-proclaimed cybersecurity hacktivist reportedly in Switzerland with possible US citizenship, but not directly working with a government or for a company.UkraineDuring the weeks leading up to the invasion in Ukraine, various threat actors shared sensitive information pertaining to the Ukrainian cyberattacks from January and February.United KingdomWhile Omnipotent states the United Kingdom as their location on his Github profile, their exact location is unknown.
Industries
DefenseSpecial Operations Command (soc[.]mil), the Defense Technical Information Center for the US Government (dtic[.]mil) and Lockheed Martin defense contractor employees.GovernmentThe website had experienced domain issues in the fall of 2021, when the Brazilian government attempted to have NameSilo – the domain’s registrar – shutdown the forum.