Ransomware Activity Rebounds After Ukraine Invasion, DarkOwl Reports
Summary
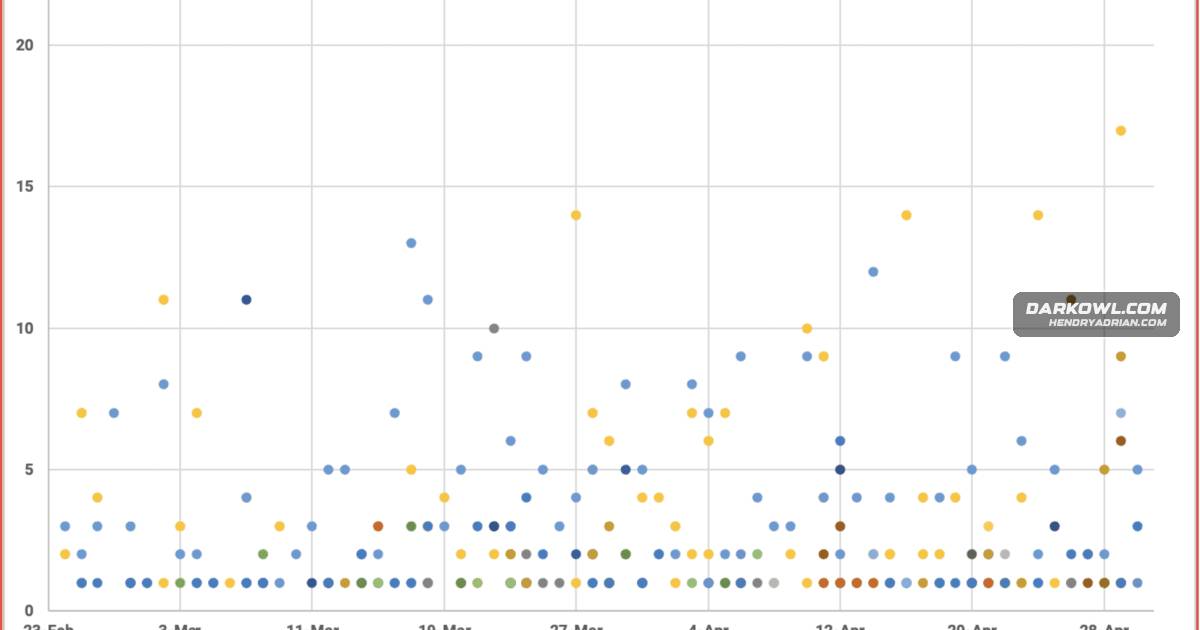
DarkOwl reports 813 ransomware victim announcements across 25 tracked groups since February 24, 2022, with activity rebounding in April and claims involving critical infrastructure. It also describes new groups and REvil’s brief return.
Key points
- DarkOwl counted 813 victim announcements across 25 active ransomware groups since February 24; LockBit 2 had the most, with 280.
- After a slowdown in CONTI victim announcements in mid-March, CONTI, LockBit 2, and CL0P announced dozens of victims during April.
- Reported targets included critical-infrastructure suppliers, manufacturers, and construction companies. The article describes incidents involving MACK Defense, TUI Group, and Nordex.
- DarkOwl says CONTI’s March attack on Nordex shut down more than 5,000 wind turbines; CONTI later published 145 GB of data it said was related to the company.
- REvil’s Tor service briefly returned on April 20 with five victim listings and an affiliate recruitment message, then became inaccessible. The group’s intentions were unclear.
- Blackbasta and Onyx appeared with new victim listings; DarkOwl also observed increased activity by HiveLeak and AlphaV.
- The article says pro-Ukrainian group nb65 claimed to use leaked CONTI ransomware against Russian entities; it also describes data leaks and threats involving ransomware groups and researchers.
Article Details
- Publisher
- DarkOwl
- Report Period
- 2022-02-24 to 2022-04-30
- Scope
- Ransomware-as-a-service activity and victim announcements tracked since the invasion of Ukraine
- Sample Size
- 25 active ransomware groups tracked by DarkOwl
- Key Statistics
- DarkOwl counted 813 victims announced by tracked ransomware groups since 2022-02-24, an average of 11.8 victims per day across the groups.
- Lockbit 2 announced 280 victims since 2022-02-24, an average of 4.5 victims per day.
- CONTI reportedly leaked 145 GB of data related to Nordex, archived in 82 compressed files.
- The article reports that Nordex shut down more than 5,000 wind turbines in Germany following a cyber incident.
- Blackbasta announced 11 victims on 2022-04-26; Onyx added 7 victims at the end of April.
Threat Actors
AlphaVRansomware group whose activity reportedly increased during the period.BlackBastaNew ransomware group reported to have appeared online and announced 11 victims on April 26.Cl0pRansomware group that announced victims, including announcements clustered around weekends.ContiRansomware group that announced victims and was reported to have encrypted MACK Defense and Nordex; its leaked source code was reportedly used by nb65.HiveLeakRansomware group whose activity reportedly increased during the period.Lockbit 2Ransomware group reported to have announced 280 victims since 2022-02-24.Network Battalion (nb65)Pro-Ukrainian cyber threat cell, also called nb65, reported to have conducted ransomware attacks against Russian entities using a variation of leaked CONTI source code.OnyxRansomware group reported to have started leaking victim data and added seven victims at the end of April.REvilRansomware operation whose Tor service reportedly reappeared on April 20 and announced five victims, then became inaccessible by the end of the month.SnatchRansomware group reported to have leaked more than a gigabyte of data from TUI Group.StormousRansomware group that announced a compromise of Ukraine’s Ministry of Foreign Affairs and stated it would not attack Ukraine.Vice SocietyRansomware group reported to have announced 20 victims in the last 10 days of April.x001xsRansomware group that reportedly had not announced victims since late January and whose Tor service redirected to a darknet credit-card provider.
Malware
BazarLoaderFrom an operations perspective, we also learned the critical roles Bazarloader Botnet, Cobalt Strike, and Trickbot played in the long-term success of CONTI’s empire.BlackBastaA new RaaS group called Blackbasta appeared online and announced 11 new victims on the 26th of April.ContiA security researcher leaked critical operational data, personally identifying information for threat actors, and sensitive private chats between members of the CONTI RaaS group.OnyxAnother new group, Onyx ransomware started leaking their victim data on a Tor service titled, “Onyx News” with 7 new victims added at the end of April.REvilThe Resurrection of REvilTrickBotFrom an operations perspective, we also learned the critical roles Bazarloader Botnet, Cobalt Strike, and Trickbot played in the long-term success of CONTI’s empire.
Tools
Countries
CanadaRansomware groups have announced at least half a dozen victims across electrical, water, or natural gas-affiliated suppliers the US, Canada, and Europe in the last 10 days.GermanyThe Nordex cybersecurity incident was likely a critical infrastructure retaliation attack for Germany’s support of Ukraine.IndiaThe new REvil Tor service boasts an odd-mix of victims, including an oil and gas company in India, asphalt production company and a corporate signage company.Russiaaffiliate programs impacted by their partners having to choose between their nationalistic alliances with Russia or Ukraine.UkraineIn the days immediately following the invasion of Ukraine, the ransomware-as-a-service (RaaS) industry on the darknet experienced several high-profile interruptions with many popular RaaS affiliate programs impacted by
Industries
ConstructionDarkOwl also observed an increase in manufacturing and construction-related companies with downstream victims including international lumber and steel processing companies mentioned quite frequently.Critical infrastructureCritical Infrastructure TargetedGovernmentinclude several US and NATO-based critical infrastructure organizations and suppliers including local government municipalities, electrical and alternative power providers, water, telecommunications, andManufacturingDarkOwl also observed an increase in manufacturing and construction-related companies with downstream victims including international lumber and steel processing companies mentioned quite frequently.Oil and gasThe new REvil Tor service boasts an odd-mix of victims, including an oil and gas company in India, asphalt production company and a corporate signage company.Telecommunicationsincluding local government municipalities, electrical and alternative power providers, water, telecommunications, and transportation suppliers.Transportationgovernment municipalities, electrical and alternative power providers, water, telecommunications, and transportation suppliers.TravelMeanwhile, Snatch leaked over a gigabyte of data from a popular European travel website, TUI Group.waterand suppliers including local government municipalities, electrical and alternative power providers, water, telecommunications, and transportation suppliers.