Cyber Insurance Cannot Replace Strong Cybersecurity Defenses
Summary
The article reviews common cyber insurance exclusions, darknet indicators of insider and prior-breach risks, and attacks targeting insurance-related businesses. It argues that insurance should supplement—not replace—strong security practices.
Key points
- The article says policies may exclude losses tied to human error, insider attacks, known unremediated vulnerabilities, prior breaches, and security improvements; coverage depends on policy terms.
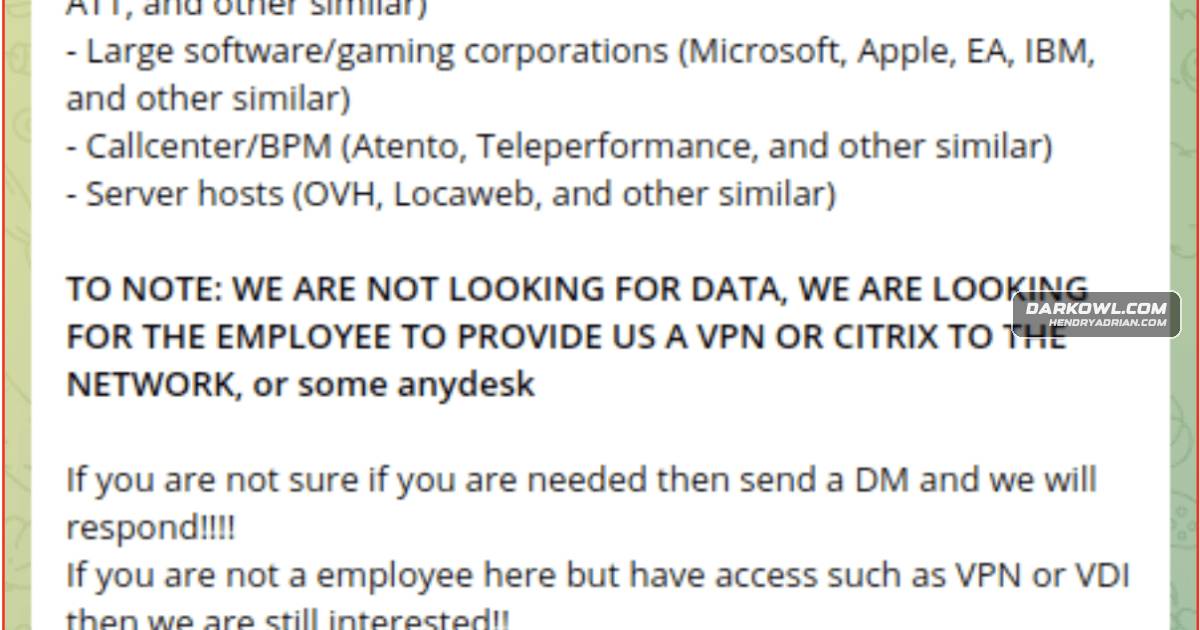
- Darknet posts have advertised payments to employees with access, including telecom insiders sought for SIM-swapping and LAPSUS$ recruitment of workers with remote network access.
- DarkOwl describes monitoring credentials, prior-breach claims, and leaked data as ways insurers could assess exposure, while noting that darknet claims are not proof of a breach.
- The article cites a threat actor's allegation of repeated compromise and data theft at an unnamed organization; the claim is attributed to the actor, not independently confirmed in the article.
- It reports that ransomware groups have targeted insurance agents, affiliated businesses, brokers, underwriting services, and legal firms, and cites LockBit's public claims involving insurance-related disputes.
Article Details
- Topic
- Cyber insurance exclusions, insider threats, and darknet monitoring
Threat Actors
Vendors
Products
AnyDeskThey specifically asked for the employees to have remote access via VPN, Citrix or anydesk applications.CitrixThey specifically asked for the employees to have remote access via VPN, Citrix or anydesk applications.DarkOwl VisionEvidence of a policy holder’s prior breaches, organization credential exposures, and and the risk of insider attacks can be evaluated using a robust darknet database, like DarkOwl Vision.HackerOneIn early July, in an unusual insider-threat example, a HackerOne employee exploited their internal access to bug reports to duplicate the reports and gain financial payment for the bug bounty program.TelegramOn Telegram, LAPSUS$ openly recruited insiders to help with their attacks calling for employees at telecommunications, software and gaming corporations, call centers, and web/server hosting organizations.
Countries
RussiaGiven we are in a time of the first ever global cyberwar as the result of Russia’s invasion of Ukraine and CISA has advised an increased security posture for all critical industry sectors, CISOs and securityUkraineGiven we are in a time of the first ever global cyberwar as the result of Russia’s invasion of Ukraine and CISA has advised an increased security posture for all critical industry sectors, CISOs and security
Industries
GamingOn Telegram, LAPSUS$ openly recruited insiders to help with their attacks calling for employees at telecommunications, software and gaming corporations, call centers, and web/server hosting organizations.GovernmentGovernment, healthcare, and Insurance carriers are also targeted for insider recruitment in a recent deep web post captured by DarkOwl (below).HealthcareGovernment, healthcare, and Insurance carriers are also targeted for insider recruitment in a recent deep web post captured by DarkOwl (below).InsuranceEarlier this summer we researched the cyber insurance industry and the darknet and reviewed basic policies, first- and third-party coverage and looked at a sample of the type of data insurers might want to monitor theSoftwareOn Telegram, LAPSUS$ openly recruited insiders to help with their attacks calling for employees at telecommunications, software and gaming corporations, call centers, and web/server hosting organizations.TelecommunicationsOn Telegram, LAPSUS$ openly recruited insiders to help with their attacks calling for employees at telecommunications, software and gaming corporations, call centers, and web/server hosting organizations.