
February Threat Intelligence Roundup Highlights Malware, Ransomware and Supplier Portal Flaw
Summary
A February roundup covers malware and phishing campaigns, GuLoader and MortalKombat activity, the Hive ransomware disruption, and a researcher-reported flaw in Toyota’s supplier portal. It also mentions a non-security AI chatbot story.
Key points
- Scammers used The Last of Us-themed downloads and activation-code offers to distribute malware and steal financial or account data.
- Researchers reported more than 50 malicious apps using ChatGPT branding; one campaign used a fake app site to spread Redline stealer.
- Trellix reported GuLoader campaigns targeting the U.S. and South Korea, using NSIS executables embedded in ZIP or ISO files.
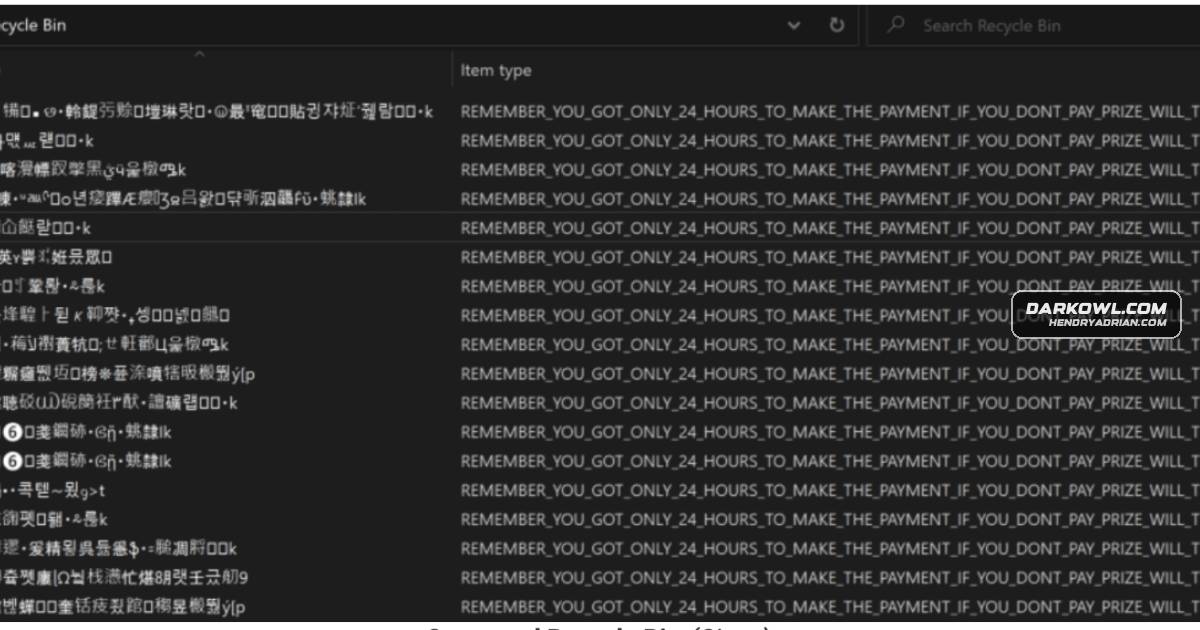
- MortalKombat ransomware, identified in January 2023, was reported alongside the Laplas cryptocurrency clipper, with victims reported in four countries.
- The U.S. Department of Justice said the FBI had accessed Hive’s network since July 2022 and provided victims with decryption keys; law enforcement also took control of Hive infrastructure.
- A researcher reported accessing Toyota’s supplier portal through a backdoor and an API information-disclosure flaw, potentially enabling access to privileged data.
Article Details
- Event Type
- Monthly roundup of cybersecurity news covering malware and phishing campaigns, ransomware activity and law-enforcement disruption, and a security breach affecting a supplier portal.
- Impact
- Reported incidents involved theft of banking and other financial data, delivery of malware, ransomware and cryptocurrency-hijacking activity, and potential exposure of privileged information for Toyota supplier-portal users. The FBI said it had provided Hive ransomware victims with decryption keys and, with other law-enforcement agencies, infiltrated and controlled servers and sites used by Hive.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | chat-gpt-pc[.]online | Domain described as a guise used to infect visitors with Redline stealer. |
People
Threat Actors
Malware
GuLoader3. GuLoader Malware Using Malicious NSIS Executables to Target E-Commerce Industry – The Hacker NewsLAPLASThe MortalKombat ransomware is being seen used in conjunction with Laplas clipper – a cryptocurrency hijacker – in recent attacks for financial fraud.MortalKombat4. New ‘MortalKombat’ Ransomware Targets systems in the U.S. and Abroad – Bleeping ComputerRedLine StealerOne domain, “chat-gpt-pc.online” was a guise to infect visitors with Redline stealer.XoristMortalKombat ransomware, first found in January of 2023, is a variant of Xorist ransomware based on the commodity family.
Vendors
Products
Bing ChatbotIn an article written for the New York Times, security researcher Kevin Roose breaks down their 2-hour long discussion with Microsoft’s new chatbot for OpenAI-powered Bing Chatbot.ChatGPT2. Hackers Use Fake ChatGPT Apps to Push Windows, Android Malware – Bleeping ComputerGlobal Supplier Preparation Information Management System (GSPIMS)A security researcher alerted Toyota that they were able to breach Toyota’s Global Supplier Preparation Information Management System (GSPIMS) – the web application used to manage their global supply chain.
Countries
PhilippinesThere are reported to be victims in the United States, United Kingdom, the Philippines, and Turkey.South KoreaAccording to Trellix the US and South Korea are targets of a GuLoader malware campaign.TurkeyThere are reported to be victims in the United States, United Kingdom, the Philippines, and Turkey.United KingdomThere are reported to be victims in the United States, United Kingdom, the Philippines, and Turkey.