
Krybit Claims Ransomware Attack on German Healthcare Organization Diakoniewerk Apolda
Summary
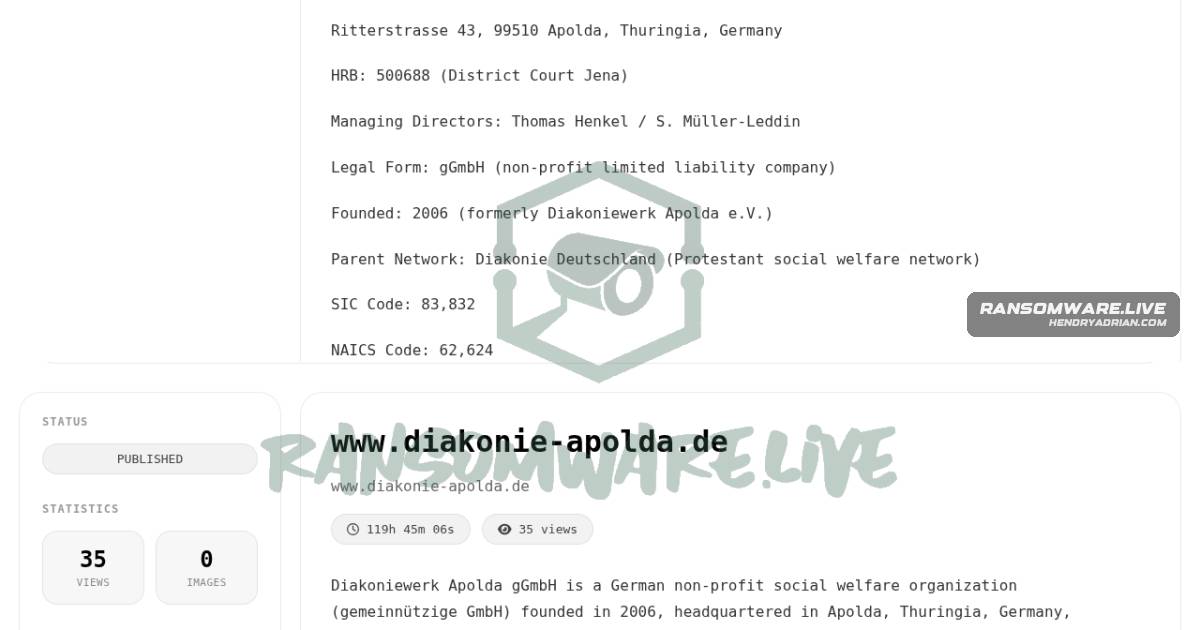
Ransomware group krybit claims it compromised data linked to Diakoniewerk Apolda gGmbH in Germany. The monitored claim was published September 17, 2026; its accuracy is unconfirmed.
Key points
- The claim names Diakoniewerk Apolda gGmbH, associated with diakonie-apolda[.]de, as the victim and identifies healthcare as its sector.
- The ransomware group krybit is named as the actor; the post attributes the claim to the group's leak site.
- The monitoring record lists September 17, 2026, as the discovery and publication date.
- The publisher says it cannot confirm the claim's accuracy. No official statement or independent confirmation is provided.
Article Details
- Victim
- Diakoniewerk Apolda gGmbH
- Victim Domain
- www.diakonie-apolda.de
- Claim Date
- 2026-09-17
- Encryption Status
- Unknown
- Exfiltration Status
- Unknown; the source reports an unverified claim of compromised data but does not confirm exfiltration.
- Ransom Demand
- Unknown
- Leak Status
- The claim was published on the actor's blog; no data publication is reported.