
May Threat Intelligence Roundup Covers Skimmers, Malware and Cyber Espionage
Summary
A May roundup highlights reports on MageCart checkout skimmers, ViperSoftX targeting password managers, the Merdoor backdoor, alleged Iranian-linked BouldSpy spyware, Bad Magic activity and malicious drivers used in BlackCat attacks.
Key points
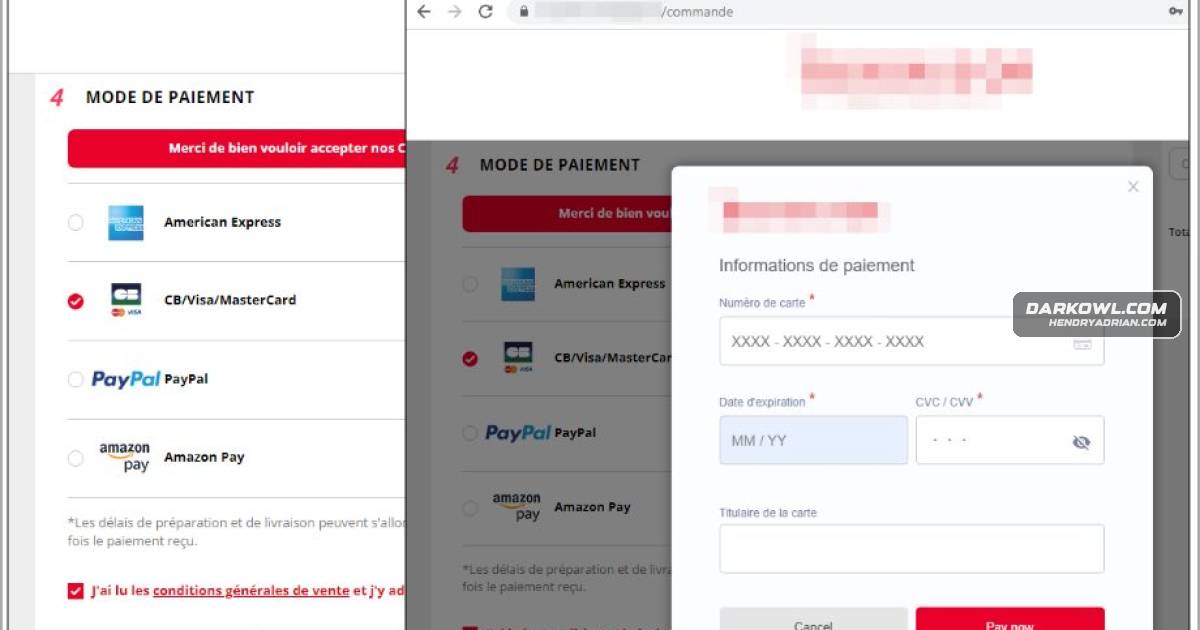
- MageCart operators reportedly use realistic, overlaid checkout forms to steal payment-card information.
- A newer ViperSoftX version reportedly targets password managers and uses the VenomSoftX browser extension, with added evasion features.
- Symantec observed LanceFly using the Merdoor backdoor against organizations in South and Southeast Asia since 2018; initial access methods remain unclear.
- Lookout attributed BouldSpy to Iran's Law Enforcement Command with moderate confidence; the Android spyware reportedly targets minority groups, and physical access appears to be the intrusion vector.
- Bad Magic, also known as Red Stinger, has been linked to activity in the Russo-Ukrainian region and activity dating to 2016.
- Trend Micro reported that the ALPHV/BlackCat ransomware group used signed malicious Windows kernel drivers known as POORTRY to evade security software.
Article Details
- Event Type
- Monthly threat intelligence roundup summarizing reports on MageCart payment-card skimming, ViperSoftX information theft, LanceFly and Merdoor activity, alleged BouldSpy spyware use, Bad Magic cyber espionage, and ALPHV/BlackCat ransomware attacks.
- Impact
- The cited reports describe theft of payment-card information and passwords, persistent backdoor access and espionage, alleged surveillance of minority groups, and ransomware activity. The roundup reports targeting across multiple countries and organizations, but provides no aggregate impact figures or confirmed remediation status.
MITRE ATT&CK
T1036 · MasqueradingBouldSpy reportedly creates malicious applications masquerading as harmless apps.T1056.003 · Web Portal CaptureMageCart skimmers reportedly superimpose fraudulent checkout forms on legitimate store pages to capture payment-card information.T1059.001 · PowerShellViperSoftX reportedly uses shellcode and byte mapping for code encryption.T1110.001 · Password GuessingSymantec observed LanceFly using SSH credential brute forcing.T1200 · Hardware AdditionsBouldSpy's intrusion vector reportedly appears to involve physical access to devices.T1547 · Boot or Logon Autostart ExecutionMerdoor is described as persistent and able to remain on devices across reboots; the specific persistence mechanism is not stated.T1562.001 · Disable or Modify ToolsALPHV/BlackCat reportedly uses malicious signed Windows kernel drivers to evade security software.T1566 · PhishingSymantec observed LanceFly using phishing emails as an initial-access method.T1574.002 · DLL Side-LoadingMerdoor is reportedly deployed through DLL side-loading into legitimate Windows processes.
Threat Actors
ALPHVRansomware group reported to use malicious signed Windows kernel drivers in attacks.Bad MagicThreat actor linked in the roundup to cyberattacks targeting companies in the Russo-Ukrainian area and activity dating to May 2016.LanceFlyNamed APT group reported to use Merdoor in attacks targeting organizations in South and Southeast Asia since 2018.Law Enforcement Command of the Islamic Republic of IranLookout attributed BouldSpy to this organization with moderate confidence; the attribution is presented as alleged.
Malware
BouldSpy4. BouldSpy Android Spyware: Iranian Government’s Alleged Tool for Spying on Minority Groups – The Hacker NewsCryDroidIt utilizes an element from the open source CryDroid, which could indicate the malware is still being developed or being used as a false flag.Merdoor3. Stealthy MerDoor malware uncovered after five years of attacks – BleepingComputerPOORTRY(aka BlackCat) has been observed employing improved signed malicious Windows kernel drivers, known as “POORTRY,” in order to not be detected while conducting cyberattacks by security software.VenomSoftXThe malware installs targets Chrome, Brave, Edge, and Opera browsers with a malicious extension called VenomSoftX.ViperSoftX2. ViperSoftX info-stealing malware now targets password managers – BleepingComputer
Vendors
CybleWith a moderate confidence level, Lookout has attributed a malware called BouldSpy (names DAAM by Cyble) to the Law Enforcement Command of the Islamic Republic of Iran.LookoutWith a moderate confidence level, Lookout has attributed a malware called BouldSpy (names DAAM by Cyble) to the Law Enforcement Command of the Islamic Republic of Iran.MalwarebytesA report by Malwarebytes highlights how MageCart skimmers are using real online stores checkout pages and hijacking them with their own fraudulent but realistic-looking forms to steal credit card information.SymantecMethods for initial access are unclear, but Symantec has observed the group using methods such as phishing emails, SSH credential brute forcing, and others.Trend MicroAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.
Products
1PasswordThe most recent version of the ViperSoftX infostealer has been observed targeting password managers including KneePass and 1Password.Android4. BouldSpy Android Spyware: Iranian Government’s Alleged Tool for Spying on Minority Groups – The Hacker NewsBraveThe malware installs targets Chrome, Brave, Edge, and Opera browsers with a malicious extension called VenomSoftX.EdgeThe malware installs targets Chrome, Brave, Edge, and Opera browsers with a malicious extension called VenomSoftX.Google ChromeThe malware installs targets Chrome, Brave, Edge, and Opera browsers with a malicious extension called VenomSoftX.KneePassThe most recent version of the ViperSoftX infostealer has been observed targeting password managers including KneePass and 1Password.Microsoft WindowsMerdoor is put into “’perfhost.exe’ or ‘svchost.exe” which are both real Windows processes through DLL side-loading.OperaThe malware installs targets Chrome, Brave, Edge, and Opera browsers with a malicious extension called VenomSoftX.
Countries
AustraliaAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.BrazilAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.FranceAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.IndiaAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.IranWith a moderate confidence level, Lookout has attributed a malware called BouldSpy (names DAAM by Cyble) to the Law Enforcement Command of the Islamic Republic of Iran.ItalyAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.JapanAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.MalaysiaAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.TaiwanAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.United StatesAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.
Industries
ConsumerAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.EnterpriseAccording to Trend Micro, the malware has targeted the consumer and enterprise sectors in the U.S., Italy, Brazil, India, Australia, Japan, Taiwan, Malaysia, France, and Italy.