DarkOwl’s October Roundup Covers Lazarus Malware, Ransomware and Cyberattacks
Summary
DarkOwl’s October roundup highlights reports on Lazarus’s Lightless Can backdoor, Magecart skimming, ransomware incidents, attacks on Trigona infrastructure, and activity by Predatory Sparrow and KillNet.
Key points
- Lazarus reportedly used fake Meta recruiter profiles and coding challenges to distribute the Lightless Can backdoor to aerospace targets.
- Magecart groups reportedly injected skimming code into websites, targeting food and retail businesses to steal personal and financial information.
- Akira actors reportedly used a contractor’s stolen VPN credentials to access BHI networks and take 767,000 files totaling 690 GB, including customer personal information.
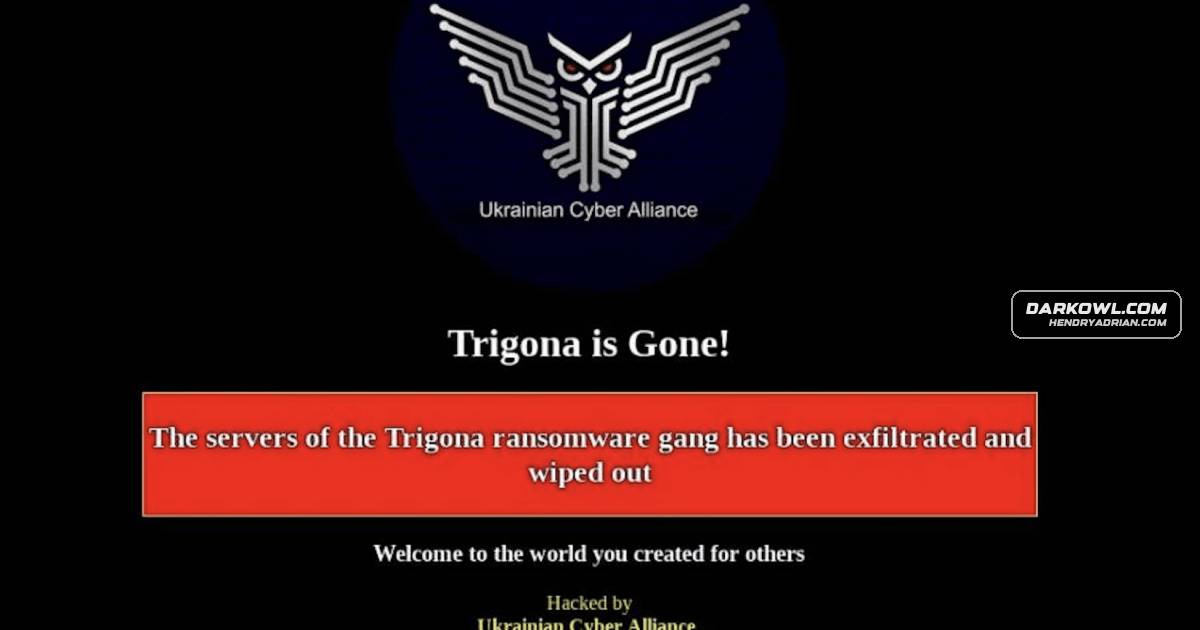
- The Ukrainian Cyber Alliance reportedly exploited CVE-2023-22515 to access Trigona’s Confluence server, collect internal materials, and delete the group’s site.
- Predatory Sparrow reemerged with a Persian-language Telegram post referencing Gaza; a linked Iranian news agency site was reportedly unavailable at the time.
- KillNet claimed a DDoS attack that made the UK Royal Family’s website unavailable for 90 minutes.
- ALPHV and BianLian claimed attacks involving Florida courts and Air Canada, respectively; the roundup presents some stolen-data details as claims or possibilities.
Article Details
- Event Type
- Monthly cybersecurity threat-intelligence roundup covering malware deployment, data theft, ransomware incidents, hacktivism, and DDoS activity.
- Impact
- Reported incidents involved stolen personal and financial information, ransomware-related data theft and exposure, compromised or deleted websites and servers, and a 90-minute outage of the UK Royal Family’s website.
CVE
People
Threat Actors
AkiraRansomware actors reportedly used stolen VPN credentials to access a US energy firm’s internal network and steal data.LazarusThreat actor group reported to have used the Lightless Can backdoor in operations targeting the aerospace industry.MagecartUmbrella term for criminal actor groups reported to use skimmers and custom malware to steal personal and financial information from ecommerce websites.Predatory SparrowIsraeli hacking collective reported to have resumed digital operations and historically targeted Iran.TrigonaRansomware gang whose Confluence server was accessed by the Ukrainian Cyber Alliance.
Malware
Products
Countries
IranThis group, who has historically targeted Iran, posted in Persian in their Telegram channel on Monday, October 16, asking if their followers were “…following what is happening in Gaza.” They also shared a link toIsrael5. Savvy Israel-linked hacking group reemerges amid Gaza fighting – CyberScoopNorth Korea1. North Korea Poses as Meta to Deploy Complex Backdoor at Aerospace Org – Dark ReadingUkraineFueling the fire, Britain’s King Charles had recently condemned the Russian invasion of Ukraine in a public speech, and KillNet attempts to exact retribution on those who speak out against Russian actions.
Industries
Aerospace1. North Korea Poses as Meta to Deploy Complex Backdoor at Aerospace Org – Dark ReadingeCommerceMagecart is an umbrella term; the collective is comprised of several different criminal actor groups who employ skimming and custom malware to steal PII and financial information form ecommerce websites.Energy3. US energy firm shares how Akira ransomware hacked its systems – Bleeping ComputerFoodMagecart is inserting malicious code into HTML pages of various websites, with a focus on food and retail industries.RetailMagecart is inserting malicious code into HTML pages of various websites, with a focus on food and retail industries.