North Korean Campaign Tied to 30,000 Compromised Devices and $10.71 Million in Crypto Losses
Summary
A joint advisory says the Contagious Interview campaign compromised at least 30,000 devices and affected over 7,000 crypto wallets. Fake job offers deliver malware to developers; related IT-worker schemes use proxies for hiring.
Key points
- A joint advisory from agencies in Japan, the U.S., Australia, and Germany estimates at least 30,000 devices in more than 100 countries were compromised.
- The actors allegedly stole funds or credentials from more than 7,000 cryptocurrency wallets, with estimated crypto losses of at least $10.71 million.
- The campaign targets developers and crypto, blockchain, and Web3 professionals with fake job offers and coding assessments.
- The reported infection chain deploys malware including BeaverTail, InvisibleFerret, FlexibleFerret, and OtterCookie.
- The advisory says infections can enable persistent access, data theft, espionage, and further movement into victims’ employers’ networks.
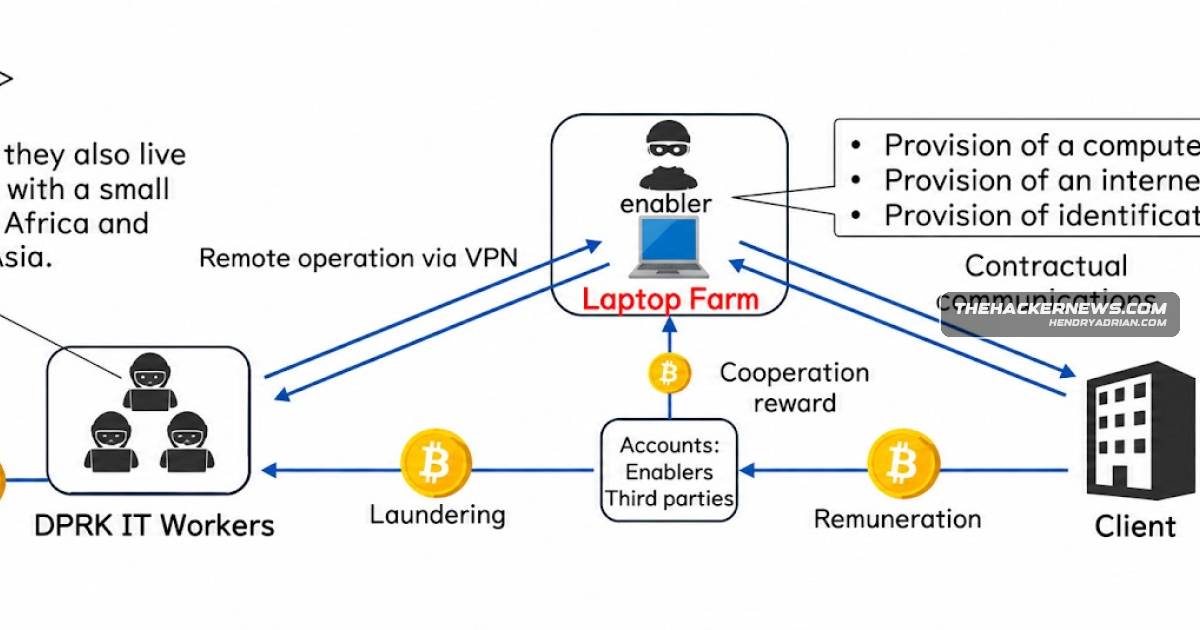
- A laptop farm operated by a facilitator in Japan was identified and dismantled, according to the agencies.
- Silent Push reported that a North Korean IT worker used a Discord server to recruit proxies for job interviews, offering them a share of the earnings.
Article Details
- Event Type
- North Korean cyber campaign and IT worker operation targeting developers and cryptocurrency professionals through fake job offers, malware, and proxy hiring.
- Impact
- At least 30,000 devices across more than 100 countries were compromised, and more than 7,000 cryptocurrency wallets had funds or credentials stolen. Estimated cryptocurrency losses are at least $10.71 million. The activity also enables credential theft, espionage, intellectual property theft, data exfiltration, and further access to organizations employing targeted developers.
MITRE ATT&CK
T1036 · MasqueradingIT workers reportedly use false identities and stolen ID images to impersonate victims.T1041 · Exfiltration Over C2 ChannelThe advisory says backdoor access is used for data exfiltration.T1056 · Input CaptureThe operation harvests sensitive information and credentials from victims.T1059.001 · PowerShellTargets are asked to complete coding tests that trigger a multi-step infection chain deploying malware.T1071.001 · Web ProtocolsWaterPlum actors are reported to use online chat platforms to communicate with developers.T1090 · ProxyThe IT worker operation uses proxies to bypass geographic and compliance restrictions.T1566.002 · Spearphishing LinkThe campaign uses fake job offers and recruitment messages to lure targets.
Threat Actors
CL-STA-0240Listed as a community tracking name associated with the activity.Contagious InterviewA threat cluster associated with the Contagious Interview campaign and the IT worker operation; reported activity includes malware deployment, credential theft, espionage, and proxy hiring.DeceptiveDevelopmentListed as a community tracking name associated with the activity.Void DokkaebiListed as a community tracking name associated with the activity.
Malware
BeaverTail#ContagiousInterviewFlexibleFerretthat leads to the deployment of various malware families, including BeaverTail, InvisibleFerret, FlexibleFerret, GolangGhost, PylangGhost, OtterCookie, RATatouille, OtterCandy, and StoatWaffle.GolangGhostto the deployment of various malware families, including BeaverTail, InvisibleFerret, FlexibleFerret, GolangGhost, PylangGhost, OtterCookie, RATatouille, OtterCandy, and StoatWaffle.InvisibleFerret#ContagiousInterviewOtterCandyBeaverTail, InvisibleFerret, FlexibleFerret, GolangGhost, PylangGhost, OtterCookie, RATatouille, OtterCandy, and StoatWaffle.OtterCookiemalware families, including BeaverTail, InvisibleFerret, FlexibleFerret, GolangGhost, PylangGhost, OtterCookie, RATatouille, OtterCandy, and StoatWaffle.PylangGhostof various malware families, including BeaverTail, InvisibleFerret, FlexibleFerret, GolangGhost, PylangGhost, OtterCookie, RATatouille, OtterCandy, and StoatWaffle.RATatouilleincluding BeaverTail, InvisibleFerret, FlexibleFerret, GolangGhost, PylangGhost, OtterCookie, RATatouille, OtterCandy, and StoatWaffle.StoatWaffleInvisibleFerret, FlexibleFerret, GolangGhost, PylangGhost, OtterCookie, RATatouille, OtterCandy, and StoatWaffle.
Products
Tools
Countries
AustraliaThe alert comes courtesy of cybersecurity and intelligence agencies from Japan, the U.S., Australia, and Germany.GermanyThe alert comes courtesy of cybersecurity and intelligence agencies from Japan, the U.S., Australia, and Germany.JapanThe alert comes courtesy of cybersecurity and intelligence agencies from Japan, the U.S., Australia, and Germany.North KoreaComplementing North Korea’s offensive cyber capabilities is the infamous IT worker scheme, which is tasked with generating illicit revenue for the regime by landing jobs in Western companies and elsewhere under falseUnited StatesThe alert comes courtesy of cybersecurity and intelligence agencies from Japan, the U.S., Australia, and Germany.
Industries
BlockchainThe primary targets of the campaign are individual web designers, engineers, and specialists in cryptocurrency, blockchain, and Web3 technologies.Cryptocurrencyat least 30,000 devices in over 100 countries and stolen funds or credentials from more than 7,000 cryptocurrency wallets, causing at least $10.71 million in losses.Web3The primary targets of the campaign are individual web designers, engineers, and specialists in cryptocurrency, blockchain, and Web3 technologies.