
ShinyHunters Claims FBI Breach and Data Theft Using PeopleSoft Zero-Day
Summary
ShinyHunters claims it exploited an unpatched Oracle PeopleSoft zero-day to access FBI systems and steal employee and applicant data. BleepingComputer has not independently verified the alleged vulnerability or breach.
Key points
- ShinyHunters claims it used a new, unpatched Oracle PeopleSoft vulnerability for initial access, then moved into FBI-managed AWS GovCloud infrastructure.
- The group alleges it stole 2TB to 3TB of data, including employee, former employee, and applicant records, and accessed FBI Criminal Justice, HR, and Medlink services.
- ShinyHunters claims the FBI detected the intrusion and took affected systems offline; the group also says it is targeting other organizations with the alleged flaw.
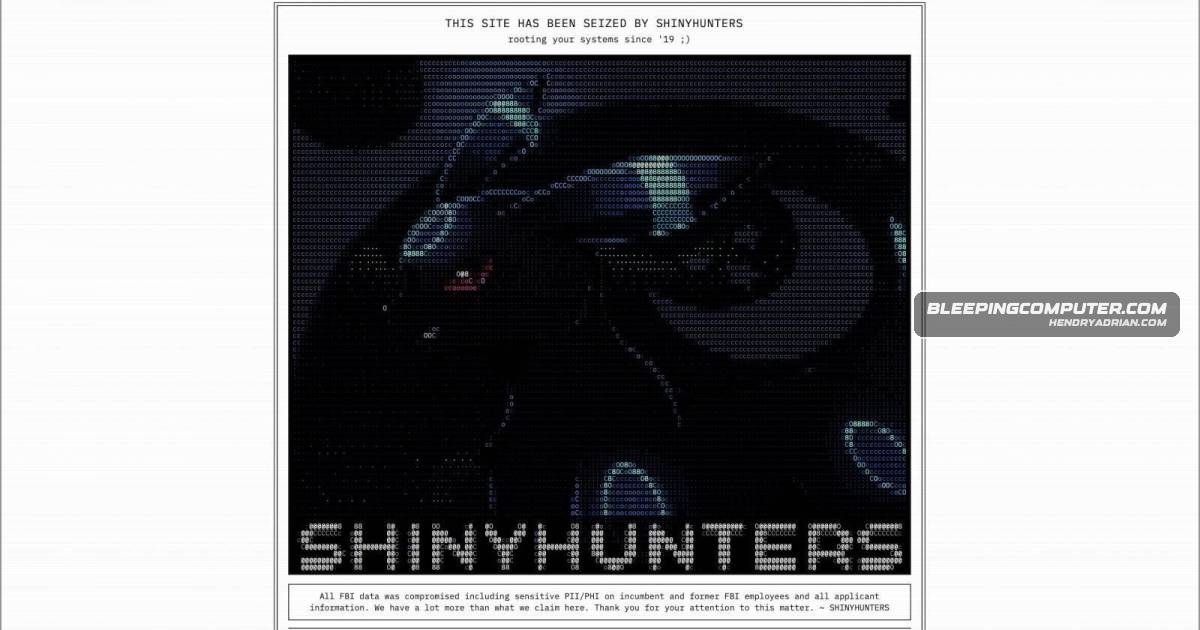
- The group shared a screenshot showing the FBI Jobs site, apply[.]fbijobs[.]gov, defaced with a claim that employee and applicant information had been compromised.
- BleepingComputer says it has not independently verified the alleged vulnerability, lateral movement, or volume and authenticity of the stolen data. 404 Media reported verifying some details in a sample of approximately 5,000 purported employee records.
Article Details
- Victim Organization
- FBI
- Incident Type
- Alleged breach involving exploitation of an unpatched Oracle PeopleSoft zero-day for remote code execution, followed by alleged access to FBI-managed AWS GovCloud systems, data theft, and defacement of the FBI Jobs website.
- Data Types Exposed
- Personally identifiable information
- Health-related information
- FBI employee and applicant information
- Internal records
- Affected Records
- ShinyHunters claimed to have stolen employee and applicant records; 404 Media received a sample of approximately 5,000 purported FBI employee records. The total number of affected records is unknown.
- Affected Data Size
- ShinyHunters claimed it stole between 2TB and 3TB of data; this has not been independently verified.
- Operational Impact
- ShinyHunters claimed the FBI took affected systems offline and terminated access to multiple networks after detecting the intrusion. The group also claimed to have defaced the FBI Jobs website. These claims have not been independently verified.
- Ransom Or Extortion
- ShinyHunters said its demand to correct or remove an FBI FLASH report was not financially motivated and was not extortion. When asked whether it would release the allegedly stolen data if the demand was not met, the group declined to comment.
- Claim Status
- alleged
MITRE ATT&CK
People
Threat Actors
Vendors
Amazon Web ServicesShinyHunters claims it breached FBI systems by exploiting an unpatched Oracle PeopleSoft zero-day, then moved into FBI-managed AWS GovCloud infrastructure and stole sensitive employee and applicant data.OracleShinyHunters claims it breached FBI systems by exploiting an unpatched Oracle PeopleSoft zero-day, then moved into FBI-managed AWS GovCloud infrastructure and stole sensitive employee and applicant data.
Products
AWS GovCloudShinyHunters claims it breached FBI systems by exploiting an unpatched Oracle PeopleSoft zero-day, then moved into FBI-managed AWS GovCloud infrastructure and stole sensitive employee and applicant data.PeopleSoftShinyHunters claims it breached FBI systems by exploiting an unpatched Oracle PeopleSoft zero-day, then moved into FBI-managed AWS GovCloud infrastructure and stole sensitive employee and applicant data.