ClosedQuorum Windows Malware Uses AI Models to Choose Post-Compromise Actions
Summary
Cisco Talos says the Go-based ClosedQuorum malware uses AI models to select post-compromise actions, including credential theft, shellcode injection and persistence. Its analyzed build cannot perform a listed lateral-movement action; in-the-wild use is unconfirmed.
Key points
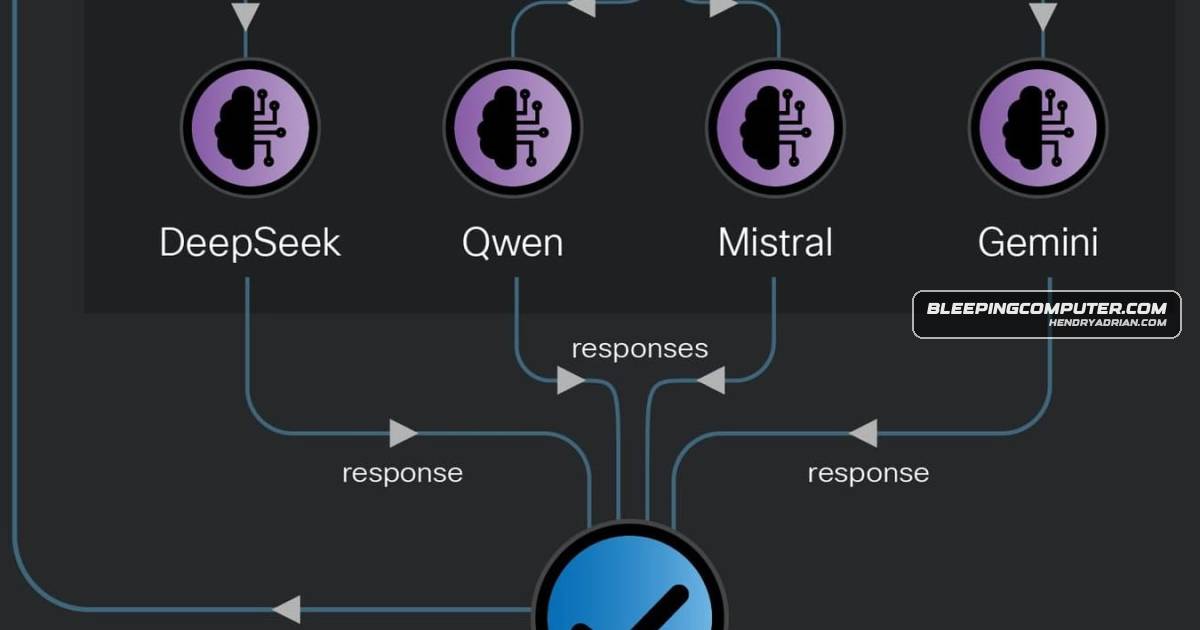
- ClosedQuorum uses Google Gemini, DeepSeek, Qwen and Mistral in a voting system to select actions based on reconnaissance; DeepSeek takes priority in a tie.
- The Go-based Windows malware can steal credentials, inject shellcode using process hollowing or Early Bird APC injection, and establish persistence.
- A lateral-movement option appears in the decision set, but the analyzed build has no handler to execute it.
- Stolen data is sent to operators through a Discord webhook; Cisco Talos says the analyzed binary contained placeholder API credentials and a dummy webhook.
- Cisco Talos says there is no confirmation of in-the-wild deployment. It linked binary artifacts to a developer's criminal-forum postings about carding dating to 2025.
- Talos describes the malware as a possible shift toward automated attack chains, while noting reliance on commercial AI APIs could cause problems if they are rate-limited, unavailable or return malformed output.
Article Details
- Event Type
- Cisco Talos reported the discovery of ClosedQuorum, a Windows malware that uses AI models to select post-compromise actions.
- Impact
- ClosedQuorum can steal credentials, generate and inject shellcode, and execute a persistence module. It sends stolen data through a Discord webhook. Cisco Talos reported no confirmation of in-the-wild deployment; the analyzed binary contained placeholder API credentials and a dummy webhook.
MITRE ATT&CK
T1003.001 · LSASS MemoryThe malware's steal decision includes LSASS credential dumping.T1055.004 · Asynchronous Procedure CallThe malware can inject shellcode using Early Bird APC injection.T1055.012 · Process HollowingThe malware can inject shellcode using process hollowing.T1555.003 · Credentials from Web BrowsersThe malware's steal decision includes credential theft from Chrome, Edge, and Firefox.
Malware
Products
DeepSeekClosedQuorum is a new Windows malware that uses Google Gemini, DeepSeek, Qwen, and Mistral AI to autonomously choose post-compromise actions without human operator commands.Google GeminiClosedQuorum is a new Windows malware that uses Google Gemini, DeepSeek, Qwen, and Mistral AI to autonomously choose post-compromise actions without human operator commands.Mistral AIClosedQuorum is a new Windows malware that uses Google Gemini, DeepSeek, Qwen, and Mistral AI to autonomously choose post-compromise actions without human operator commands.QwenClosedQuorum is a new Windows malware that uses Google Gemini, DeepSeek, Qwen, and Mistral AI to autonomously choose post-compromise actions without human operator commands.