
Doxbin: How the Doxing Site Exposes Personal Information and Puts Victims at Risk
Summary
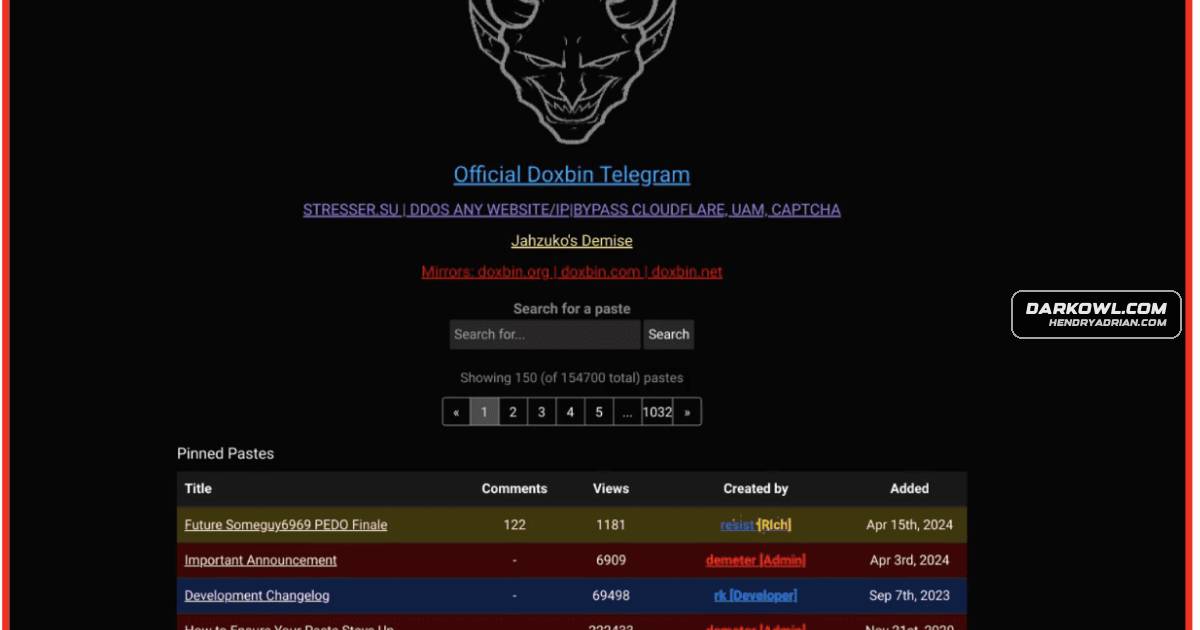
DarkOwl examines Doxbin’s history, the personal data shared on the site, and risks including swatting, identity theft and harassment. Claims that an operator was kidnapped remain unverified; the site is operating again.
Key points
- Doxbin is a paste site used to publish personal information about individuals, often without consent; the article says posted claims are not validated.
- Examples of exposed data include names, addresses, phone numbers, account credentials, financial information and details about family members.
- Information may come from public sources or, in some cases, hacking, according to the article.
- Doxed individuals may face swatting, identity theft, financial crime, stalking, harassment and reputational harm.
- The article recounts Doxbin’s history, including its original launch in 2011 and a law-enforcement seizure in 2014.
- In mid-May, images and videos circulated alleging that an operator had been kidnapped; the claim could not be verified, and the site later returned to normal operation.
- DarkOwl recommends monitoring the site for exposed company and employee information.
Article Details
- Topic
- Doxbin and its role in doxing, swatting, and related harms