Documentation Placeholder Domain Used to Deliver Windows ClickFix Attack
Summary
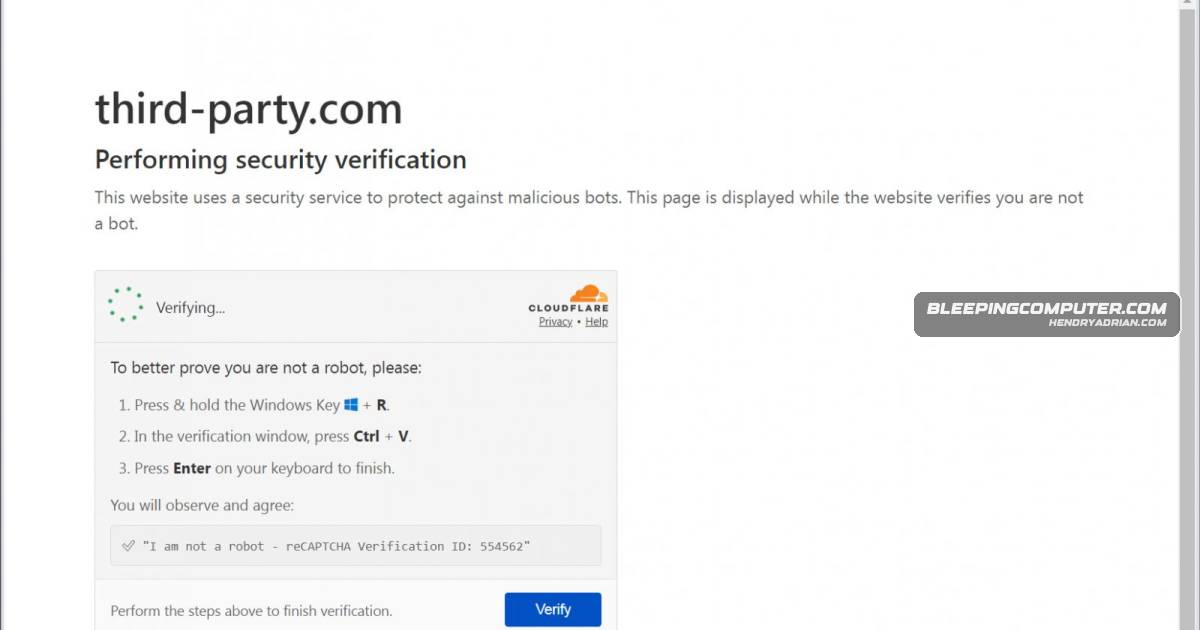
third-party[.]com is serving a fake Cloudflare check that tricks Windows users into running a PowerShell payload. The download site no longer resolves, and no executions from copied documentation references have been reported.
Key points
- Manifold Security reported that third-party[.]com, long used as a documentation placeholder, is serving a fake Cloudflare verification page.
- Clicking the fake verification prompt copies a PowerShell command to the clipboard and tells Windows users to run it via the Run dialog.
- The command was configured to download a script from elxxvvx[.]xyz; BleepingComputer found that domain no longer resolved during testing.
- A May 2, 2026 Hybrid Analysis report showed the script downloading a 134MB archive and attempting to launch draw.io.exe; the archive was unavailable for analysis.
- The page reportedly shows unsupported-operating-system errors to macOS and Linux visitors rather than the clipboard-based lure.
- The domain appears in public documentation and code examples, but there are no reports that copied references have led to ClickFix executions.
Article Details
- Event Type
- ClickFix attack using a fake Cloudflare verification page to trick Windows users into executing malicious PowerShell commands.
- Impact
- The page copies a command to the clipboard that downloads and runs a PowerShell script. A reported attack chain attempted to download a 134MB ZIP archive and launch draw.io.exe, but the archive was unavailable, so its payload could not be determined. The chain was broken at the time of testing, and no attacks resulting from copied documentation references had been reported.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | third-party[.]com | Domain serving the fake Cloudflare verification page used as a ClickFix lure. |
| URL | hxxps[:]//elxxvvx[.]xyz/update2[.]zip | Reported URL for the ZIP archive the downloaded PowerShell script attempted to retrieve; the archive was no longer available. |
MITRE ATT&CK
T1059.001 · PowerShellThe attack chain uses a malicious PowerShell command and downloads a PowerShell script.T1105 · Ingress Tool TransferThe PowerShell script downloads a ZIP archive from a remote URL.T1140 · Deobfuscate/Decode Files or InformationThe command reconstructs the payload URL before downloading the script.T1204.002 · Malicious FileThe ClickFix page instructs users to manually run the copied PowerShell command.
People
Products
CloudflareThe third-party.com domain, long used as a placeholder in developer documentation, is now serving a fake Cloudflare verification page that tricks Windows users into running malicious PowerShell commands.Microsoft WindowsThe third-party.com domain, long used as a placeholder in developer documentation, is now serving a fake Cloudflare verification page that tricks Windows users into running malicious PowerShell commands.