ThreatsDay Roundup: AI Search Poisoning, Coding-Tool Data Exposure, and One-Click Code Execution
Summary
This roundup covers credential theft, malware, AI-tool data exposure, supply-chain attacks, a malicious WordPress plugin update, and a reported VS Code flaw, alongside new defensive measures and security advisories.
Key points
- RemControl, an Android banking trojan distributed through fake TVTap pages promoted by Meta ads, uses Accessibility Services to overlay banking apps, capture keystrokes and screens, and remotely control infected devices.
- Z.ai disabled ZCode features after a default workflow sent local code repositories to Alibaba Cloud without users’ consent.
- Researchers reported that the Russian super-app MAX can capture mini-app screens, access their local storage, inject JavaScript, mediate network traffic, and control authentication context.
- A reported AI search-poisoning campaign seeds online content with fraudulent contact details and login pages that may be surfaced in AI-generated answers for major companies.
- A malicious Admin Menu Editor Pro update installed a web shell; the maintainer said at least 230 customers installed the compromised update on 1,500 sites and released version 2.37.
- SafeDep reported a malicious dependency in Deep-Live-Cam that downloads a clipboard hijacker, and a typosquatted npm package that installs a cross-platform remote-access trojan.
- The roundup also covers a GitHub Actions cache-access control intended to reduce cache-poisoning risk, and a reported VS Code vulnerability that could enable code execution after a user clicks a link.
Article Details
- Event Type
- Weekly cybersecurity threat roundup covering malware and phishing campaigns, supply-chain incidents, security research, and security advisories.
- Impact
- Reported threats include credential and financial-data theft, device and account compromise, malicious software distribution, cryptocurrency theft, ransomware and extortion, and exposure of sensitive source code. A malicious plugin update was installed by at least 230 customers across 1,500 sites.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | adminmenueditor[.]com | Compromised plugin update server used to distribute a malicious Admin Menu Editor Pro update. |
MITRE ATT&CK
T1056.001 · KeyloggingRemControl logs keystrokes from infected Android devices.T1195.001 · Compromise Software Dependencies and Development ToolsA malicious source dependency was added to Deep-Live-Cam, and a typosquatted npm package delivered a trojan through its postinstall hook.T1204.002 · Malicious FileThe DarkMe incidents relied on victims being persuaded to run a malicious .pif file.T1505.003 · Web ShellThe malicious Admin Menu Editor Pro update installed a web shell on affected sites.T1566.001 · Spearphishing AttachmentReported phishing campaigns used email to lure victims to credential-theft pages or to deliver a malicious .pif file.
CVE
CVE-2023-38831“Two years ago, DarkMe developed a reputation by leveraging two separate zero days to deliver its malware: WinRAR (CVE-2023-38831) and Windows Defender SmartScreen (CVE-2024-21412),” Huntress said.CVE-2024-21412“Two years ago, DarkMe developed a reputation by leveraging two separate zero days to deliver its malware: WinRAR (CVE-2023-38831) and Windows Defender SmartScreen (CVE-2024-21412),” Huntress said.
People
Ariel SimonVigilance Security source cited for reporting the AI search poisoning campaign.Janis ElstsMaintainer of Admin Menu Editor Pro who reported the malicious updates and response.Max HirschbergerResearcher who detailed Process Parameter Poisoning.Ogulcan UgurResearcher who detailed Process Parameter Poisoning.Quentin BourgueSecurity researcher cited for describing Exvicy's reuse of ErrTraffic code.
Threat Actors
Malware
DarkMeThe roundup also highlighted supply chain abuse, EDR evasion, malicious WordPress updates, and phishing campaigns tied to RemControl, MAX, Exvicy, DarkMe, Global Group, and MicrosoftSystem64.Global GroupThe roundup also highlighted supply chain abuse, EDR evasion, malicious WordPress updates, and phishing campaigns tied to RemControl, MAX, Exvicy, DarkMe, Global Group, and MicrosoftSystem64.MicrosoftSystem64The roundup also highlighted supply chain abuse, EDR evasion, malicious WordPress updates, and phishing campaigns tied to RemControl, MAX, Exvicy, DarkMe, Global Group, and MicrosoftSystem64.RemControlThe roundup also highlighted supply chain abuse, EDR evasion, malicious WordPress updates, and phishing campaigns tied to RemControl, MAX, Exvicy, DarkMe, Global Group, and MicrosoftSystem64.
Vendors
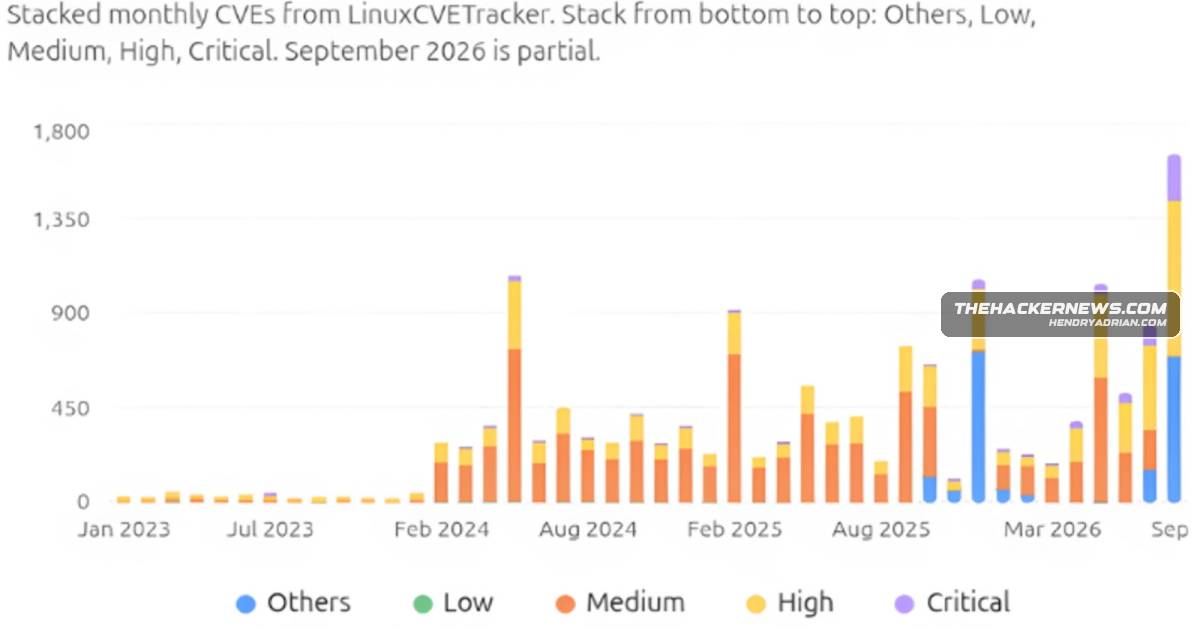
Alibaba CloudZ.ai disabled ZCode features after local repositories were sent to Alibaba Cloud.CanonicalThe “recent explosion” in the volume of CVEs, mainly driven by AI, has prompted Canonical to transition to a unified, 2-week release cycle that merges its four-week cycle for regular Stable Release Updates (SRUs) andGitHubis uploaded to social media, websites that allow file uploads, website hosting platforms (Google sites, GitHub pages, WordPress, and Blogger), fundraisers, job search, and event platforms (Posh.vip, onecause.com,MicrosoftRemedio has detailed a Visual Studio Code vulnerability that could transform Microsoft’s code editor into a vector for compromise through a single link.VKMAX is a state-backed Russian mobile “super-app” developed by VK (aka VKontakte) that combines instant messaging, e-commerce, banking, and public government services.Z.aiZ.ai disabled ZCode features after local repositories were sent to Alibaba Cloud.
Products
Admin Menu Editor ProA malicious version of the Admin Menu Editor Pro plugin for WordPress was uploaded to adminmenueditor[.]com on September 14, 2026.Deep-Live-CamSafeDep has disclosed that an unknown threat actor added on September 8, 2026, a malicious source dependency to Deep-Live-Cam, a Python face swapping application with 96,600 GitHub stars.GitHub ActionsGitHub has announced that developers can now use cache-mode to apply least-privilege access to the GitHub Actions cache at the workflow or job level.MaxThe roundup also highlighted supply chain abuse, EDR evasion, malicious WordPress updates, and phishing campaigns tied to RemControl, MAX, Exvicy, DarkMe, Global Group, and MicrosoftSystem64.VSCodeRemedio has detailed a Visual Studio Code vulnerability that could transform Microsoft’s code editor into a vector for compromise through a single link.ZCodeZ.ai disabled ZCode features after local repositories were sent to Alibaba Cloud.
Countries
CanadaA previously undocumented Android banking trojan dubbed RemControl is targeting retail banking customers across Western Europe (Italy, France, Spain, Poland, Portugal), the Middle East, and Canada.FranceA previously undocumented Android banking trojan dubbed RemControl is targeting retail banking customers across Western Europe (Italy, France, Spain, Poland, Portugal), the Middle East, and Canada.ItalyA previously undocumented Android banking trojan dubbed RemControl is targeting retail banking customers across Western Europe (Italy, France, Spain, Poland, Portugal), the Middle East, and Canada.PolandA previously undocumented Android banking trojan dubbed RemControl is targeting retail banking customers across Western Europe (Italy, France, Spain, Poland, Portugal), the Middle East, and Canada.PortugalA previously undocumented Android banking trojan dubbed RemControl is targeting retail banking customers across Western Europe (Italy, France, Spain, Poland, Portugal), the Middle East, and Canada.SpainA previously undocumented Android banking trojan dubbed RemControl is targeting retail banking customers across Western Europe (Italy, France, Spain, Poland, Portugal), the Middle East, and Canada.