Ransomware Activity Surged in 2024 as New Groups Emerged and Major Victims Were Hit
Summary
DarkOwl’s 2024 roundup describes active ransomware groups, major attacks and rising activity, including 31 new groups and a record 574 attacks reported in December.
Key points
- RansomHub claimed 593 victims in 2024; Play claimed 362 and Akira 291, according to the article.
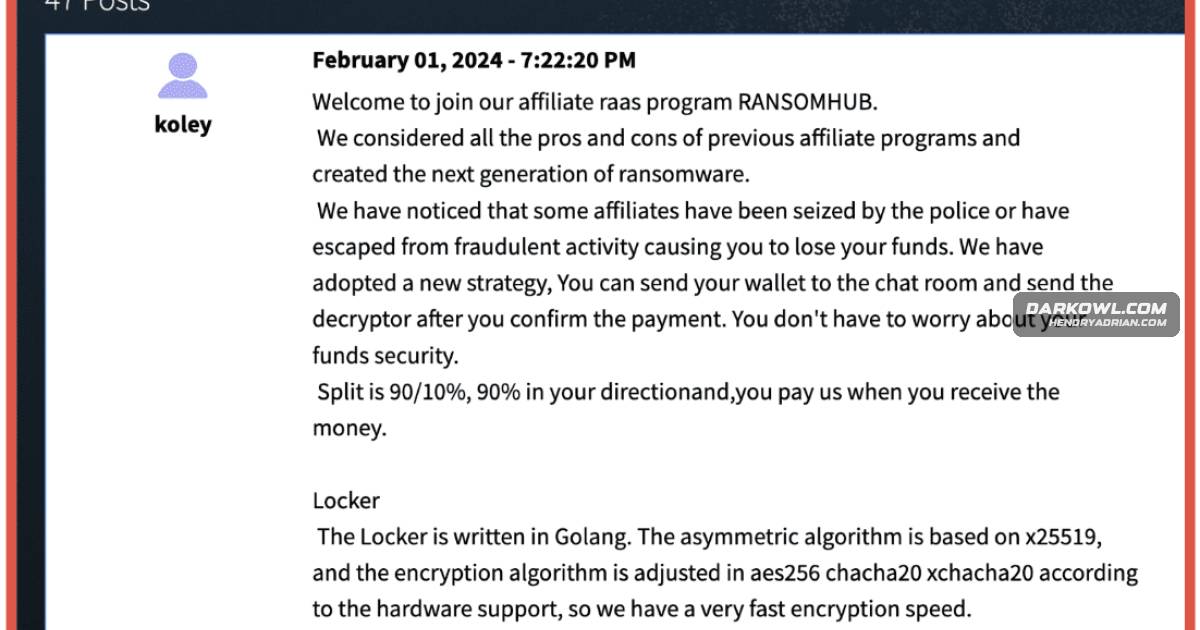
- The article says LockBit continued operating after disruption from Operation Cronos, while RansomHub became one of the most active groups.
- Change Healthcare’s attack affected more than 190 million people, and the article says the company paid a $22 million ransom.
- Attacks on CDK Global and Blue Yonder disrupted services used by dealerships, Starbucks and Sainsbury’s.
- The article reports 574 ransomware attacks in December 2024, the highest monthly total since monitoring began in 2021.
- It says the number of active ransomware groups rose 30% year over year, with 31 new groups entering the ecosystem.
Article Details
- Publisher
- DarkOwl
- Report Period
- 2024
- Scope
- Ransomware groups, activity trends, and selected victim incidents during 2024
- Key Statistics
- RansomHub claimed 593 victims by year-end 2024.
- Play claimed 362 victims during 2024; Akira claimed 291.
- There were 574 ransomware attacks in December 2024, the highest monthly total since monitoring began in 2021.
- The number of active ransomware groups increased 30% year over year, with 31 new groups entering the ecosystem.
- The Change Healthcare breach affected over 190 million individuals; the Medisecure breach affected approximately 12.9 million.
- Recommendations
- Adopt robust cybersecurity measures.
- Use dark web monitoring and maintain vigilance.
Threat Actors
AkiraRansomware group reported to use double extortion and target organizations, particularly in the United States.BlackCatRansomware group reported as responsible for the Change Healthcare attack; the article identifies ALPHV as an alternate name.LockBitRansomware group whose affiliates continued conducting attacks despite disruptions from Operation Cronos.PlayRansomware group reported to exploit vulnerabilities in widely used software to gain initial access.RansomHubRansomware group reported as responsible for attacks including breaches affecting a U.S. healthcare payment system and Albyn Housing Society.
Vendors
CitrixThe group is known for exploiting vulnerabilities in widely used software, such as Fortinet, Citrix, and VMware’s ESXi, to gain initial access to target systems.FortinetThe group is known for exploiting vulnerabilities in widely used software, such as Fortinet, Citrix, and VMware’s ESXi, to gain initial access to target systems.VMwareThe group is known for exploiting vulnerabilities in widely used software, such as Fortinet, Citrix, and VMware’s ESXi, to gain initial access to target systems.
Products
ESXiThe group operates a ransomware-as-a-service (RaaS) model, targeting multiple platforms, including Windows, Linux, and ESXi.LinuxThe group operates a ransomware-as-a-service (RaaS) model, targeting multiple platforms, including Windows, Linux, and ESXi.Microsoft WindowsThe group operates a ransomware-as-a-service (RaaS) model, targeting multiple platforms, including Windows, Linux, and ESXi.
Countries
AustraliaThis is the largest breach of data in Australia’s history.Canadaand Canada. The company paid a $25 million ransom to the Eastern European and Russian hacker group BlackSuit to restore services.ScotlandAlbyn Housing Society, one of Scotland’s largest housing charities, was hacked by the ransomware gang RansomHub.United StatesThe adversary seems to target almost exclusively companies originating from and operating in the United States.