Acronis Details INC Ransomware’s Growth, Tactics and Cross-Platform Payloads
Summary
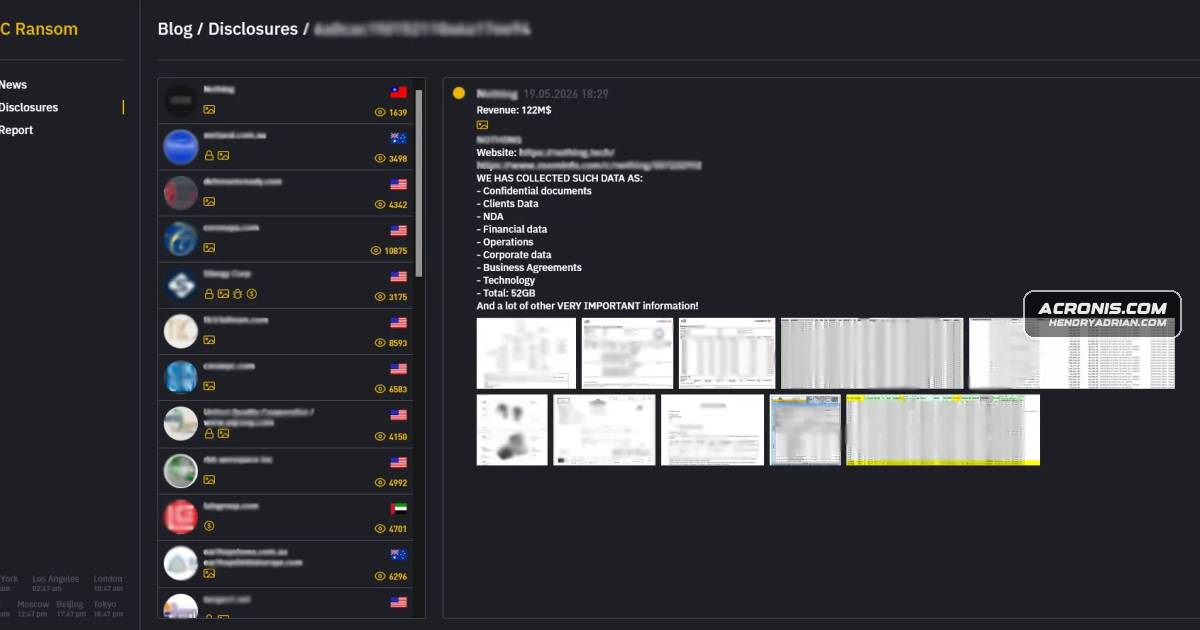
Acronis examines INC ransomware’s growth to more than 800 claimed victims since 2023, its intrusion methods and Windows and Linux/ESXi payloads, and offers IOCs and mitigation recommendations.
Key points
- INC has claimed more than 800 victims since 2023 and is among the most active ransomware groups in 2026; the report says U.S. organizations account for 65.3% of listed victims.
- Recent initial-access methods include spear phishing, stolen credentials and exploitation of exposed vulnerabilities, including flaws in Citrix, Fortinet and SimpleHelp products.
- In recent incidents, affiliates used a modified script to extract credentials from Veeam backup servers, including support for newer salted DPAPI encryption.
- Observed intrusion activity included network discovery, RDP and PsExec for lateral movement, tools to impair endpoint protection, and RMM software for remote access.
- The group stages and exfiltrates data using 7-Zip and rclone before encrypting systems; its Linux/ESXi payload can shut down virtual machines.
- Acronis reports that INC source code was offered for sale in 2024 and that Lynx and Sinobi later showed code overlap with INC.
- The report provides YARA rules and file and network indicators, and recommends tested offline or immutable backups, MFA, segmentation, endpoint protection and timely patching.
Article Details
- Publisher
- Acronis Threat Research Unit
- Report Period
- 2023–2026
- Scope
- INC ransomware evolution, attack chain, victimology, tooling, and Windows and Linux/ESXi payloads.
- Key Statistics
- INC claimed more than 800 victims since 2023.
- Organizations in the United States accounted for 65.3% of listed victims as of the report's publication.
- The report places INC among the five most active ransomware groups globally in 2026.
- In May 2024, a forum user listed INC's Windows and Linux/ESXi payloads for $300,000, with the listing limited to three buyers.
- The report identifies five leading 2026 target sectors: legal services, manufacturing, technology, health care, and construction.
- Recommendations
- Maintain at least three backup copies on two media types, keep one copy off-site, and use offline or immutable backups that are regularly tested.
- Deploy and update EDR and ransomware protection with behavioral detections and anti-tamper protections enabled.
- Require multifactor authentication and strong passwords.
- Segment networks, disable unnecessary services and ports, and restrict outbound traffic.
- Prioritize patching vulnerabilities known to be exploited by ransomware and train staff on phishing and social engineering.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | incblog[.]su | Listed as INC ransomware network infrastructure. |
| SHA256 | 1898d056463284d849801cbdea6a3dec6c9f568f01569912c3868a5eea9a5449 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | 1d10d8f5a420d0e4683b4cb40bcf0c984d1e7ea1f3b4442a00a525584632ac11 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | 24f6c0ca39b2a5593086ff56d818ddfbde121f8e44d54faa762e510397dc9db7 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | 31800380c359143ae82c4f9011eee653dd22443d03d6a499148203bbfc275502 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | 589d9480fbfec2d8e61638eb0b537183d0f9977411fd1d2c0f8eb611feebe880 | SHA-256 hash listed under Linux INC ransomware indicators of compromise. |
| SHA256 | 5cc212f84d2bf3fbab165aaf09b16e00fcf2f1ccd880d24b14404c53dcdbf241 | SHA-256 hash listed under Linux INC ransomware indicators of compromise. |
| SHA256 | 60aeb9f7bccf377ff02ed64783e66a62c0f976878d9729b067bc7e5b0b9da9d6 | SHA-256 hash listed under Linux INC ransomware indicators of compromise. |
| SHA256 | 6bf155b269d452f3c3b62832b27bbebe4da436e228dbf521155b1d5989e3743f | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | 6cd349eda0fa6c8b274a0920852c68f8b727afea1fdbc69ad183cef05d9cf141 | SHA-256 hash listed under Linux INC ransomware indicators of compromise. |
| SHA256 | 765508aa2ec6a1b73a76a23f4fa559d32355622748c91a46ed7b315eae2ee60a | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | 7f37351979c249417cb180b4ede0ed17e5fe2a1f08add4d72606b589f8fdb245 | SHA-256 hash listed under Linux INC ransomware indicators of compromise. |
| SHA256 | 8d1a22c430252f29611766b8e4a82af0fba60d609246463466b384d6d4793df4 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | 90e46e89fec2108a1cb4850bb33e3563e92a14d04e1e613ac8c9311f152d294c | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | 97aebda5482899fef84a24e456bff055acaa47e5ab4029f768d9e0c62a660ce2 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | acce811c4fc2a6e3fddd4231e386f1648ca44f039d2d275316bc0a0fc96e0af4 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | bf8c45e5aa9551a17eefbd1d179422c32b4309c47ee9a3f315bb80ed6d4f7efc | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | d26bfb0147f60dc6500a9298d521ee67b49daaf4b8f8be54e7cc8fd86a597570 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | d65120291dee76c694f8bea54841f7f68329b499b28f4aee5ea5c9369a7432cb | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | dc9938f51150d13a69fc25f3f19052eacb1bf0a086fd5cf39762501fb3ddd7da | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | ea721240c14e3d14f8d88e0020880448c6c602f1180a1e5dbe40871cfeedcc22 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | f6a01d0246ce31faf6938ea488086d4358505405a4ef5c5faa482e79e92cb347 | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
| SHA256 | ff5da8f0330a4c581c37284c74aae2683c007dc6e406e1e2e6803e7bb398b77b | SHA-256 hash listed in the report's INC ransomware indicators of compromise. |
CVE
CVE-2023-3519vulnerabilities in public-facing applications such as CVE-2023-3519 (CitrixCVE-2023-48788Netscaler), CVE-2023-48788 (Fortinet EMS), CVE-2024-57727 (SimpleHelp RMM) andCVE-2024-57727Netscaler), CVE-2023-48788 (Fortinet EMS), CVE-2024-57727 (SimpleHelp RMM) andCVE-2025-5777CVE-2025-5777 (Citrix Bleed 2).
People
Threat Actors
BlackCatRansomware operation whose shutdown reportedly contributed to affiliates migrating to INC; also cited as a payload used by Vice Society.INCRansomware-as-a-service group described as conducting attacks and claiming victims.JSWORMRansomware operation named in a reported link between salfetka and the aliases rinc and farnetwork.KarmaRansomware operation named in a reported link between salfetka and the aliases rinc and farnetwork.LockBitRansomware operation whose disruption reportedly contributed to affiliates migrating to INC.LynxRansomware operation reported to have emerged after INC source code was listed for sale, with substantial code overlap.NefilimRansomware operation named in a reported link between salfetka and the aliases rinc and farnetwork.NemtyRansomware operation named in a reported link between salfetka and the aliases rinc and farnetwork.NokoyawaRansomware operation named in a reported link between salfetka and the aliases rinc and farnetwork.sinobiRansomware operation reported to have emerged after the sale of INC source code.Vice SocietyObserved deploying INC ransomware against the health care industry in late 2024.
Malware
BlackCatThe disruption of LockBit and the shutdown of BlackCat created opportunities for INC to expand as affiliates migrated to alternative ransomware operations.Hello Kittyof cycling through third-party payloads such as BlackCat, Rhysida, Hello Kitty,INC ransomwareFrom emerging threat to top-tier ransomware-as-a-service: The evolution of INC ransomwareLynxINC's influence extends beyond its own operations. Following the 2024 sale of its source code, related ransomware families such as Lynx and Sinobi emerged with significant code overlap.Quantum LockerZeppelin, and Quantum Locker. Additionally, following the disruption of LockBitRhysidaof cycling through third-party payloads such as BlackCat, Rhysida, Hello Kitty,SinobiINC's influence extends beyond its own operations. Following the 2024 sale of its source code, related ransomware families such as Lynx and Sinobi emerged with significant code overlap.ZeppelinZeppelin, and Quantum Locker. Additionally, following the disruption of LockBit
Vendors
AcronisAcronis Threat Research UnitCitrixvulnerabilities in public-facing applications such as CVE-2023-3519 (CitrixFortinetNetscaler), CVE-2023-48788 (Fortinet EMS), CVE-2024-57727 (SimpleHelp RMM) andSimpleHelpNetscaler), CVE-2023-48788 (Fortinet EMS), CVE-2024-57727 (SimpleHelp RMM) andVeeamRecent incidents reveal updated tooling, including a modified credential dumper capable of targeting newer Veeam backup deployments. The updated tool includes support for Veeam’s newer salted DPAPI credential encryptionVMwaremonths, targeting VMware infrastructure and mirroring a broader shift among
Products
Acronis EDR / XDRCitrix NetScalerESXiBoth the Windows and Linux/ESXi encryptors have been rewritten in Rust, enabling cross-platform development and increasing analysis complexity.Fortinet EMSNetscaler), CVE-2023-48788 (Fortinet EMS), CVE-2024-57727 (SimpleHelp RMM) andSimpleHelp RMMNetscaler), CVE-2023-48788 (Fortinet EMS), CVE-2024-57727 (SimpleHelp RMM) andVeeamRecent incidents reveal updated tooling, including a modified credential dumper capable of targeting newer Veeam backup deployments. The updated tool includes support for Veeam’s newer salted DPAPI credential encryptionVMwaremonths, targeting VMware infrastructure and mirroring a broader shift among
Tools
7-Zipransomware actors compress and password-protect the staged data with 7-Zip,Advanced IP Scannercases where they have used tools like Angry IP scanner, Advanced IP scanner andAngry IP scannercases where they have used tools like Angry IP scanner, Advanced IP scanner andAnyDeskStrike, AnyDesk, ScreenConnect, and TeamViewer were used by INC ransomwareCobalt Strikenetscannetscan.ProcessTerminator.exeProcessTerminator.exe -p <PID/ProcessPsExecand PsExec, to access and execute commands on other systems in the network.PsKillutility named PsKill that terminates local or remote processes by PID orRClonethen upload the archives to attacker-controlled cloud storage using rclone.ScreenConnectStrike, AnyDesk, ScreenConnect, and TeamViewer were used by INC ransomwareTeamViewerStrike, AnyDesk, ScreenConnect, and TeamViewer were used by INC ransomwareVeeam-Get-Creds.ps1version of the open-source Veeam-Get-Creds.ps1 scriptvim-cmdextracted from the blob is ‘vim-cmd’, which is a VMware Infrastructure
Countries
Australiaall the victims and with a long tail led by Australia, Canada, Germany and Taiwan.Canadaall the victims and with a long tail led by Australia, Canada, Germany and Taiwan.Germanyall the victims and with a long tail led by Australia, Canada, Germany and Taiwan.Taiwanall the victims and with a long tail led by Australia, Canada, Germany and Taiwan.United StatesUnited States organizations account for more than 65% of listed victims, with legal services, manufacturing, construction, technology and health care among the most targeted
Industries
ConstructionUnited States organizations account for more than 65% of listed victims, with legal services, manufacturing, construction, technology and health care among the most targetedEducationparticularly the heavy target of education and health care sectors in its earlyHealthcareUnited States organizations account for more than 65% of listed victims, with legal services, manufacturing, construction, technology and health care among the most targetedLegal servicesUnited States organizations account for more than 65% of listed victims, with legal services, manufacturing, construction, technology and health care among the most targetedManufacturingUnited States organizations account for more than 65% of listed victims, with legal services, manufacturing, construction, technology and health care among the most targetedProfessional Servicesservices, professional services, manufacturing and construction whereTechnologyUnited States organizations account for more than 65% of listed victims, with legal services, manufacturing, construction, technology and health care among the most targeted