Malware From a Sponsored Search Result Targeted Huntress Engineer’s Claude Code Credentials
Summary
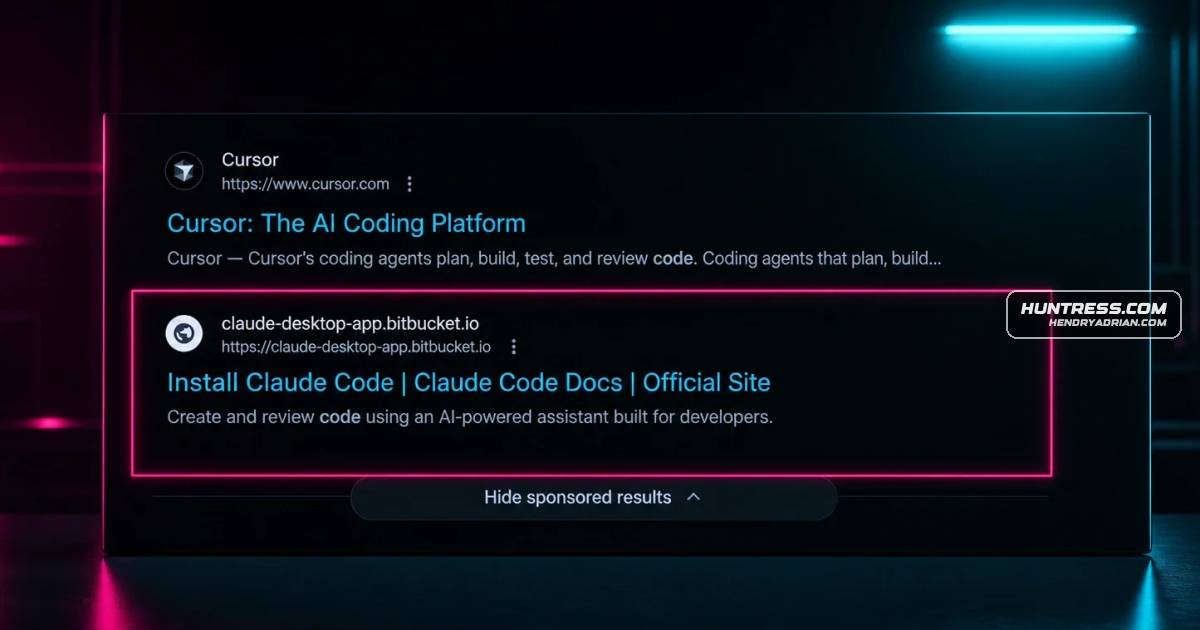
A Huntress engineer clicked a sponsored search result for Claude Code and ran malware that targeted his macOS keychain credentials. Huntress detected it, rotated credentials and found no sign attackers had used them.
Key points
- The malware was delivered after the engineer clicked a sponsored Google result while searching for “Claude Code.”
- A credential-stealing script ran on the engineer’s MacBook, using base64 encoding and gzip compression before downloading and launching a second payload.
- The payload targeted Claude Code credentials in the macOS keychain and used obfuscated AppleScript.
- Huntress tooling alerted on the activity; the engineer reported it immediately, and the SOC rotated credentials and reviewed logs.
- Huntress reported no sign the attackers had tried to use the targeted credentials.
- The article highlights rapid reporting and incident response as important safeguards against malvertising and credential theft.
Article Details
- Victim Organization
- Huntress
- Incident Type
- Malvertising-led credential-stealing malware infection on a Huntress engineer’s MacBook
- Disclosure Date
- 2026-04-09
- Operational Impact
- Malware ran on the engineer’s MacBook and attempted to obtain Claude Code credentials. The engineer reported the incident immediately; Huntress rotated credentials and reviewed logs. The article reports no evidence that the credentials were used, and says the attackers did not obtain them.
- Ransom Or Extortion
- None reported.
- Claim Status
- confirmed