
DarkOwl Tracks Hacktivist Activity Amid Iran-Israel Conflict
Summary
DarkOwl reports DDoS claims, alleged data leaks and other hacktivist activity amid the Iran-Israel conflict, while noting that some claims—including attacks on US targets—were unverified or unsupported by evidence.
Key points
- DarkOwl observed no large increase in claims of US victims from known hacktivist groups after US strikes on Iran, and found no direct threats to the US in its collection at the time.
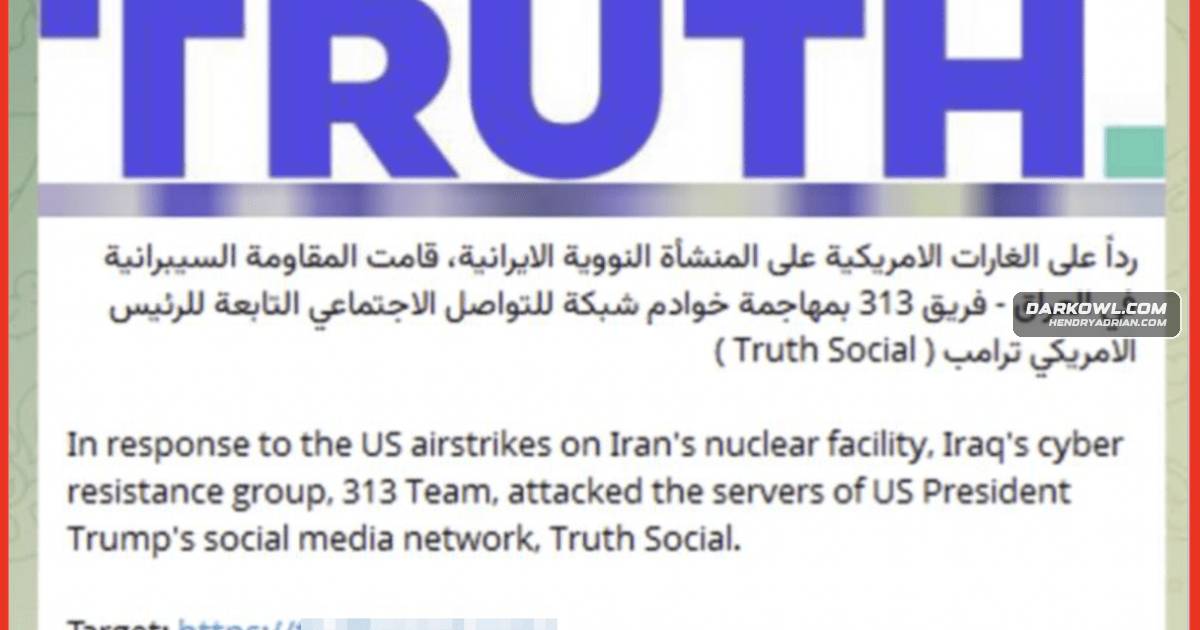
- Group 313 claimed to have taken down Truth Social, but DarkOwl said the claim was uncorroborated and the outage may have resulted from heavy traffic.
- Keymous+ claimed DDoS attacks on several US targets; Mr. Hamza claimed to target the US Air Force and FBI without providing evidence of success.
- DarkOwl reported that Nobitex, an Iranian cryptocurrency exchange, was reportedly hacked by pro-Israeli group Predatory Sparrow; researchers reportedly traced $90 million from its wallets to known hacker addresses.
- DarkOwl analysts observed posts offering or sharing alleged data leaks from Israeli and Iranian organizations, said to contain personal information.
- The article notes that groups shared AI-generated attack imagery and that Telegram posts circulated fake or misleading conflict videos, including game footage and images from earlier conflicts.
- The report says hacktivist groups were coordinating and forming alliances, while their reactions to the conflict and views on US involvement varied.
Article Details
- Event Type
- Hacktivist activity and reported cyberattacks amid the Iran-Israel conflict, including claimed DDoS attacks and a reported hack of the Iranian cryptocurrency exchange Nobitex.
- Impact
- Groups reported targeting organizations in the United States, Israel, and Iran. The article says Predatory Sparrow was reported to have targeted Nobitex, with researchers reporting that $90 million was sent from its wallets to known hacker addresses. DarkOwl analysts also identified data leaks allegedly involving Israeli and Iranian organizations, said to contain personal information. Several attack claims, including claims of successful DDoS attacks, were unverified.
MITRE ATT&CK
People
Threat Actors
Products
Countries
IranBulletin highlighting the possible threat to the United States as a result of the ongoing conflict in Iran and the US missile attacks on key nuclear sites in Iran.IsraelPresident Trump has now stated on social media that there will be a ceasefire between Iran and Israel, channels are sharing his messages on Truth Social.QatarIran retaliated with an attack against a US airbase in Qatar, which was condemned by Qatar and reportedly intercepted.United States22 DHS released a National Terrorism Advisory System Bulletin highlighting the possible threat to the United States as a result of the ongoing conflict in Iran and the US missile attacks on key nuclear sites in Iran.