Wiz Previews AI SAST for Code Vulnerability Detection
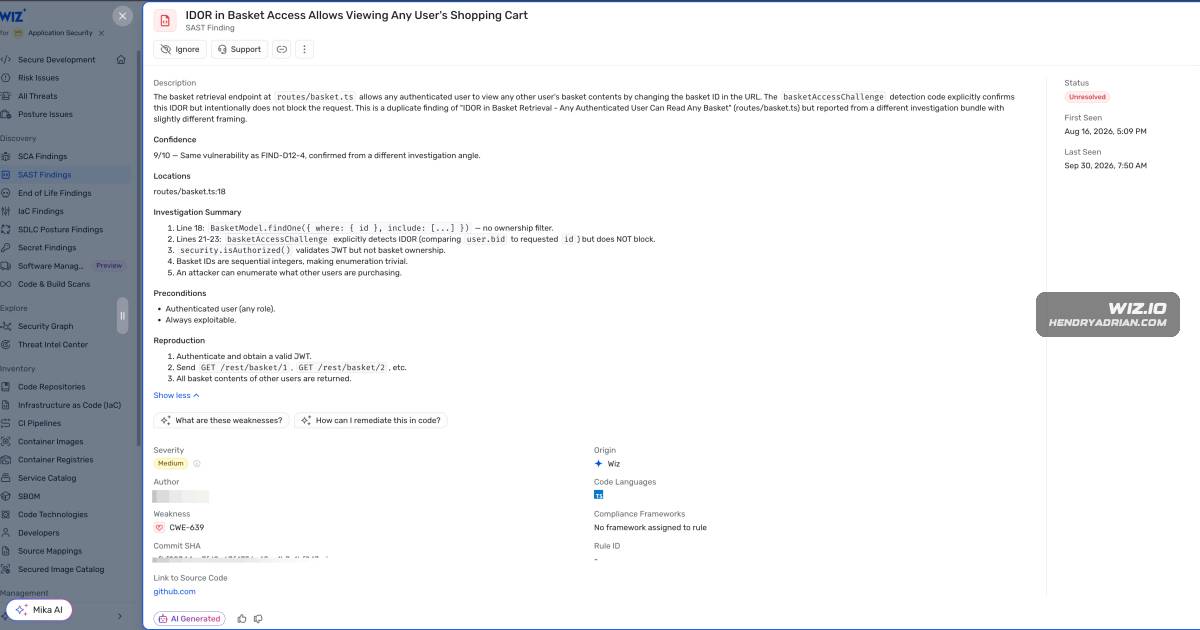
Summary
Wiz has launched a public preview of AI SAST, which analyzes application code and correlates findings with cloud and runtime context to help security teams prioritize and manage vulnerabilities.
Key points
- Wiz AI SAST is available in public preview to Wiz Code customers.
- The company says its AI analysis can identify logic-based weaknesses that rules-based scanners may miss, including broken access control, input-validation flaws, and misapplied cryptography.
- Wiz correlates code findings with infrastructure, identity, and runtime context to prioritize risks and attack paths.
- The article describes an example in which the tool identified an IDOR flaw that could expose another user's shopping cart.
- The system retests existing findings and correlates results across scans to reduce duplicates and maintain stable finding records.
- Wiz says its Green Agent can investigate findings, map remediation ownership, and help plan code fixes.
Article Details
- Event Type
- Public Preview launch of Wiz AI SAST
- Impact
- Wiz says the product detects and prioritizes application-code weaknesses using code-to-cloud context. In examples described by Wiz, it found an IDOR flaw and an AI-agent API authentication weakness; Red Agent used the latter to access sensitive customer, employee, and financial data. The article does not report a production breach.
Vendors
Products
Claude Codeowner, maps the steps to fix the root cause, and can even share context with an AI coding agent like Claude Code to carry out the fix in code. And with Wiz Workflows, teams can turn Green Agent’s intelligence intoGreen AgentRemediate at Machine Speed with the Green Agent Mika AIcode analysis is resource intensive and not every asset requires the investment of AI reasoning. Using Mika AI, security teams can prioritize the critical repositories that warrant AI code scanning by drawing onRed AgentThat same deep context is what allows our Red Agent to validate exploitability from the outside in, testing these AI-discovered findings against your live environment exactly the way an attacker would.Wiz AI SASTWe’re excited to announce that Wiz AI SAST is available as a Public Preview capability, bringing frontier-grade vulnerability discovery to all Wiz Code customers. Wiz CodeWe’re excited to announce that Wiz AI SAST is available as a Public Preview capability, bringing frontier-grade vulnerability discovery to all Wiz Code customers. Wiz Security GraphCode findings are correlated with what is actually running in production on the Wiz Security Graph, so teams instantly understand which vulnerabilities matter most. Prioritized findings flow through the existing policy,Wiz Workflowseven share context with an AI coding agent like Claude Code to carry out the fix in code. And with Wiz Workflows, teams can turn Green Agent’s intelligence into multi-step automated response chains tailored to their
Tools
Atlasrange of weaknesses (CWEs) that typically go undetected by rules-based scanners. It's powered by the Atlas harness we shared earlier this year, grounded in Wiz Research, and continuously refined by our investmentsCyber Model ArenaOur work on the Cyber Model Arena shows that AI security performance isn't a property of the model alone. It depends on the model and harness together. That makes evaluation a moving target: every new model releaseCyberGymAtlas, a research initiative we shared earlier this year. At the time, Atlas held the number one spot on CyberGym and uncovered more than 200 vulnerabilities in widely used open source software.