Cybersecurity Roundup Covers ShinyHunters Claims, Malware Campaigns and Espionage
Summary
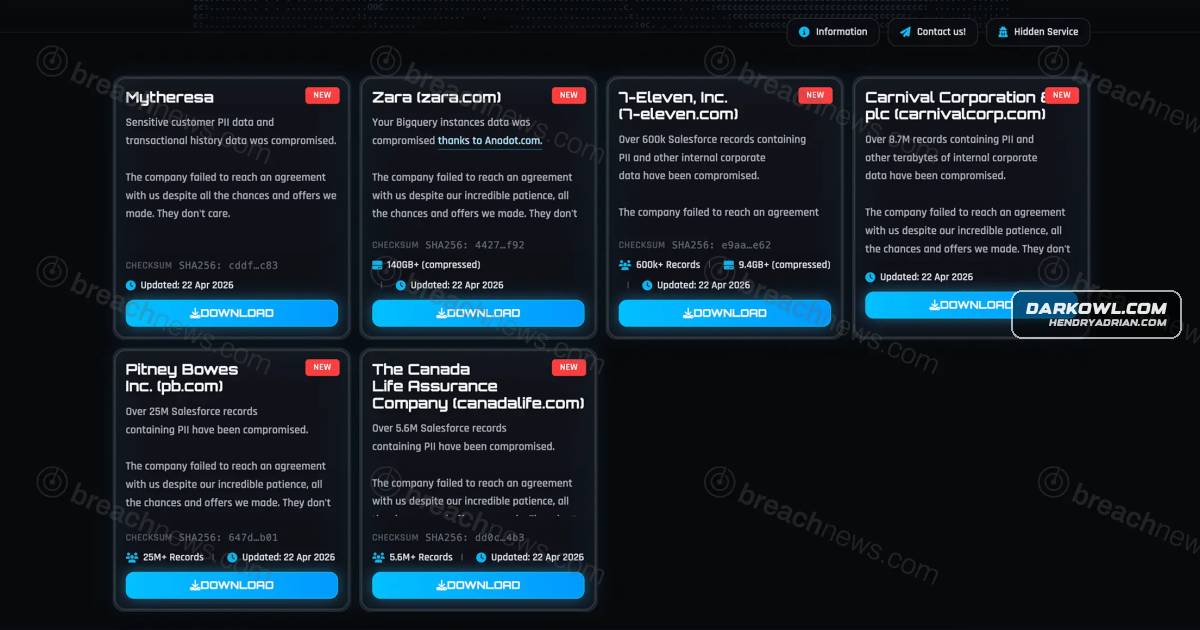
A monthly roundup covers alleged ShinyHunters data theft, a French data-breach arrest, malware on Hugging Face and OpenVSX, espionage campaigns, and the arrest of Dream Market’s suspected administrator.
Key points
- ShinyHunters claimed to have stolen records linked to 8,800 schools and universities from education technology company Instructure; the article describes the claim as alleged.
- French authorities detained a 15-year-old suspect over the France Titres (ANTS) data breach, involving the alleged sale of millions of records.
- A fake OpenAI repository on Hugging Face delivered Windows infostealer malware and reportedly received more than 200,000 downloads before removal.
- Researchers said 6 of 73 GlassWorm extensions on OpenVSX had been activated to deliver malware, while the rest were dormant.
- China-linked groups were reported targeting Asian governments and other organizations through vulnerable Exchange and IIS servers, web shells, and malware; FamousSparrow was also linked to repeated Exchange intrusions at an Azerbaijani energy company.
- German authorities arrested the suspected former Dream Market administrator, who faces U.S. money-laundering charges related to alleged transfers of more than $2 million.
Article Details
- Event Type
- Cybersecurity news roundup covering alleged data breaches, cyber espionage, malware distribution, and law-enforcement actions.
- Impact
- Reported incidents include alleged theft of student and staff records from educational institutions and data belonging to multiple companies; espionage targeting government and defense organizations; malware delivery through a repository and software extensions; and exploitation of an Azerbaijani oil and gas company. The roundup also reports arrests and charges related to cybercrime and money laundering.
People
breach3dAlias used by the 15-year-old suspect detained in connection with the France Titres (ANTS) data breach; the source says the suspect was selling records allegedly stolen in the breach.Owe Martin AndresonIdentified in the article as the alleged former Dream Market administrator arrested in Germany and charged with money laundering.
Threat Actors
CL-STA-0049Named cluster reported to have network overlap with SHADOW-EARTH-053.Earth AluxNamed threat group reported to have network overlap with SHADOW-EARTH-053.FamousSparrowChinese-affiliated threat group linked to repeated Microsoft Exchange exploitation against an Azerbaijani oil and gas company.REF7707Named cluster reported to have network overlap with SHADOW-EARTH-053.SHADOW-EARTH-053Tracked threat cluster described as conducting an espionage campaign against government and defense sectors; the article reports network overlap with CL-STA-0049, Earth Alux, and REF7707.ShinyHuntersThreat group that claimed responsibility for stealing records from Instructure and released data it said belonged to multiple organizations.
Malware
Deed RATThe attack enabled the staged deployment of two separate backdoors across three infection waves: Deed RAT (also known as Snappybee), a ShadowPad successor leveraged by several China-linked espionage groups, andGlassWorm6. GlassWorm malware attacks return via 73 OpenVSX “sleeper” extensions – Bleeping ComputerGodzillaOnce inside, they install web shells (GODZILLA) to maintain control over the system.ShadowPadThey then deploy more advanced malware, such as ShadowPad, using DLL sideloading techniques that hide malicious code inside legitimate, signed programs.SNAPPYBEEthe staged deployment of two separate backdoors across three infection waves: Deed RAT (also known as Snappybee), a ShadowPad successor leveraged by several China-linked espionage groups, and TernDoor, a malwareTernDoor(also known as Snappybee), a ShadowPad successor leveraged by several China-linked espionage groups, and TernDoor, a malware strain recently identified in campaigns targeting telecommunications infrastructure in South
Vendors
Instructure1. Instructure hacker claims data theft from 8,800 schools, universities – Bleeping ComputerMicrosoftThis group takes advantage of known, already-patched vulnerabilities in internet-facing Microsoft Exchange and IIS servers to gain initial access.OpenAI4. Fake OpenAI repository on Hugging Face pushes infostealer malware – Bleeping ComputerSalesforceSeveral of the organizations are associated with the groups previous compromise of Salesforce environments.
Products
CanvasUsing Canvas data export feature ShinyHunters was able to harvest “hundreds of gigabytes of user records, messages, and enrollment data”.Hugging Face4. Fake OpenAI repository on Hugging Face pushes infostealer malware – Bleeping ComputerIISThis group takes advantage of known, already-patched vulnerabilities in internet-facing Microsoft Exchange and IIS servers to gain initial access.Microsoft ExchangeThis group takes advantage of known, already-patched vulnerabilities in internet-facing Microsoft Exchange and IIS servers to gain initial access.OpenVSX6. GlassWorm malware attacks return via 73 OpenVSX “sleeper” extensions – Bleeping ComputerPrivacy Filter“The repository had typosquatted OpenAI’s legitimate Privacy Filter release, copied its model card nearly verbatim, and shipped a loader.py file that fetches and executes infostealer malware on Windows machines,” states
Countries
China5. China-Linked Hackers Target Asian Governments, NATO State, Journalists, and Activists – The Hacker NewsFranceFrench authorities have detained a 15-year-old suspect in connection to the cyberattack on France Titres (ANTS).Germany8. US charges suspected Dream Market admin arrested in Germany – Bleeping Computer
Industries
DefenseChina-linked hackers have conducted an espionage campaign against government and defense sectors in South, East, and Southeast Asia, as well as a European NATO member.EducationNew posts on ShinyHunters data leak site reveal the threat group allegedly has breached the education technology company Instructure.Energy7. Azerbaijani Energy Firm Hit by Repeated Microsoft Exchange Exploitation – The Hacker NewsGovernmentChina-linked hackers have conducted an espionage campaign against government and defense sectors in South, East, and Southeast Asia, as well as a European NATO member.Telecommunicationsespionage groups, and TernDoor, a malware strain recently identified in campaigns targeting telecommunications infrastructure in South America.