Iran-Linked Hackers Disrupt UK Power Plant and US Wastewater Facilities
Summary
Iran-linked hackers reportedly took a UK power plant offline for four days and disrupted wastewater facilities in 12 US states. The article says exposed systems and default credentials enabled access, and urges operators to monitor threats and secure internet-facing OT.
Key points
- A UK power plant was offline for four days in July 2026; the facility’s identity was not disclosed, and the wider UK power supply was unaffected.
- Wastewater treatment facilities across 12 US states reportedly suffered intrusions, causing loss of water pressure and flooding at multiple sites.
- Attackers reportedly accessed programmable logic controllers by scanning for exposed devices and using unchanged default credentials.
- The FBI attributed the activity to malicious cyber actors; US government sources pointed to Iran as the likely origin. No group formally claimed responsibility for either incident.
- The article links the activity to actors reportedly affiliated with CyberAv3ngers and the IRGC, while noting that public confirmation of the UK incident was not provided by the NCSC.
- The article recommends auditing internet-facing PLCs and ICS components for default or reused credentials and unnecessary exposure, and monitoring dark web and hacktivist channels for early warning.
Article Details
- Victim Organization
- Undisclosed UK power plant and wastewater treatment facilities across twelve US states
- Incident Type
- Intrusions into operational technology and industrial control systems, including access to programmable logic controllers, causing power-plant downtime and wastewater-system disruption
- Operational Impact
- The UK power plant was offline for four days in July 2026; the wider UK power supply was not affected. Wastewater facilities across twelve US states experienced loss of water pressure and flooding at multiple sites.
- Ransom Or Extortion
- None reported.
- Claim Status
- confirmed
Threat Actors
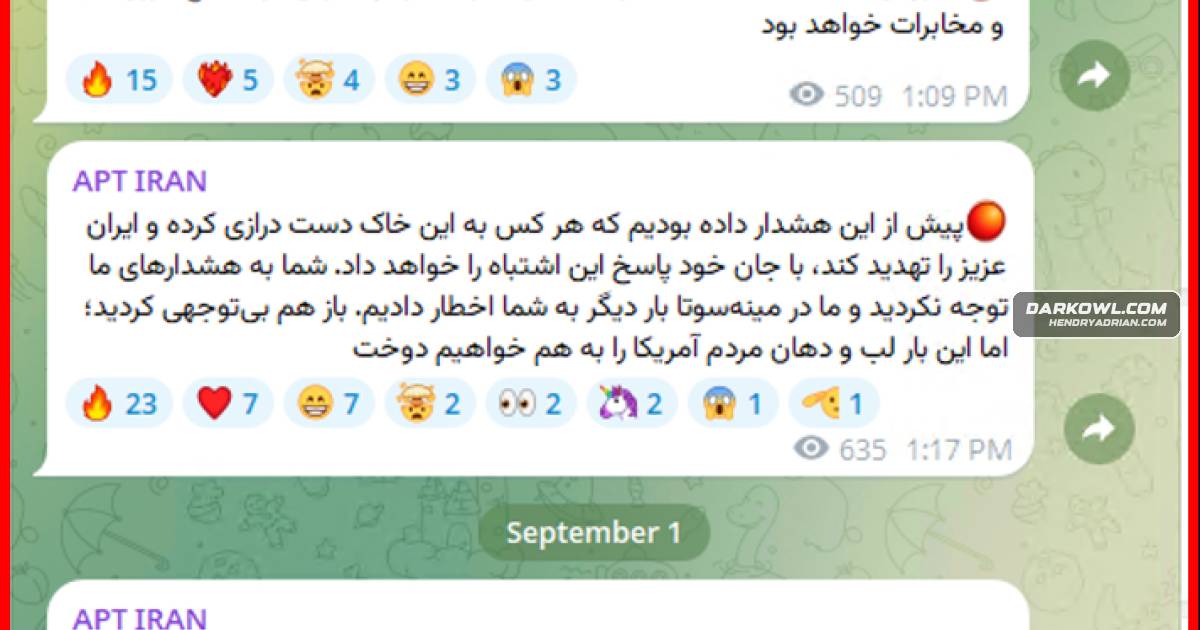
APT IRANNamed group whose Telegram channel threatened the United States; the article does not attribute either incident to the group.CyberAv3ngersReportedly affiliated with the Iran-linked actors associated with the incidents; the article does not say the group claimed responsibility.IRGCThe article describes CyberAv3ngers as affiliated with the IRGC and says the IRGC has a documented history of targeting operational technology at Western utilities.
Countries
IranIn back-to-back incidents this summer, Iran-linked hackers showed the world how quickly online rhetoric turns into physical disruption, and how thin the line has become between the operational technology that keeps theUnited KingdomIn back-to-back incidents this summer (2026), Iran-linked hackers took down a small-scale power plant in the United Kingdom and disrupted wastewater treatment facilities across a dozen US states.United States8/30/2026 1:09 PM] APT IRAN: 🔴 “Soon, the United States will witness unexpected and critical incidents in the energy, water, and telecommunications industries.”
Industries
Energy8/30/2026 1:09 PM] APT IRAN: 🔴 “Soon, the United States will witness unexpected and critical incidents in the energy, water, and telecommunications industries.”Telecommunications8/30/2026 1:09 PM] APT IRAN: 🔴 “Soon, the United States will witness unexpected and critical incidents in the energy, water, and telecommunications industries.”waterthe operational technology that keeps the lights on and the industrial control systems that keep the water running.