
N0n Claims Theft of Chibitek Client Data
Summary
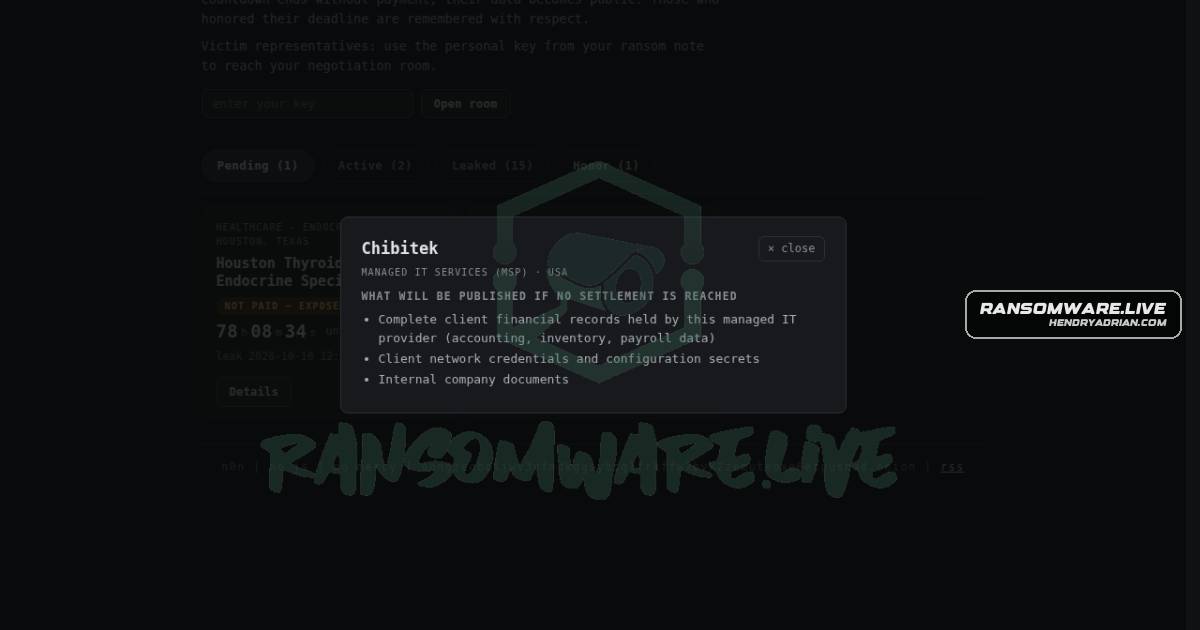
Ransomware group N0n claims it stole Chibitek client financial records, network credentials, configuration secrets, and internal documents. The claim says the data was exposed on October 11, 2026; it is unverified.
Key points
- N0n claims it targeted Chibitek, a US managed IT services provider.
- The group claims to have stolen client accounting, inventory, and payroll records, along with network credentials, configuration secrets, and internal documents.
- The claim says the data was exposed on October 11, 2026, and that no payment was made.
- The post states that the claims are unverified. No official statement from Chibitek is included.
Article Details
- Victim
- Chibitek
- Claim Date
- 2026-10-07
- Encryption Status
- Unknown
- Exfiltration Status
- Claimed by N0n; not independently confirmed
- Exfiltrated Data
- N0n claims it stole client financial records, including accounting, inventory, and payroll data, as well as client network credentials, configuration secrets, and internal company documents.
- Ransom Demand
- Not disclosed
- Leak Status
- Claimed exposed on 2026-10-11 04:43 UTC; the source says the information is based on public claims and cannot confirm their accuracy.