Wiz Previews Exposure Management Dashboard for CTEM and AI-Speed Remediation
Summary
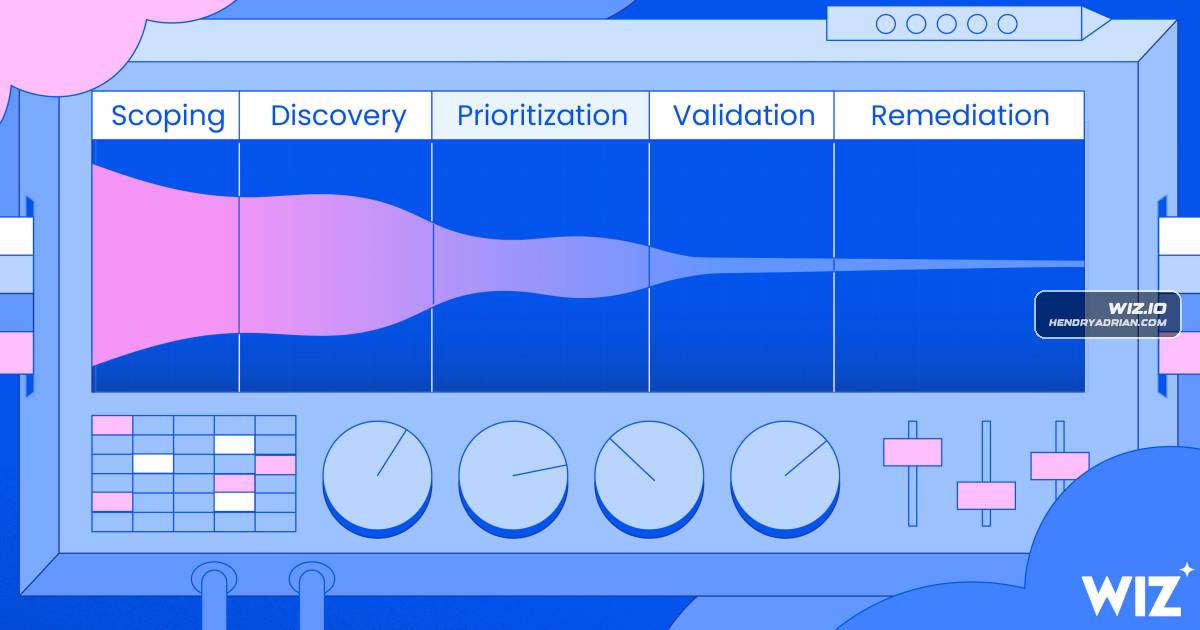
Wiz has launched a public preview of its Exposure Management Dashboard, which organizes CTEM workflows for scoping, discovery, prioritization, validation, and remediation, using platform agents to help teams manage security risks.
Key points
- The dashboard brings asset and risk information together across cloud, code, on-premises systems, AI workloads, workstations, identities, and SaaS.
- It groups risks into attack paths with business context to help teams prioritize issues over alert volume.
- Wiz ASM and its Red Agent can validate whether attack paths are exploitable from outside the environment.
- The Green Agent supports investigation, root-cause analysis, ownership mapping, and remediation; Wiz Workflows can automate response steps.
- The dashboard is in public preview and is available through the Wiz Preview Hub.
Article Details
- Event Type
- Wiz announced the Exposure Management Dashboard, now in Public Preview.
- Impact
- The dashboard is designed to unify security-risk visibility and support prioritization, validation, and remediation across the CTEM lifecycle, including through Wiz platform agents and integrations. Wiz says it aims to help teams reduce mean time to remediation and keep pace with AI-accelerated vulnerability discovery and exploitation.
Vendors
Products
Exposure Management Dashboardfor security and vulnerability management to keep up with AI scale and speed with the new Exposure Management Dashboard. Built to help teams operationalize this threat landscape shift, this one-stop shop isJiraexample, automatically triggering a Green Agent investigation on critical Wiz Issues and opening a Jira ticket assigned to the right developer.Red Agentfrom the outside, giving you the attacker’s perspective. Validation is done with Wiz ASM and with the Red Agent- our AI-powered pentester- to test your environment for exploitable risks from the outside, leveragingWiz ASMto be exploitable from the outside, giving you the attacker’s perspective. Validation is done with Wiz ASM and with the Red Agent- our AI-powered pentester- to test your environment for exploitable risks from theWiz Codeenvironment. This includes infrastructure vulnerabilities (cloud and on-prem), code vulnerabilities via Wiz Code and ASPM integrations, pen-test findings, cloud misconfigurations, exposed secrets, sensitive dataWiz Green Agentand issue resolution over time against established SLAs. This stage is supercharged by the Wiz Green Agent, an AI-powered investigation and remediation engine. The Green Agent automatically conductsWiz Security Graphrisks combine across your environment to create an attack path with true business impact on the Wiz Security Graph. The prioritization stage provides you with the Wiz Issues that represent these attack paths,Wiz UVMour cloud and code scanners, while seamlessly ingesting data from your existing third-party scanners via Wiz UVM.Wiz Workflowsmapping to give you the safest and most efficient path to resolution. You can scale this with Wiz Workflows that enable you to automate repeatable response processes-for example, automatically triggering a