
Acronis Finds Small Businesses Exposed to Unsupported Windows and Known-Exploited Vulnerabilities
Summary
Acronis telemetry from more than 1.2 million Windows and macOS machines finds persistent unsupported OS use and overdue patches among small businesses; 66.7% of overdue machines had a CISA KEV-linked patch outstanding.
Key points
- The study analyzed anonymized telemetry from more than 330,000 small-business tenants and 1.2 million Windows and macOS machines from October 2025 through September 2026.
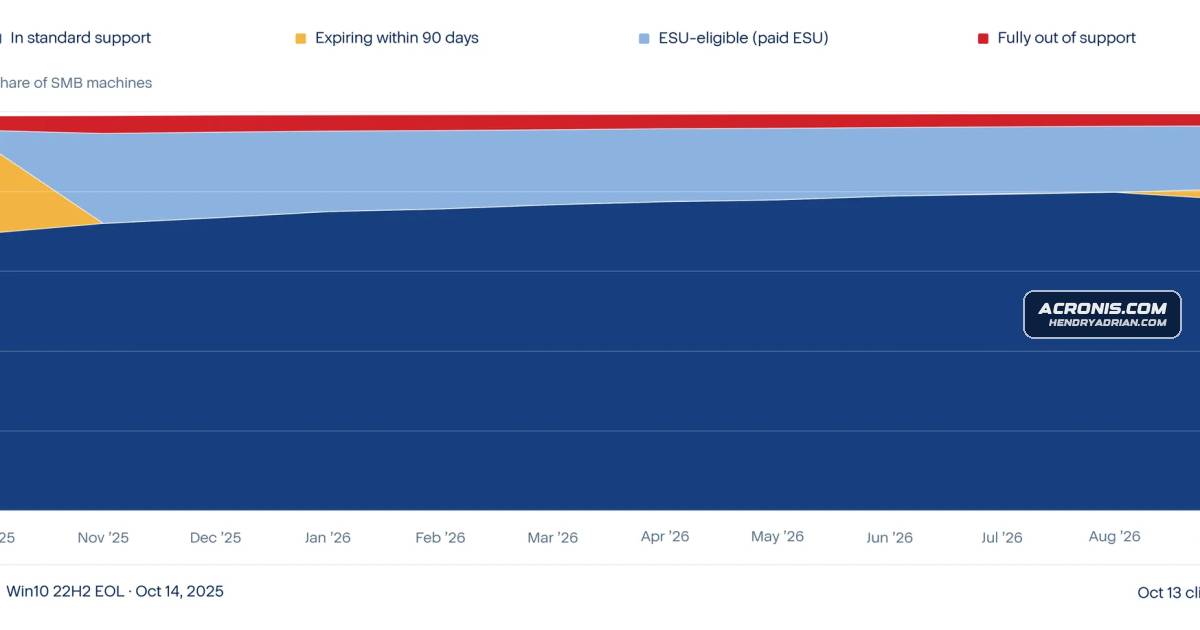
- Based on its September snapshot, the report projected 196,328 machines would lose all patch coverage on October 13, 2026. ESU eligibility does not establish whether a machine was enrolled. The article, dated November 18, describes this deadline as upcoming, although it had passed by then.
- Among nearly 200,000 machines with at least one open, overdue vulnerable patch, 66.7% had a patch linked to a CISA Known Exploited Vulnerability and 33.9% had a patch linked to a ransomware-related KEV.
- Windows 10 22H2 had an overdue-patch rate of 22.9% across all such machines and 48.0% among scanned machines, according to the report.
- Windows 7/8.x and Windows Server 2008/2012 accounted for 3.7% of the fleet; older server versions were more concentrated among the smallest customers.
- Patch-exposure analysis included only machines with Acronis patch management active; 41.7% of Windows SMB machines had a patch-management record, so the report characterizes its overall overdue rates as floor estimates.
- The report recommends migrating unsupported systems, expanding patch management coverage, prioritizing KEV-linked patches, and reviewing OS lifecycles regularly.
Article Details
- Publisher
- Acronis
- Report Period
- October 2025–September 2026; data cut-off October 6, 2026
- Scope
- Anonymized Acronis Cyber Platform telemetry on operating-system support status and overdue vulnerable patches at small businesses with 1–99 managed computers. Patch-exposure analysis covers only machines with Acronis patch management active.
- Sample Size
- More than 330,000 small-business tenants and more than 1.2 million Windows and macOS machines; the September 2026 fleet breakdown lists 1,231,023 machines.
- Key Statistics
- Based on the September 2026 snapshot, 196,328 machines were projected to lose all patch coverage on October 13, 2026.
- Among almost 200,000 Windows machines with at least one overdue vulnerable patch in September 2026, 66.7% had an open patch linked to a CISA Known Exploited Vulnerability (KEV), and 33.9% had an open patch linked to a ransomware-associated KEV.
- Overdue vulnerable patches affected 16.0% of the full SMB Windows fleet; 10.7% had an overdue KEV-linked patch and 5.4% an overdue ransomware-KEV-linked patch.
- In September 2026, 41.7% of Windows SMB machines had an Acronis patch management record; the report says its overdue-vulnerability rates, calculated using the full machine count, are floor estimates.
- Windows 7/8.x and Windows Server 2008/2012 together accounted for 3.7% of the small-business fleet.
- Recommendations
- Audit Windows Server 2012 and 2012 R2 workloads and migrate to Server 2022 or 2025, consolidate, or decommission them before the final ESU year ends on October 13, 2026.
- Deploy patch management to machines that currently have no scan record.
- Prioritize open patches linked to CISA KEV entries and apply KEV patches within 30 days.
- Treat ransomware-linked KEV patches as a critical remediation priority; the report recommends filtering vulnerability output for KEV and ransomware-linked entries.
- Establish quarterly operating-system lifecycle reviews and start upgrade projects 12–18 months before end-of-life deadlines.
Vendors
Products
Acronis Cyber Platform2025 through September 2026 — across more than 330,000 small business customer tenants on the Acronis Cyber Platform, representing more than 1.2 million Windows and macOS machines.Windows 10 22H2are set to lose all patch coverage in a single day. This includes the more than 160,000 machines on Windows 10 22H2 whose ESU Year 1 expires, more than 30,000 machines on Windows Server 2012 and 2012 R2 that exhaustWindows 10 LTSB 2016on Windows Server 2012 and 2012 R2 that exhaust their final ESU year, and almost 1,500 machines on Windows 10 LTSB 2016, which reaches the end of standard extended support with no ESU option available.Windows 7Beyond the three points above, the oldest machines in the fleet, those on Windows 7 and 8.x and on Windows Server 2008 and 2012, are still 3.7% of the fleet. They appear in many markets, but their share of the localWindows Server 2008 R2Windows Server 2008 R2 (build 7601)Windows Server 2012than 160,000 machines on Windows 10 22H2 whose ESU Year 1 expires, more than 30,000 machines on Windows Server 2012 and 2012 R2 that exhaust their final ESU year, and almost 1,500 machines on Windows 10 LTSB 2016,Windows Server 2012 R2expires for commercial customers. Second, the three-year ESU program for Windows Server 2012 and Windows Server 2012 R2 reaches its final day — there are no more paid years available after this date. Third, Windows 10
Countries
Argentinafleet. They appear in many markets, but their share of the local fleet is highest in Turkey, Taiwan, Argentina and Indonesia, and the old server versions tilt toward the smallest customers.BrazilUnited States and Brazil hold the most machines in these two groups. They also have large fleets, so a share view is needed to see where the long tail is thickest. Measured as a share of the local fleet, it is thickestIndonesiaappear in many markets, but their share of the local fleet is highest in Turkey, Taiwan, Argentina and Indonesia, and the old server versions tilt toward the smallest customers.Spainthe local fleet, it is thickest in Turkey (7.3%), Taiwan (6.8%), Argentina (6.3%), Indonesia (5.9%) and Spain (5.8%). Older hardware, slower refresh cycles and tight budgets are the usual reasons small businessesTaiwan3.7% of the fleet. They appear in many markets, but their share of the local fleet is highest in Turkey, Taiwan, Argentina and Indonesia, and the old server versions tilt toward the smallest customers.Türkiyestill 3.7% of the fleet. They appear in many markets, but their share of the local fleet is highest in Turkey, Taiwan, Argentina and Indonesia, and the old server versions tilt toward the smallest customers.United Statesat least one open, overdue, vulnerable patch in September 2026: 66.7% had at least one patch linked to a U.S. CISA Known Exploited Vulnerability (KEV), and 33.9% had an open patch that ransomware actors have actively
Industries
Healthcarecan mean replacing the machine it controls, and a production stop costs more than the risk feels like. Health care is similar: Scanners, lab devices and practice software are often tied to one Windows version by theManufacturingfits how these industries use computers, although the data cannot prove any of the reasons. In manufacturing, old Windows versions often run production equipment, machine controllers and specialist software thatTechnologyexpect from tills and back-office PCs that run one fixed program and are only replaced when they break. Technology shows the opposite: few old desktops but a larger share of old servers. A likely reason is that